One pane of glass. Total security.
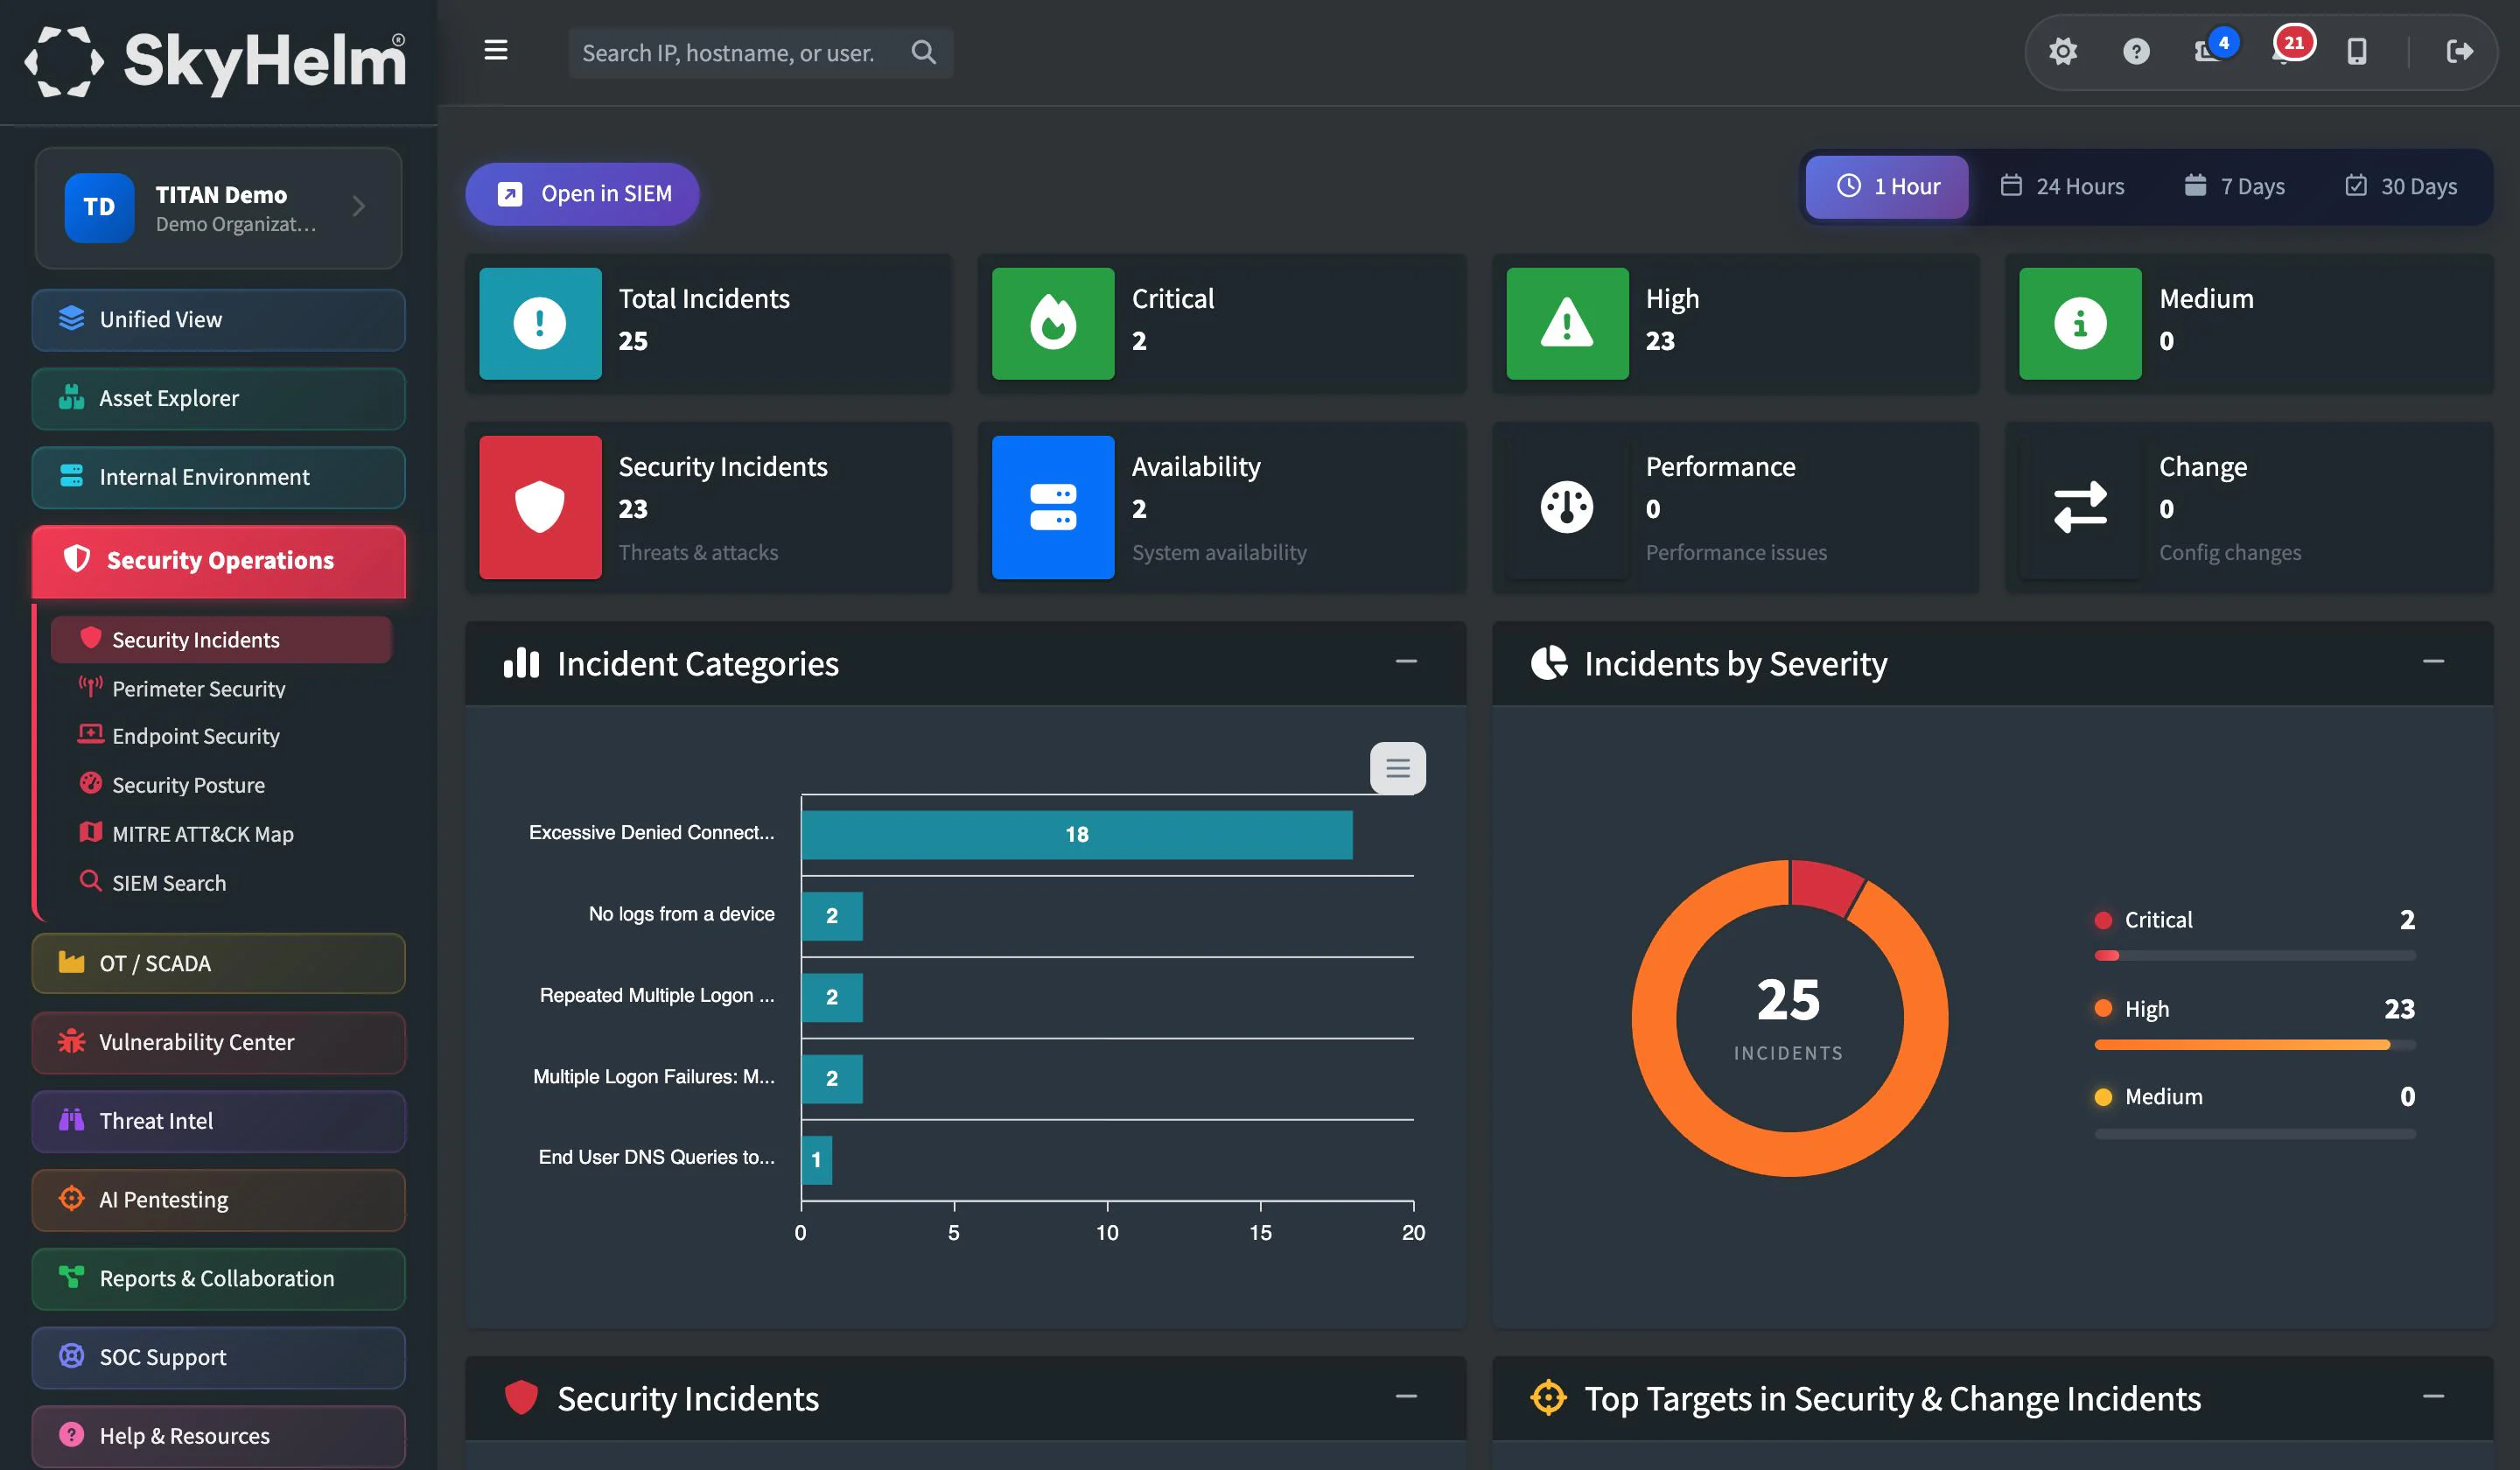
A single security operations platform built for critical infrastructure, from endpoints and SIEM to OT, vulnerabilities, threat intelligence and reporting.
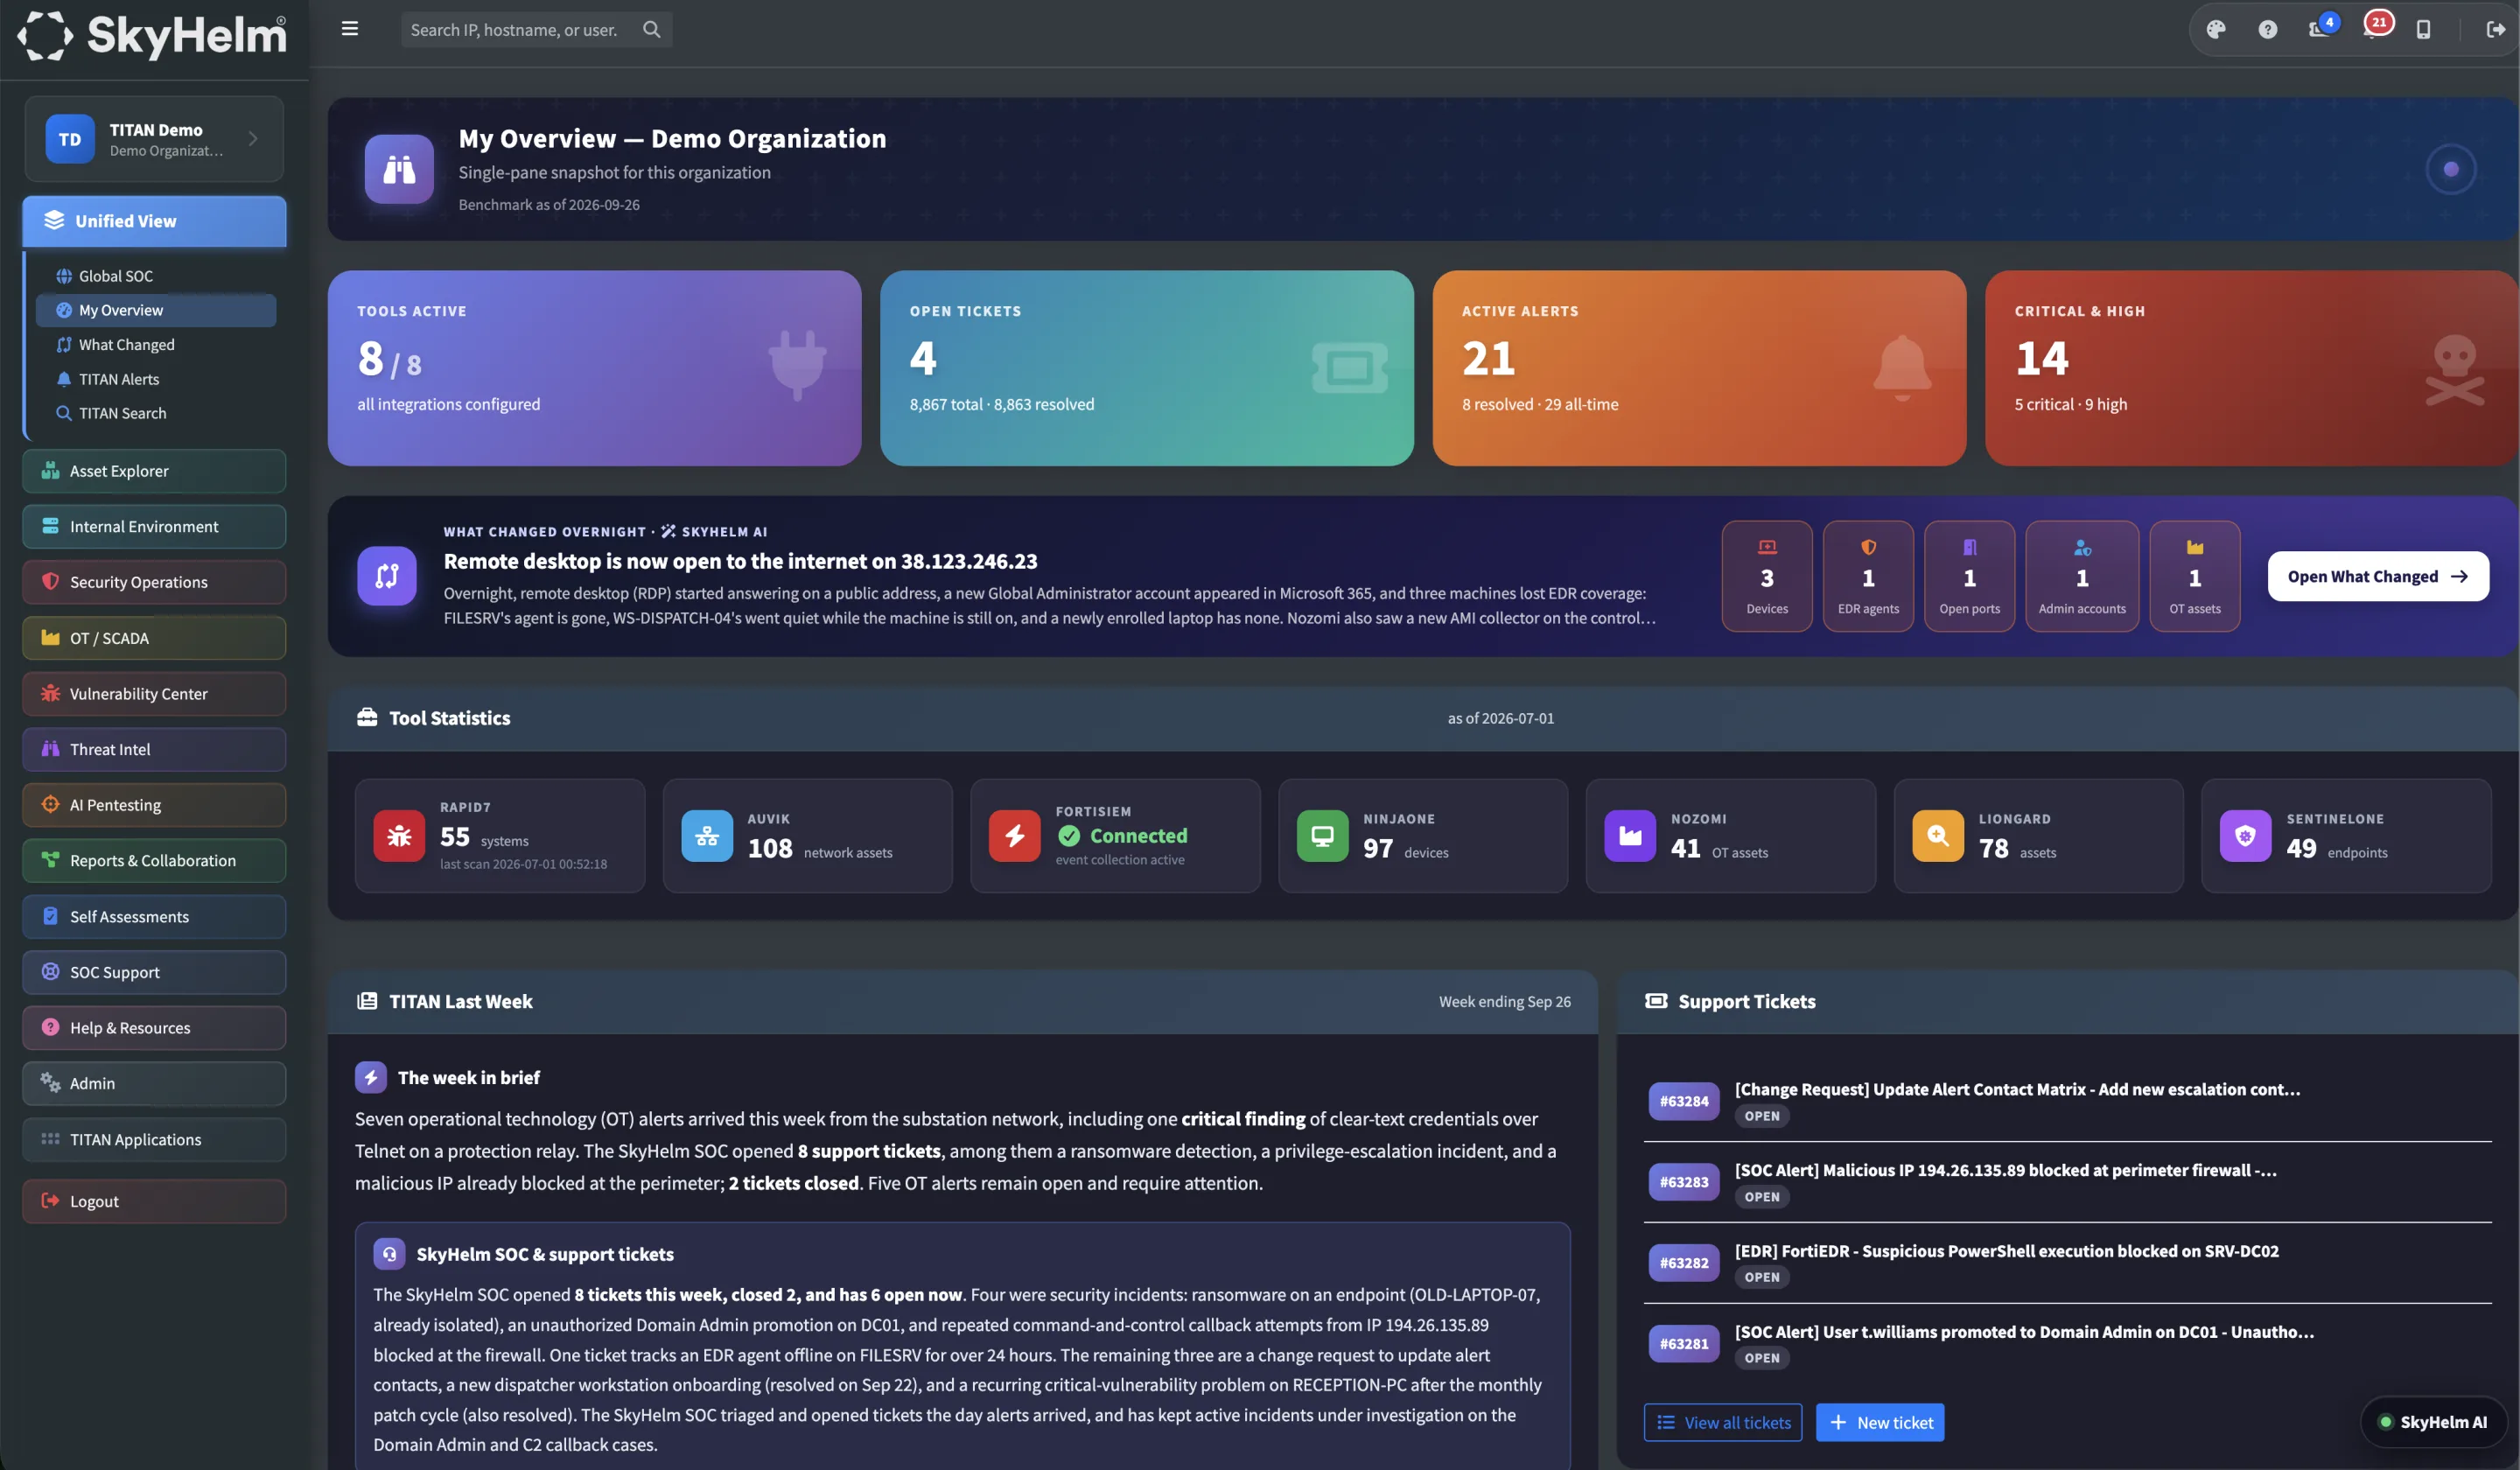
261 capabilities, built for critical infrastructure. Correlated, risk-ranked and presented in context, so your team sees what matters first.
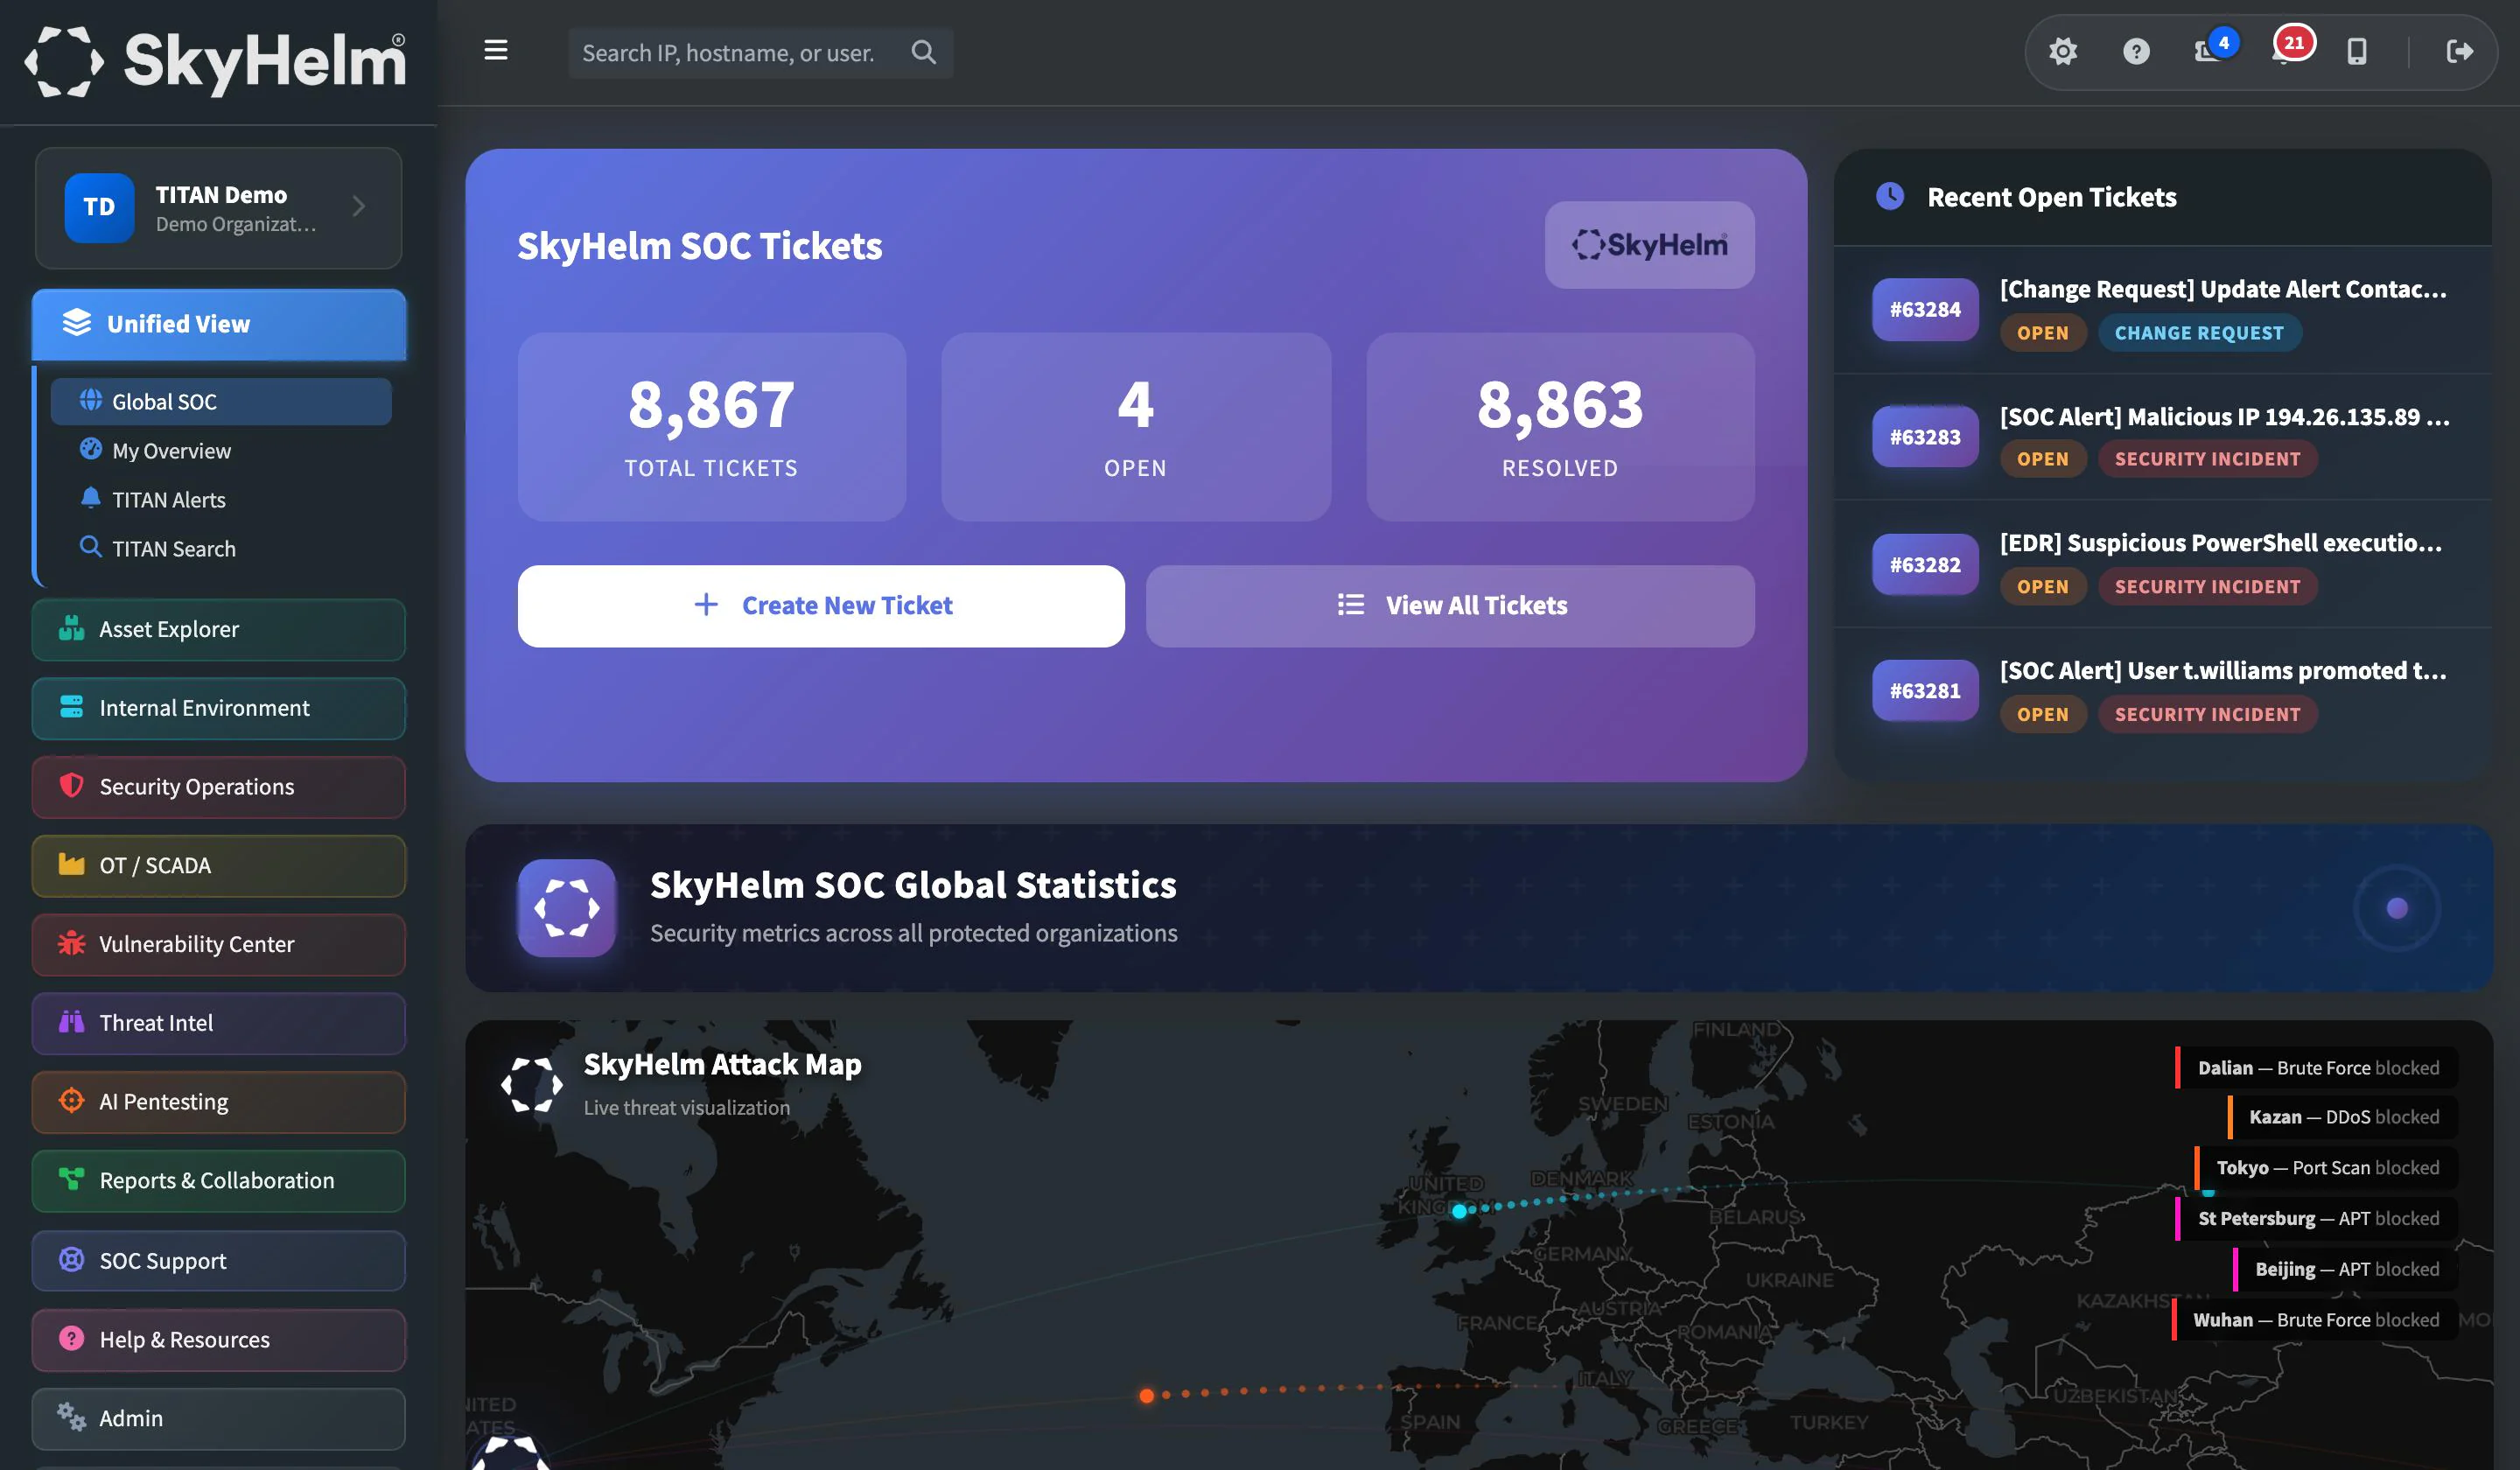
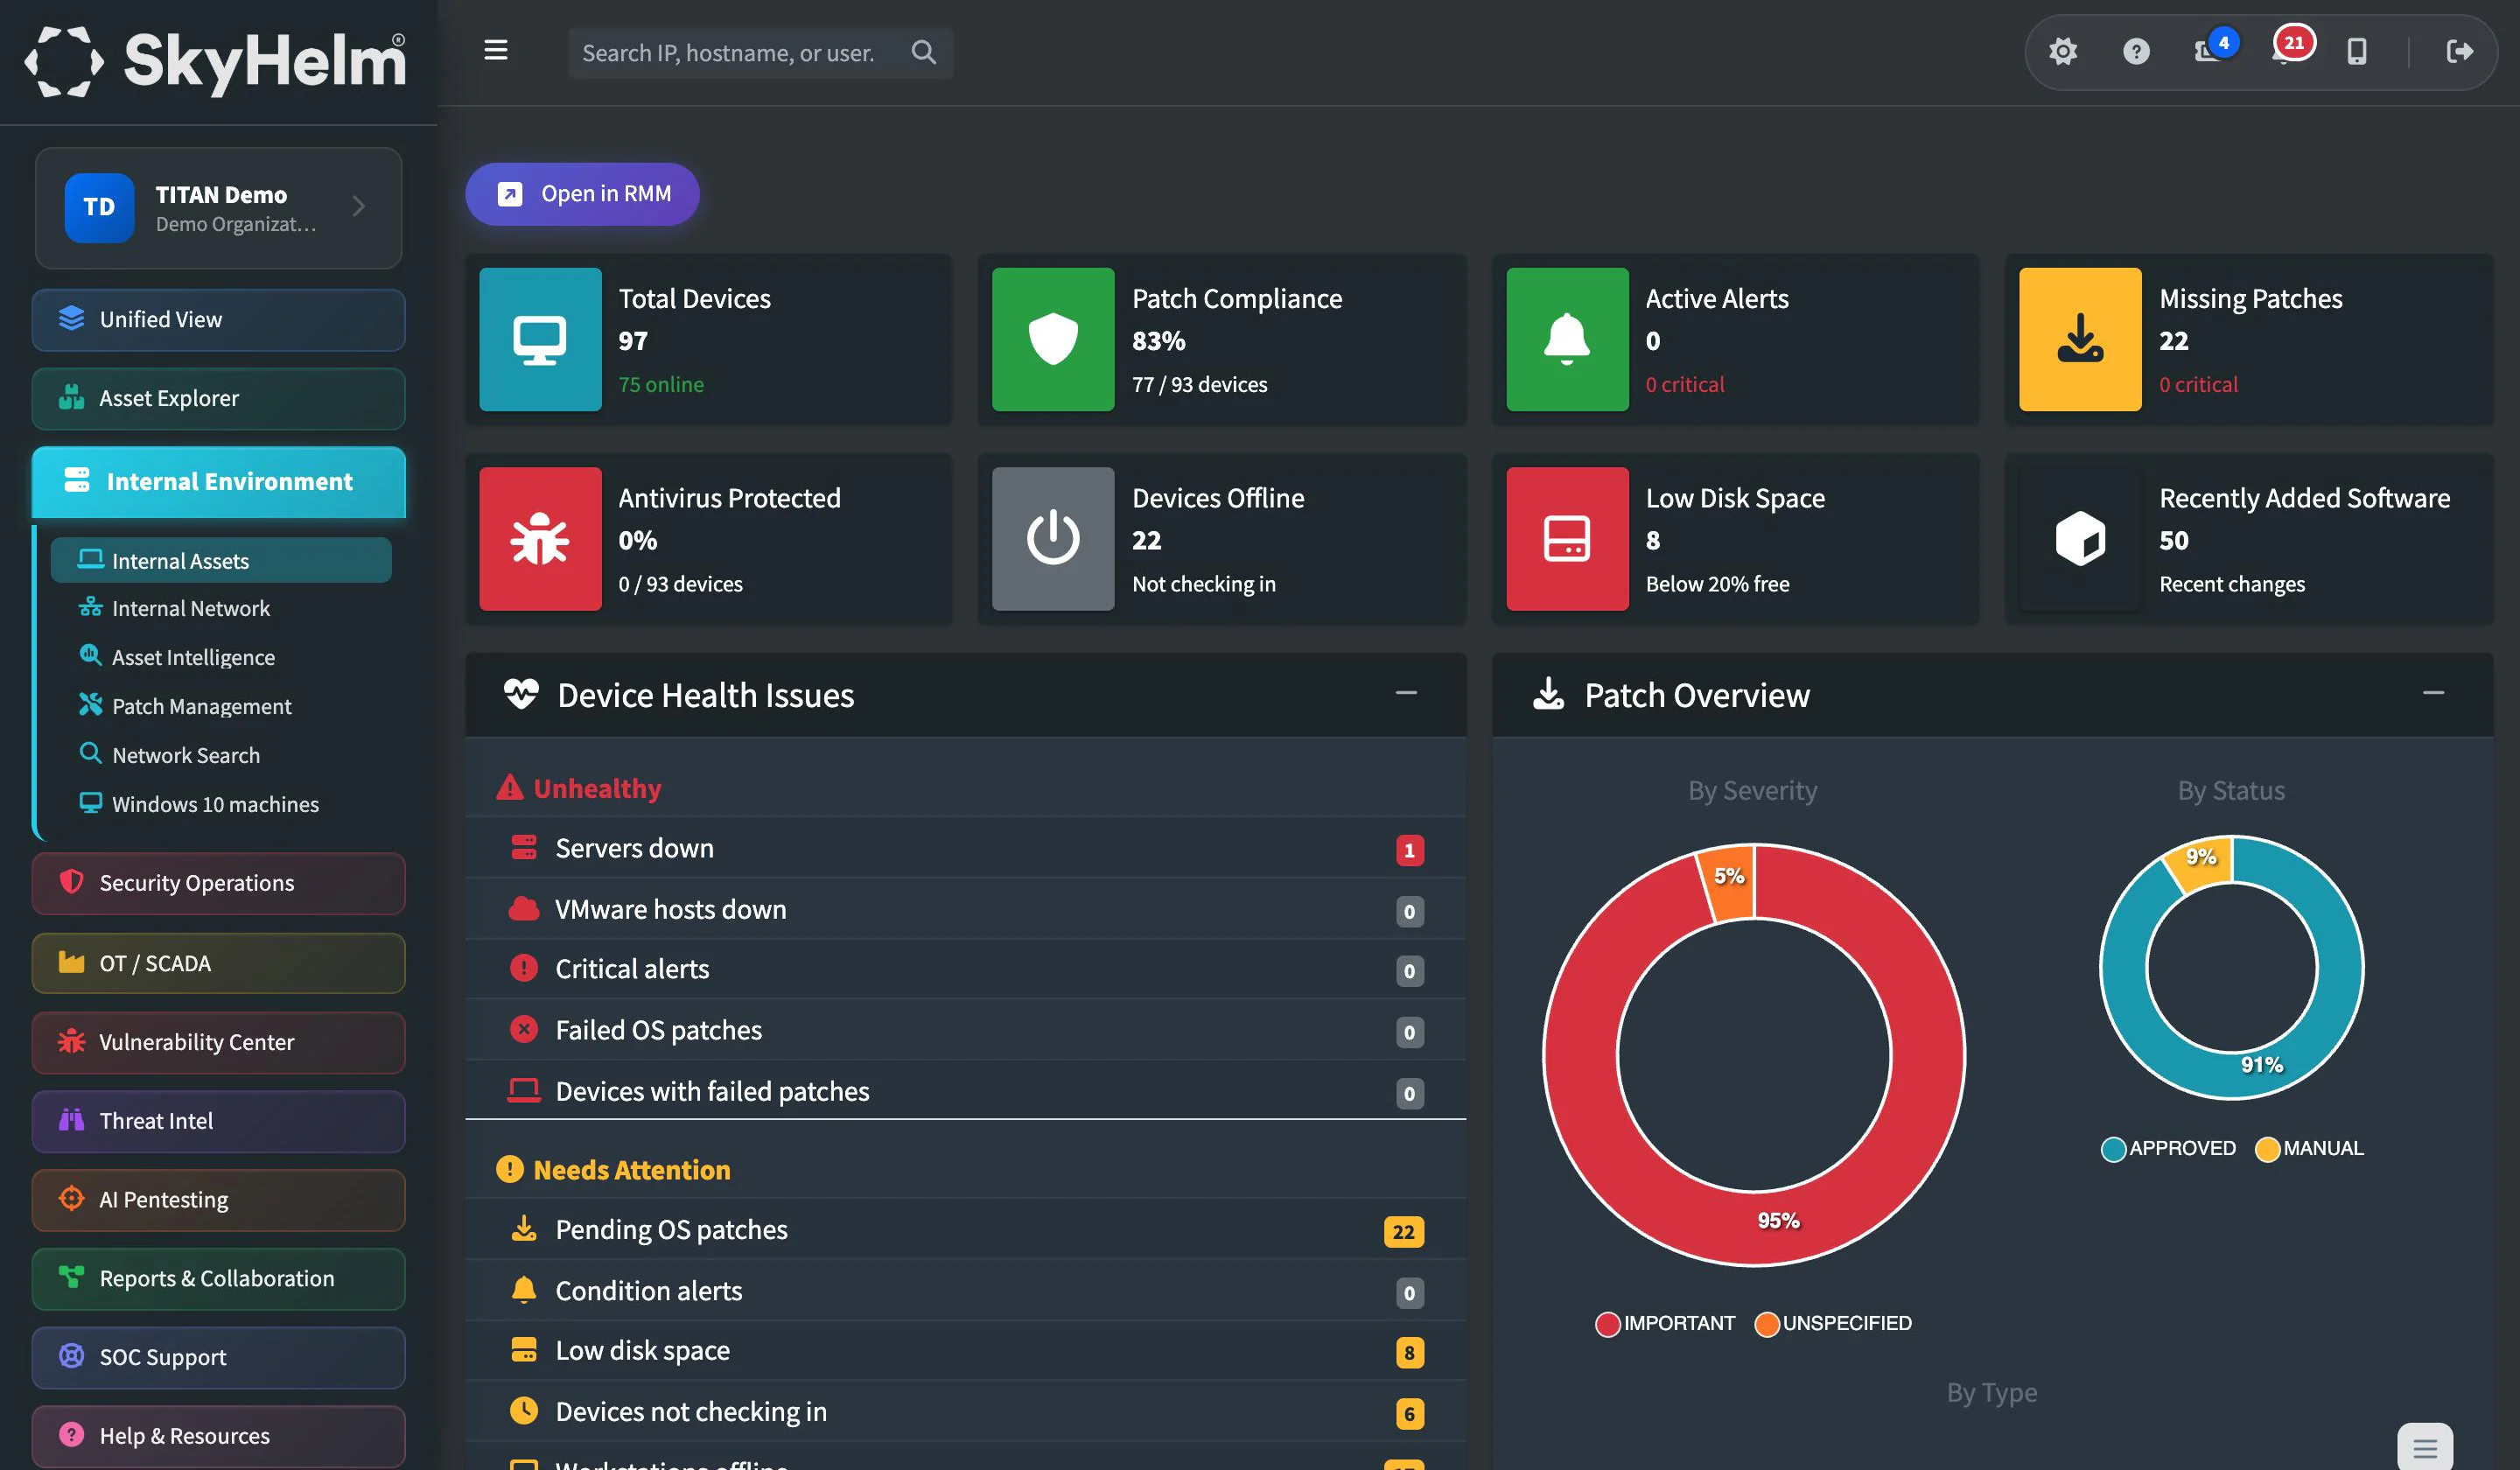
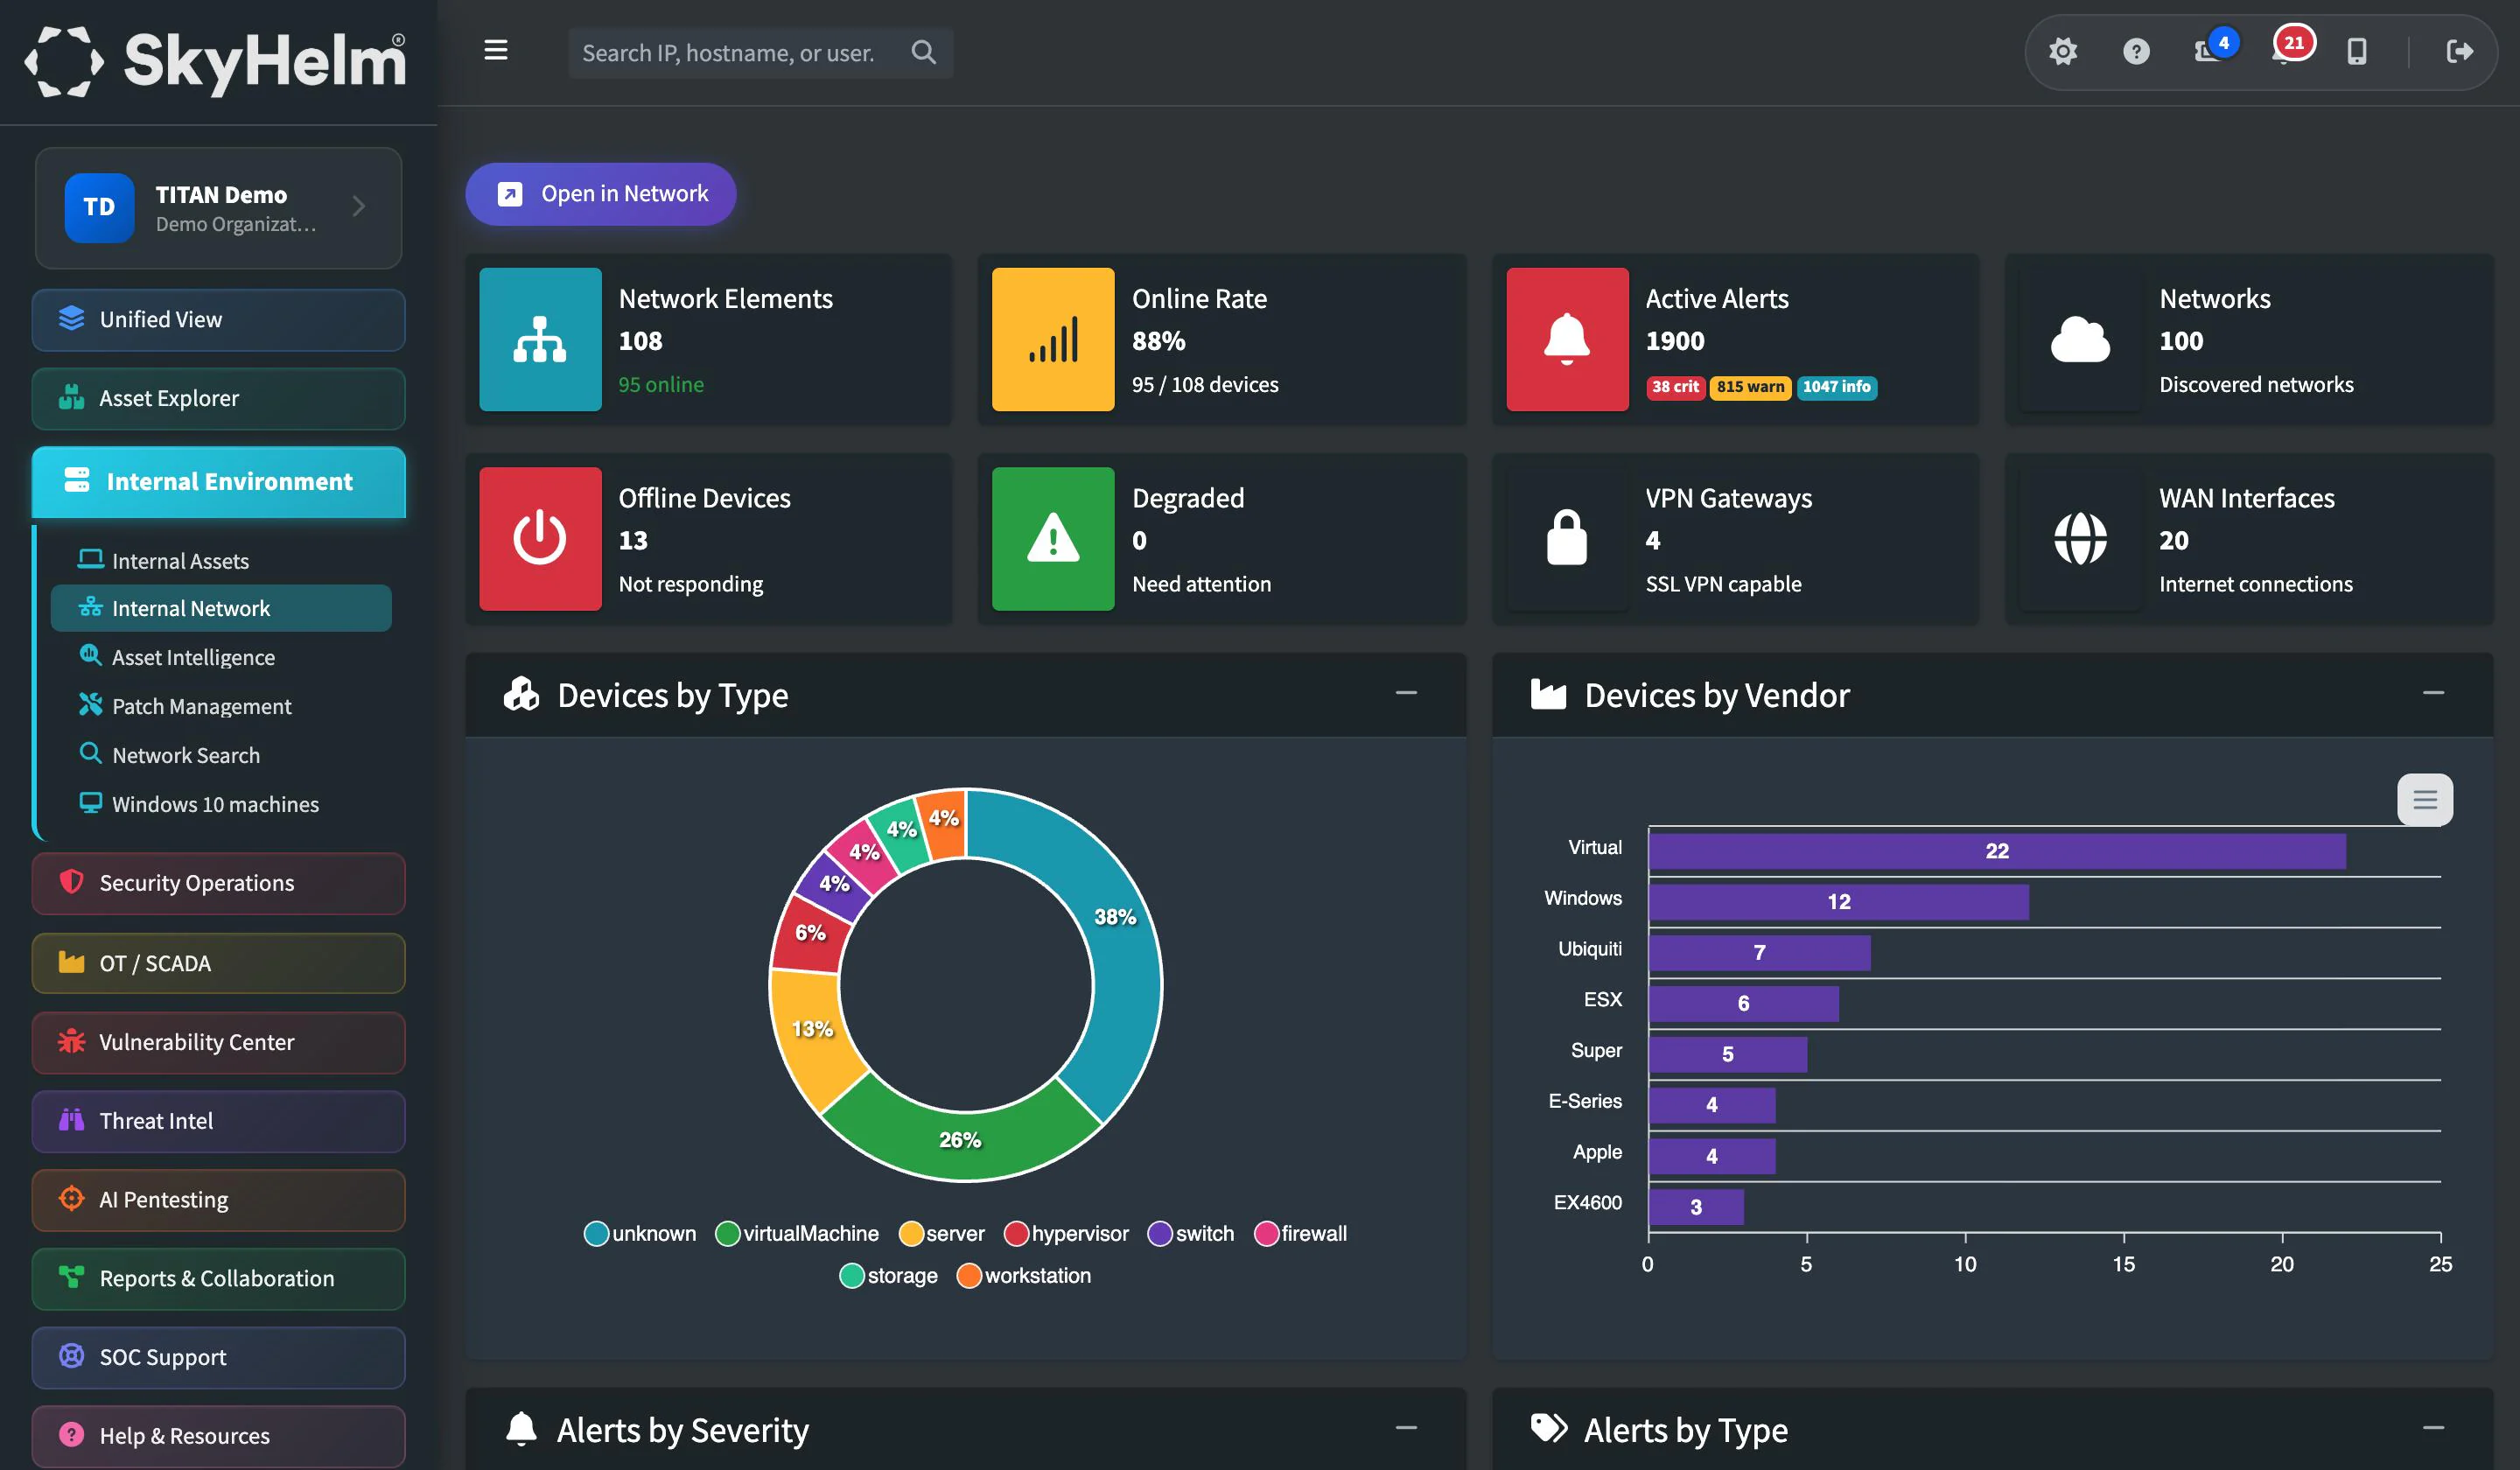
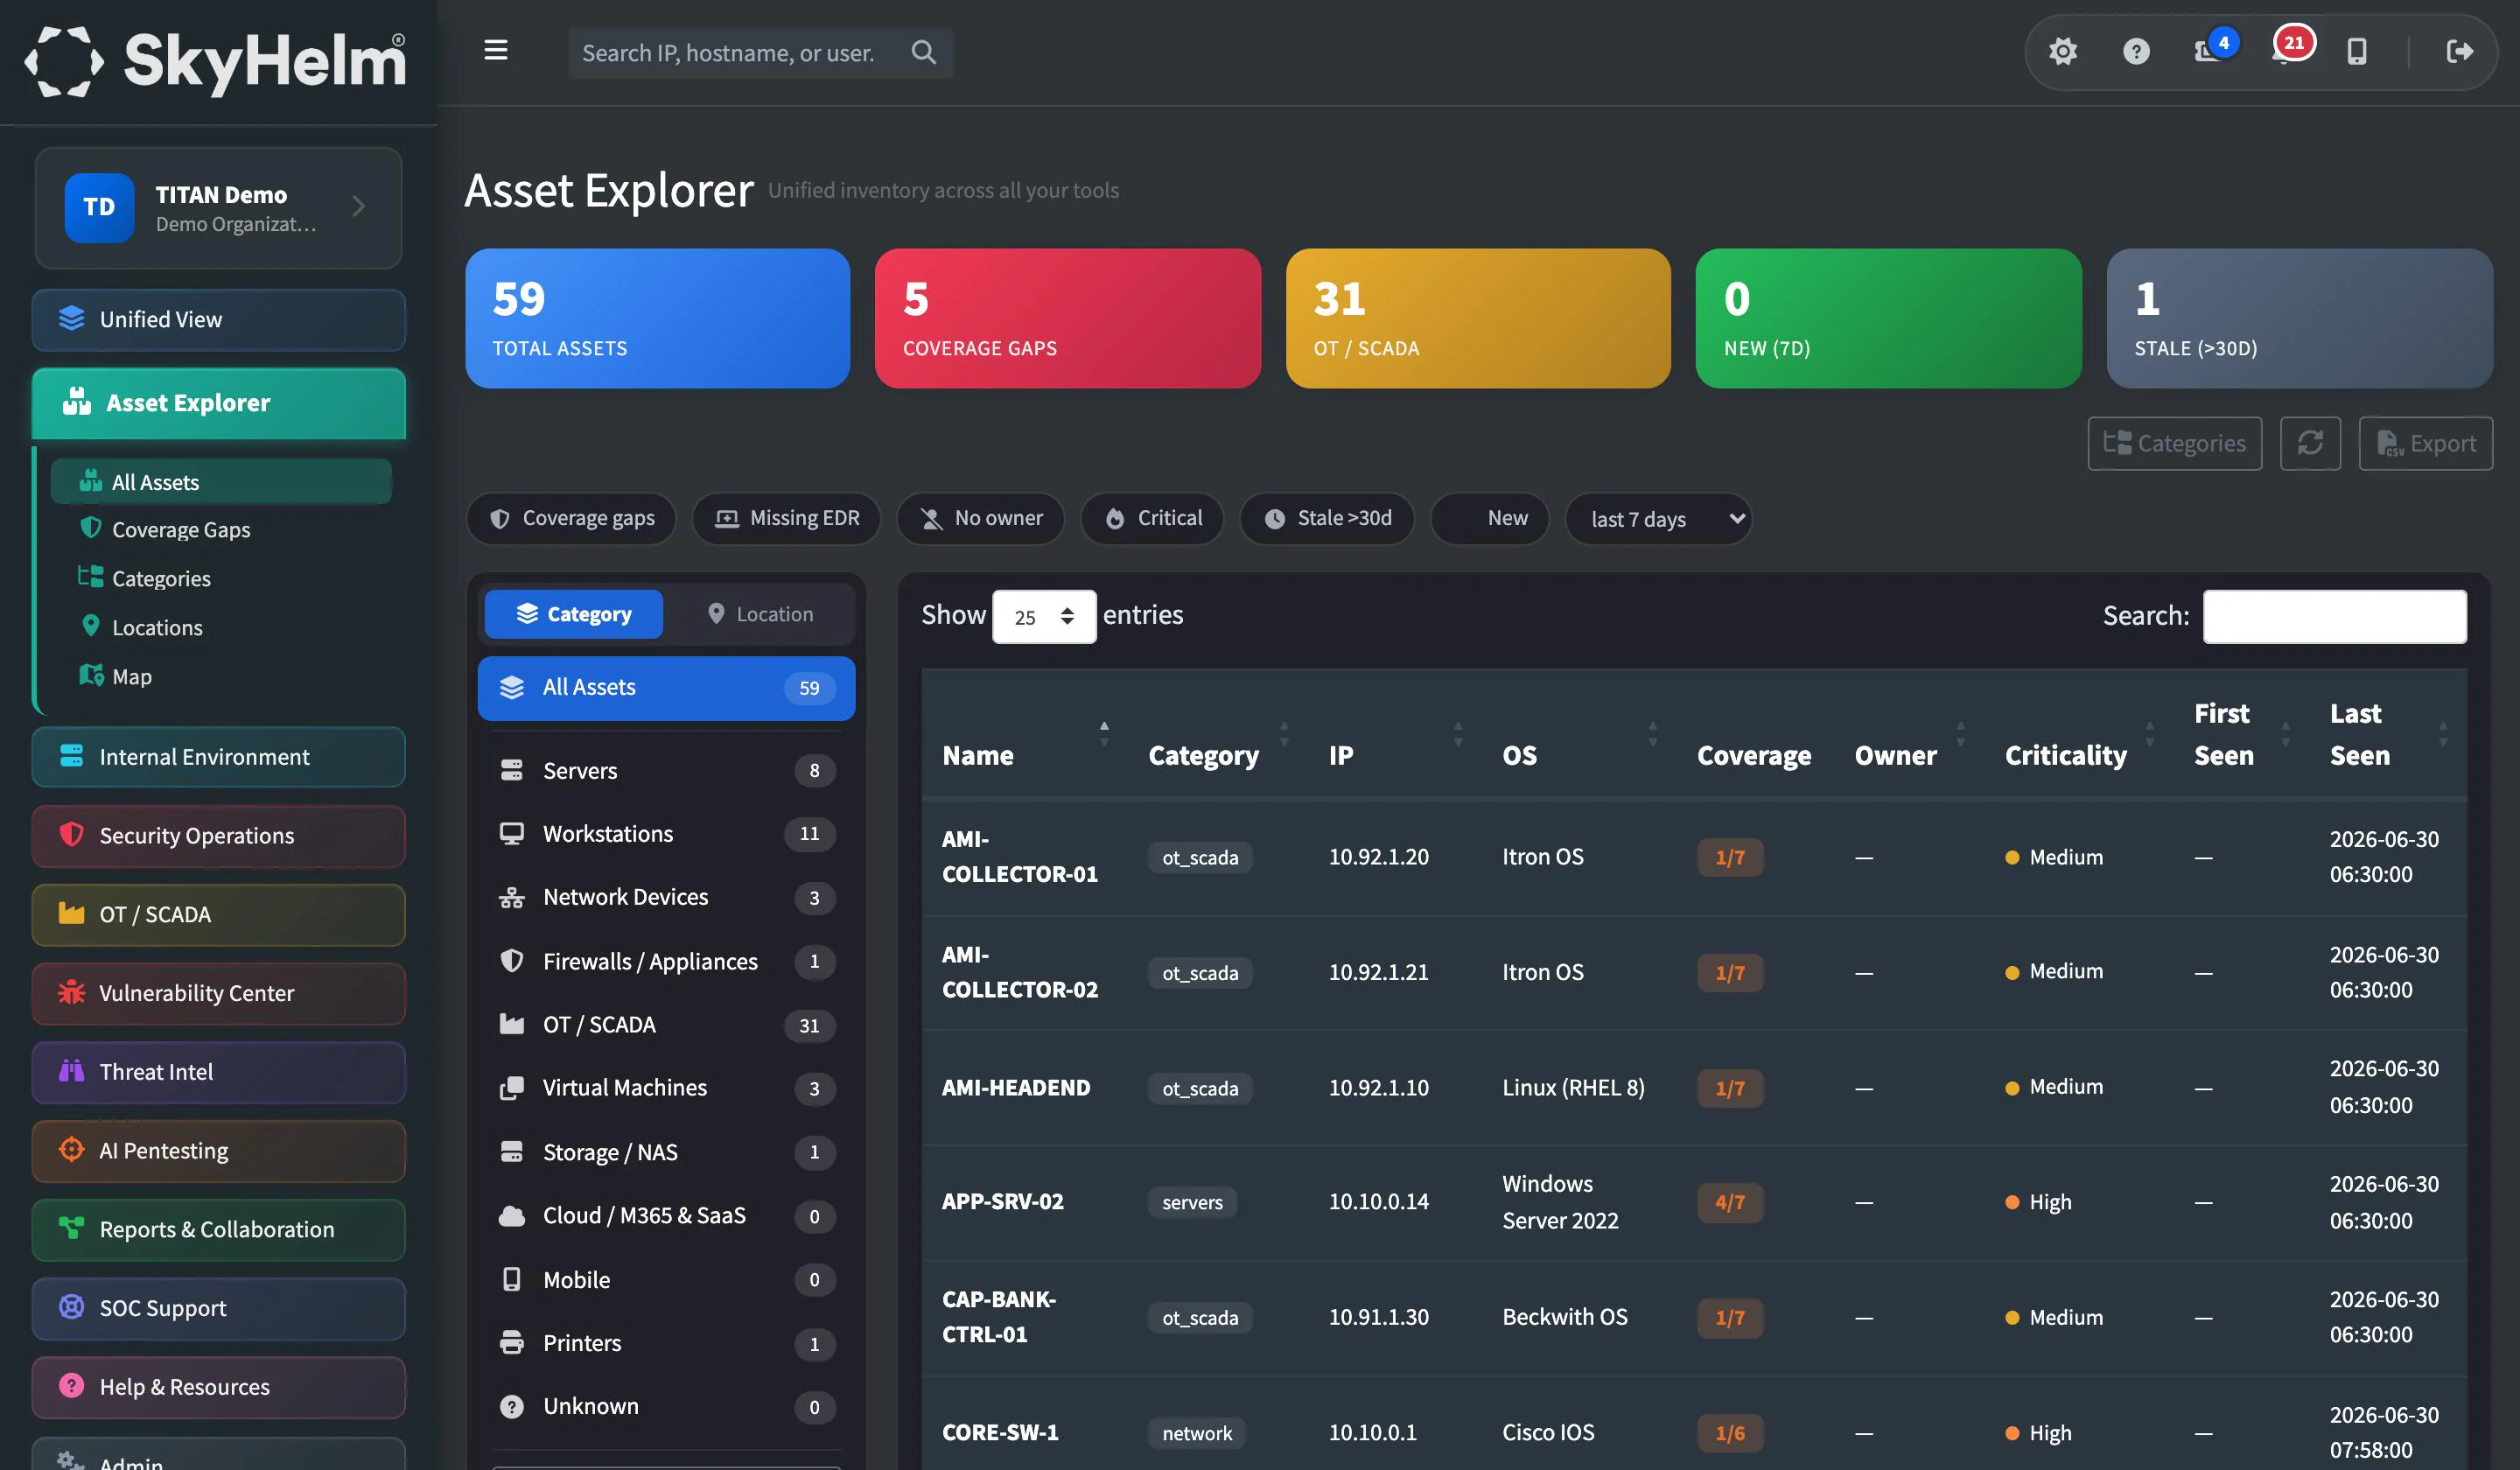
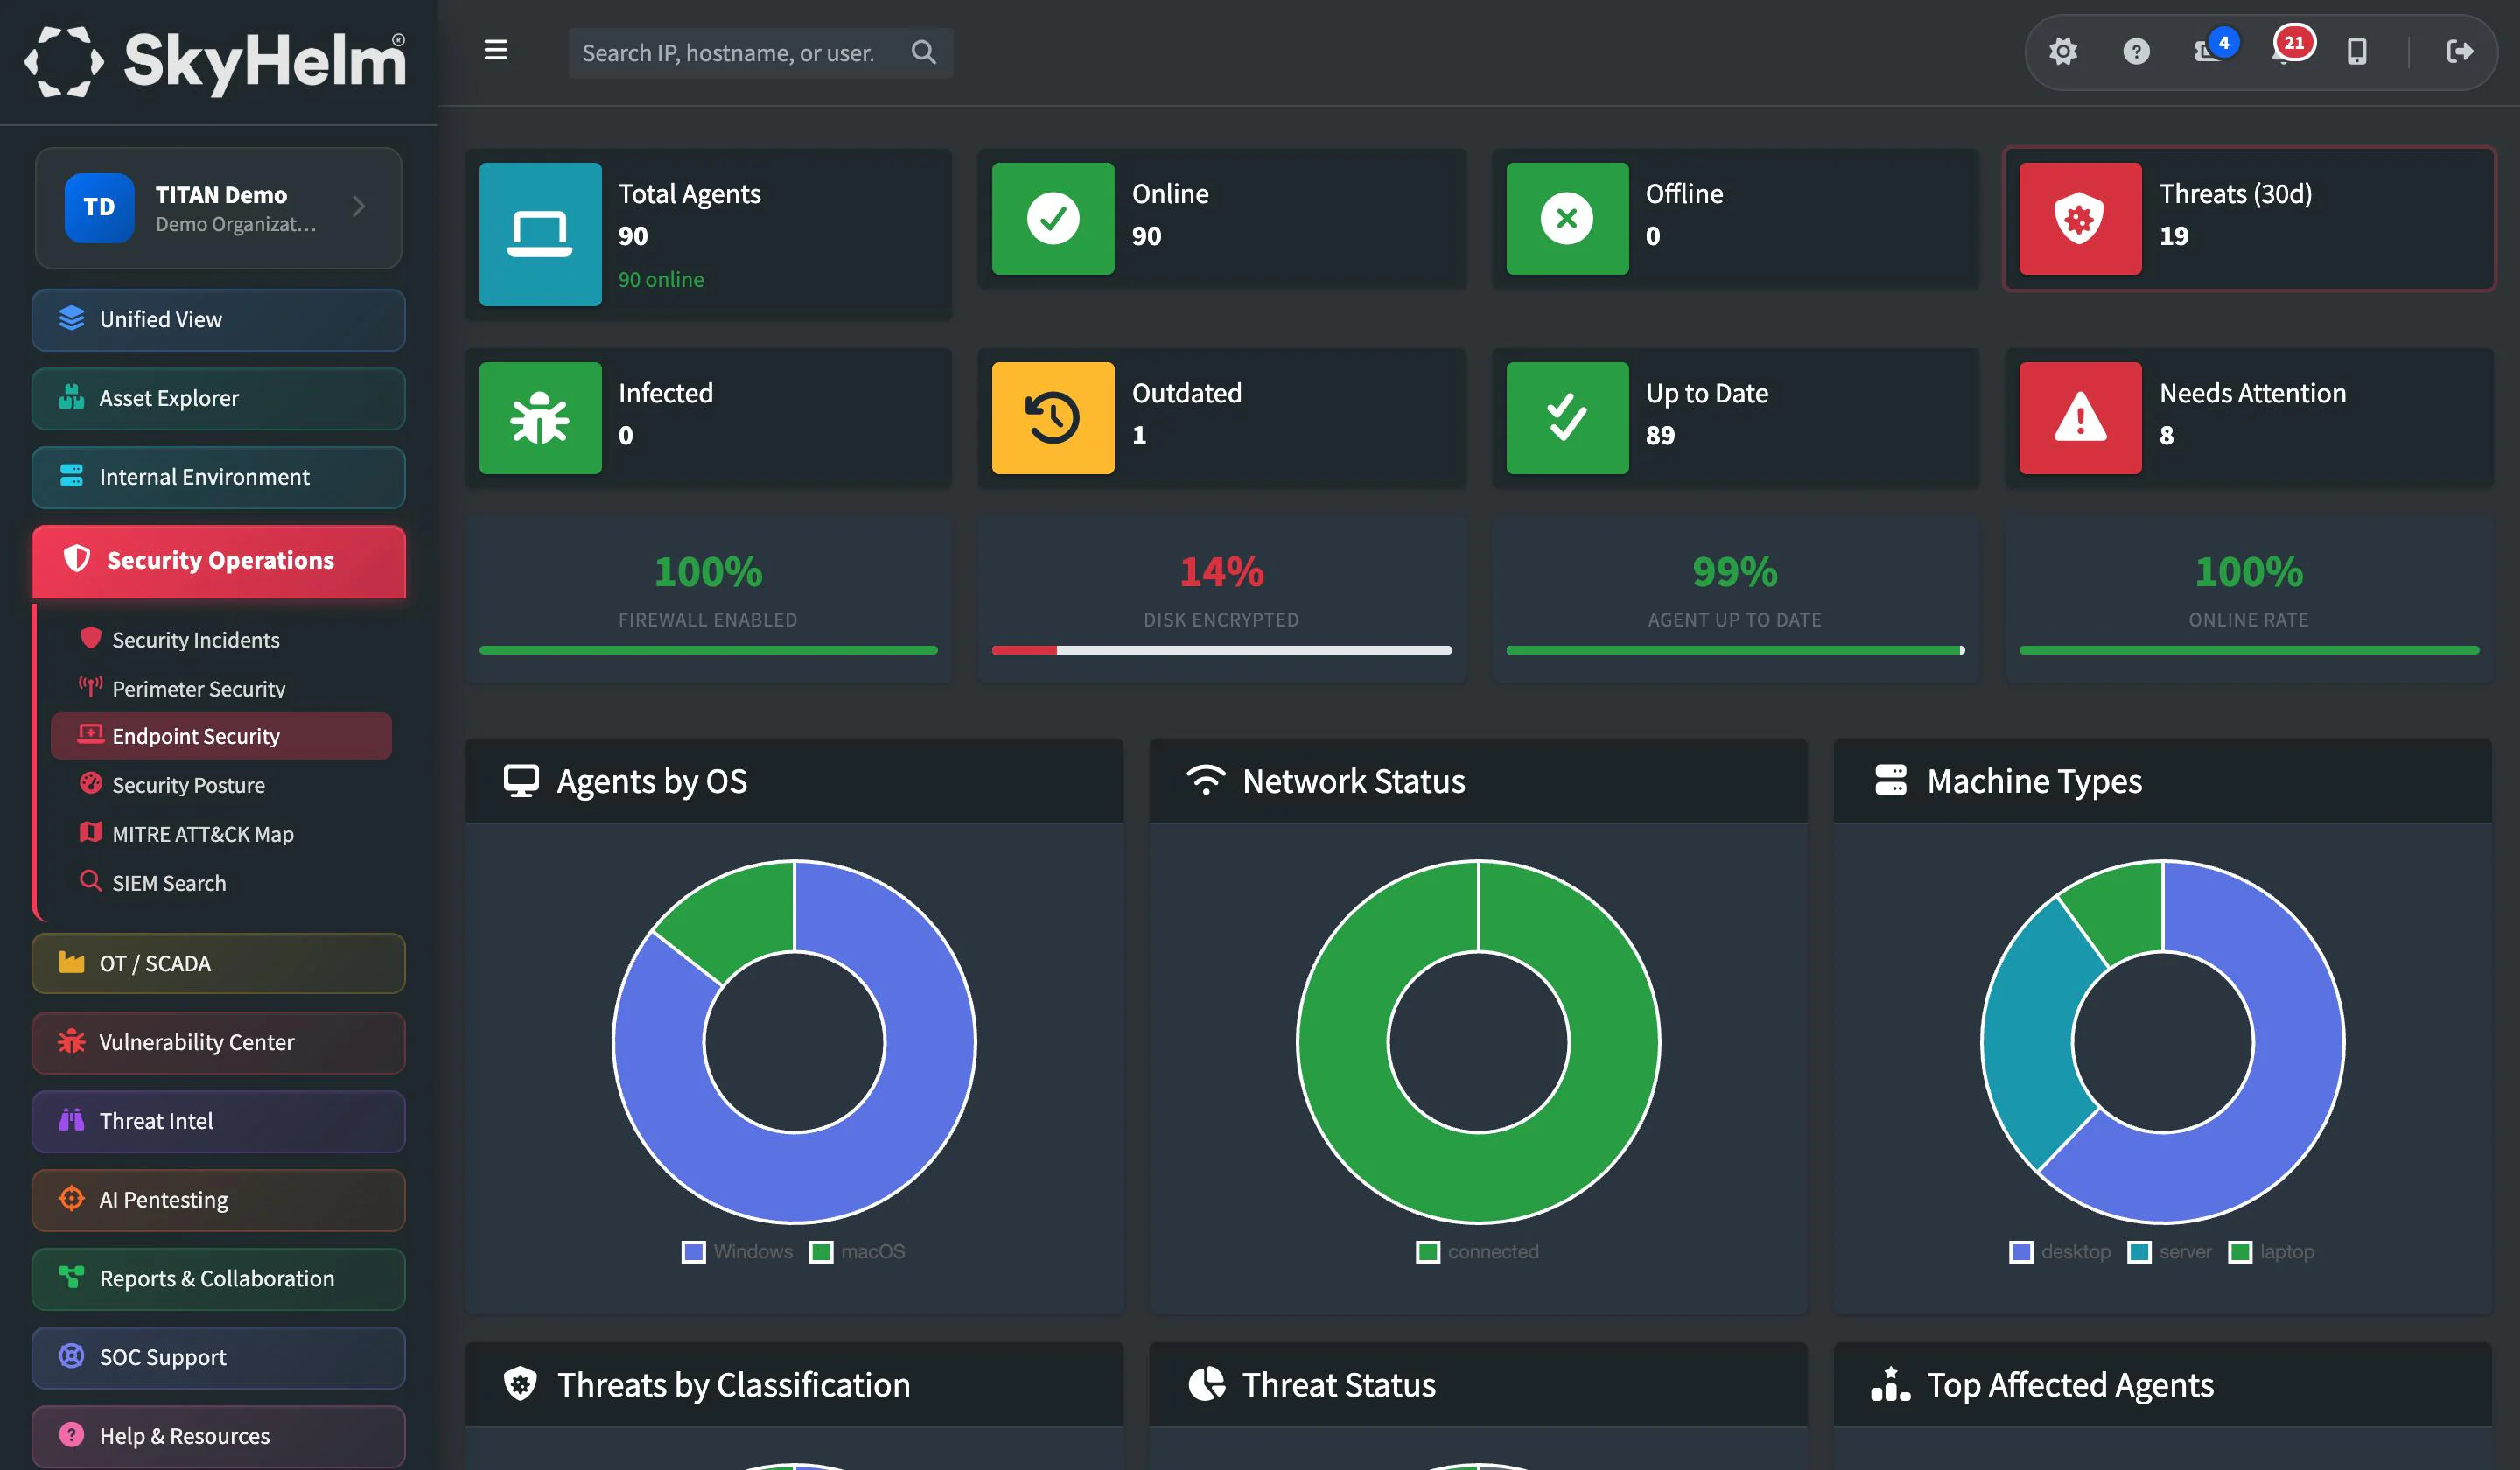
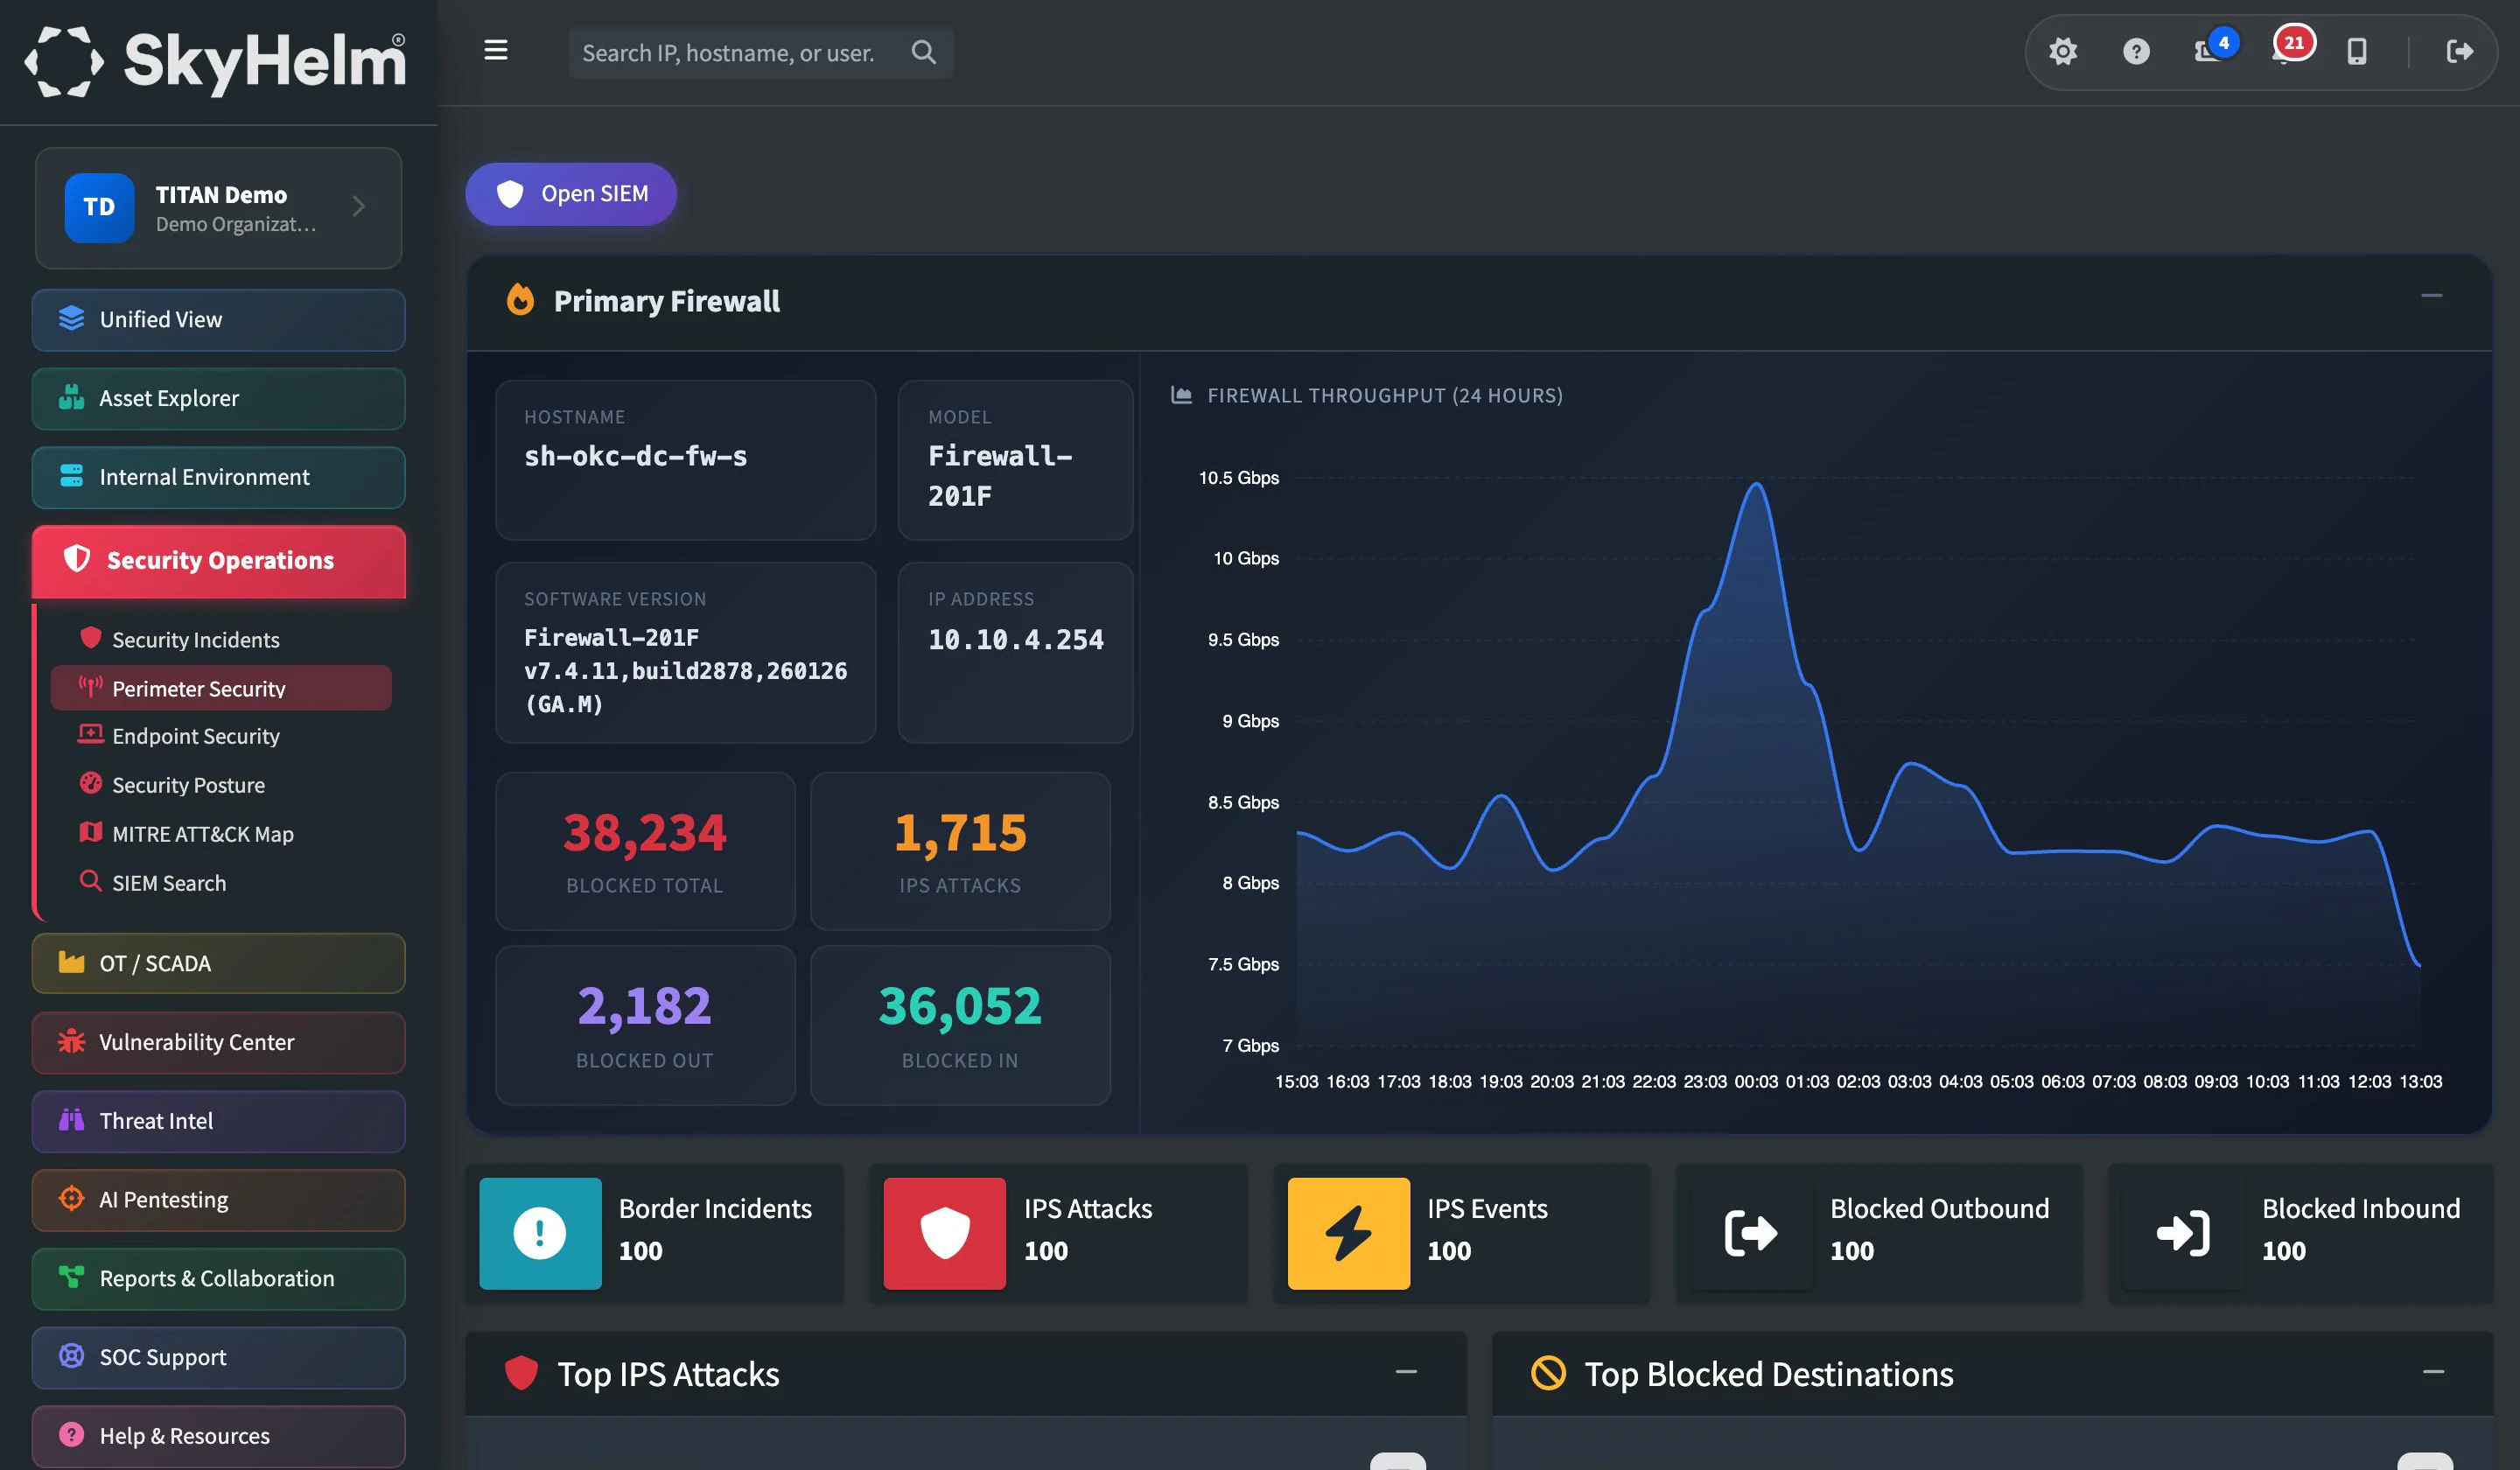
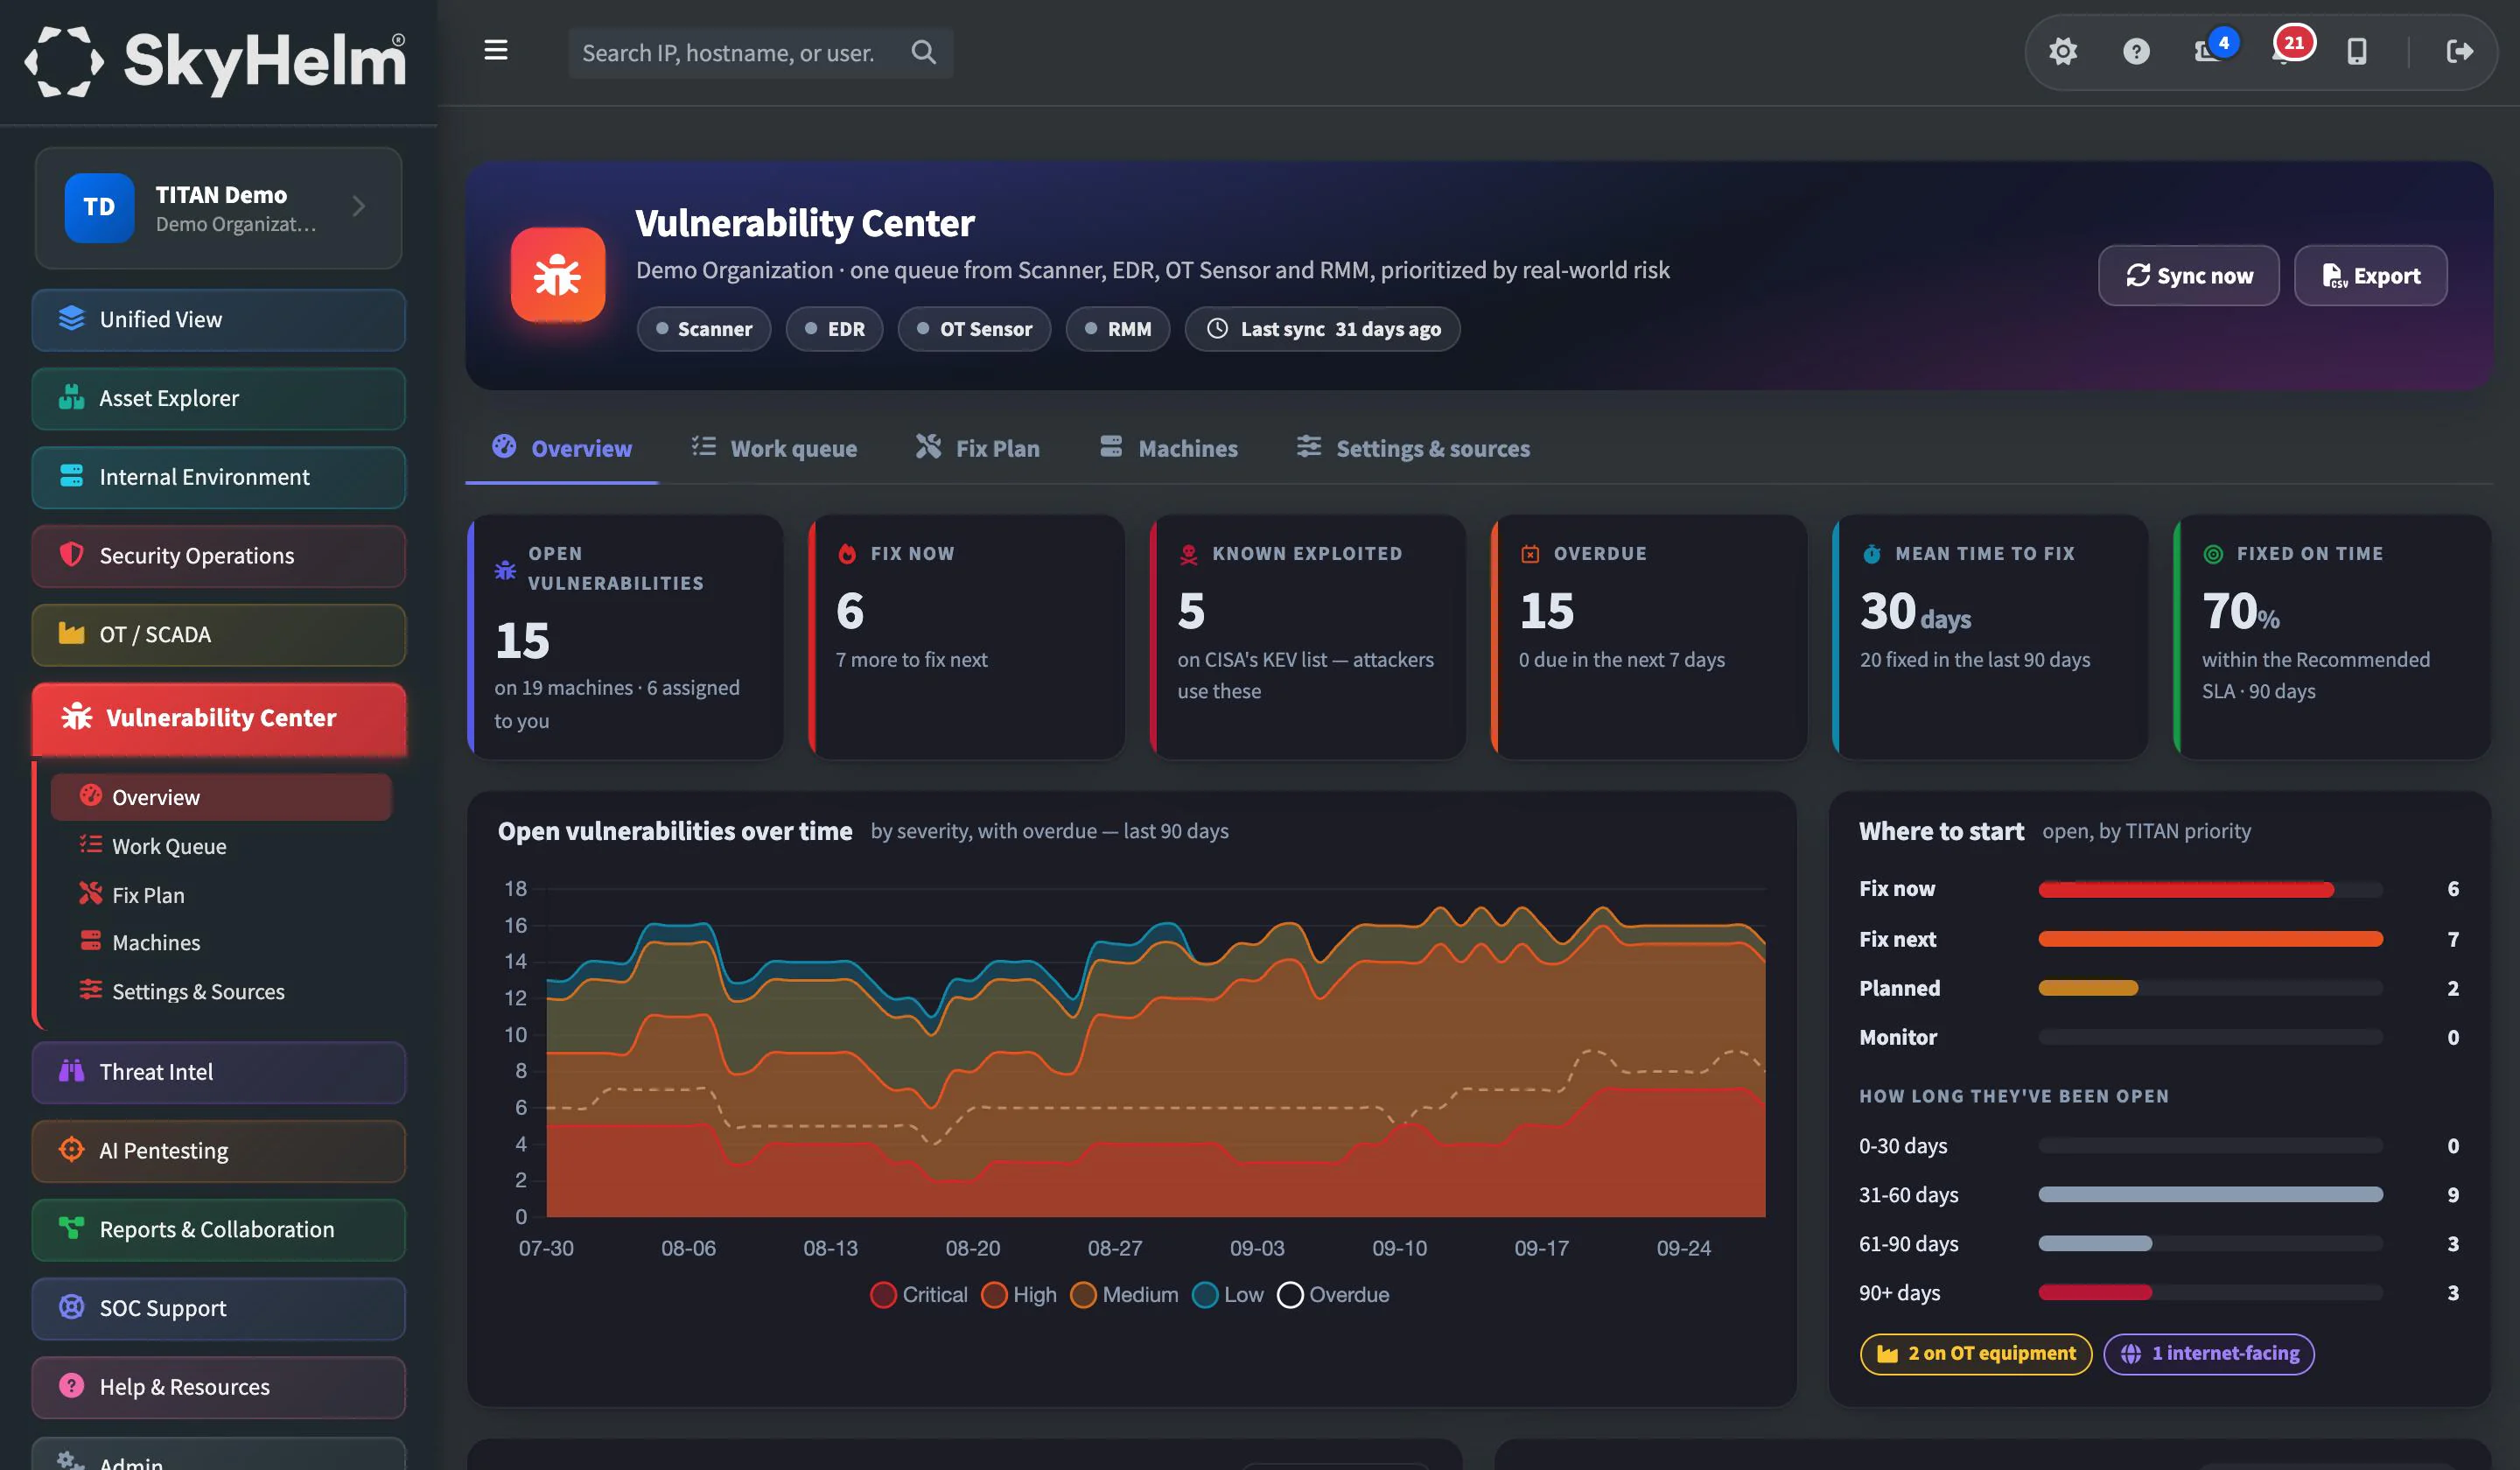
Take a closer look.
Scroll through the views your team will use every day.
Every module. Every job. One platform.
Each module in TITAN is purpose-built for critical infrastructure, unified, correlated, and presented in context. Pick a job to see the modules behind it.
See & Manage
Know every device, every network and every change across your organization.
Detect & Respond
Catch attacks on endpoints, in the traffic, in OT and across every log.
Anticipate Threats
Find your exposure and weaknesses before an attacker does.
Plan & Improve
Report to your board, measure yourself against NIST, CISA and NRECA, and ask TITAN anything.
How TITAN Works
Modular tools. One platform. Zero blind spots.
Every log. One timeline.
Firewalls, servers, endpoints and OT, correlated in real time into the incidents that matter.
One alert, from first ping to board report
TITAN's modules matter because they work together. Here's how a single alert moves through TITAN without anyone opening another console.
Detect
The firewall's IPS blocks an exploit attempt. A critical alert lands in TITAN Alerts and on your phone.
Investigate
Click the source IP. IP Intelligence checks 14 sources and your own alerts; TITAN Search finds everywhere it appears.
Understand
The targeted machine's asset page shows its software, patches, vulnerabilities and past incidents in one place.
Fix
The Fix Plan names the update that closes the hole, and your team pushes it remotely in minutes.
Prove
The case closes once every tool stops detecting it, and the win shows up in Sunday's recap and the board report.
Built secure, from sign-in to storage
TITAN connects to every security tool your organization runs, so it's built with the same care: tight access control, isolated data and protection against abuse.
TITAN never works alone.
Behind TITAN is the SkyHelm 24/7 SOC: US-based analysts who know electric cooperatives, watching your environment around the clock. Their work shows up right inside TITAN, the alerts they handled and their ticket activity, so you always know what happened while you were asleep.
Learn About Our SOC- US-based SOC that knows your organization
- Named analysts familiar with your environment
- Direct phone escalation to on-call analysts
- NERC CIP-aware incident handling
- OT/SCADA-trained analysts
- The SkyHelm SOC's work is visible in TITAN: alerts it handled and its ticket activity
261 capabilities. One platform.
See how TITAN stacks up against the platforms organizations like yours usually evaluate, feature by feature.
See TITAN in action
Schedule a walkthrough with our team. We'll show you how TITAN unifies your security stack and gives your team the visibility they've been missing.