Vulnerability Center. Find it. Fix it. Prove it.
One work queue for every vulnerability from every tool, prioritized by real-world exploitability.
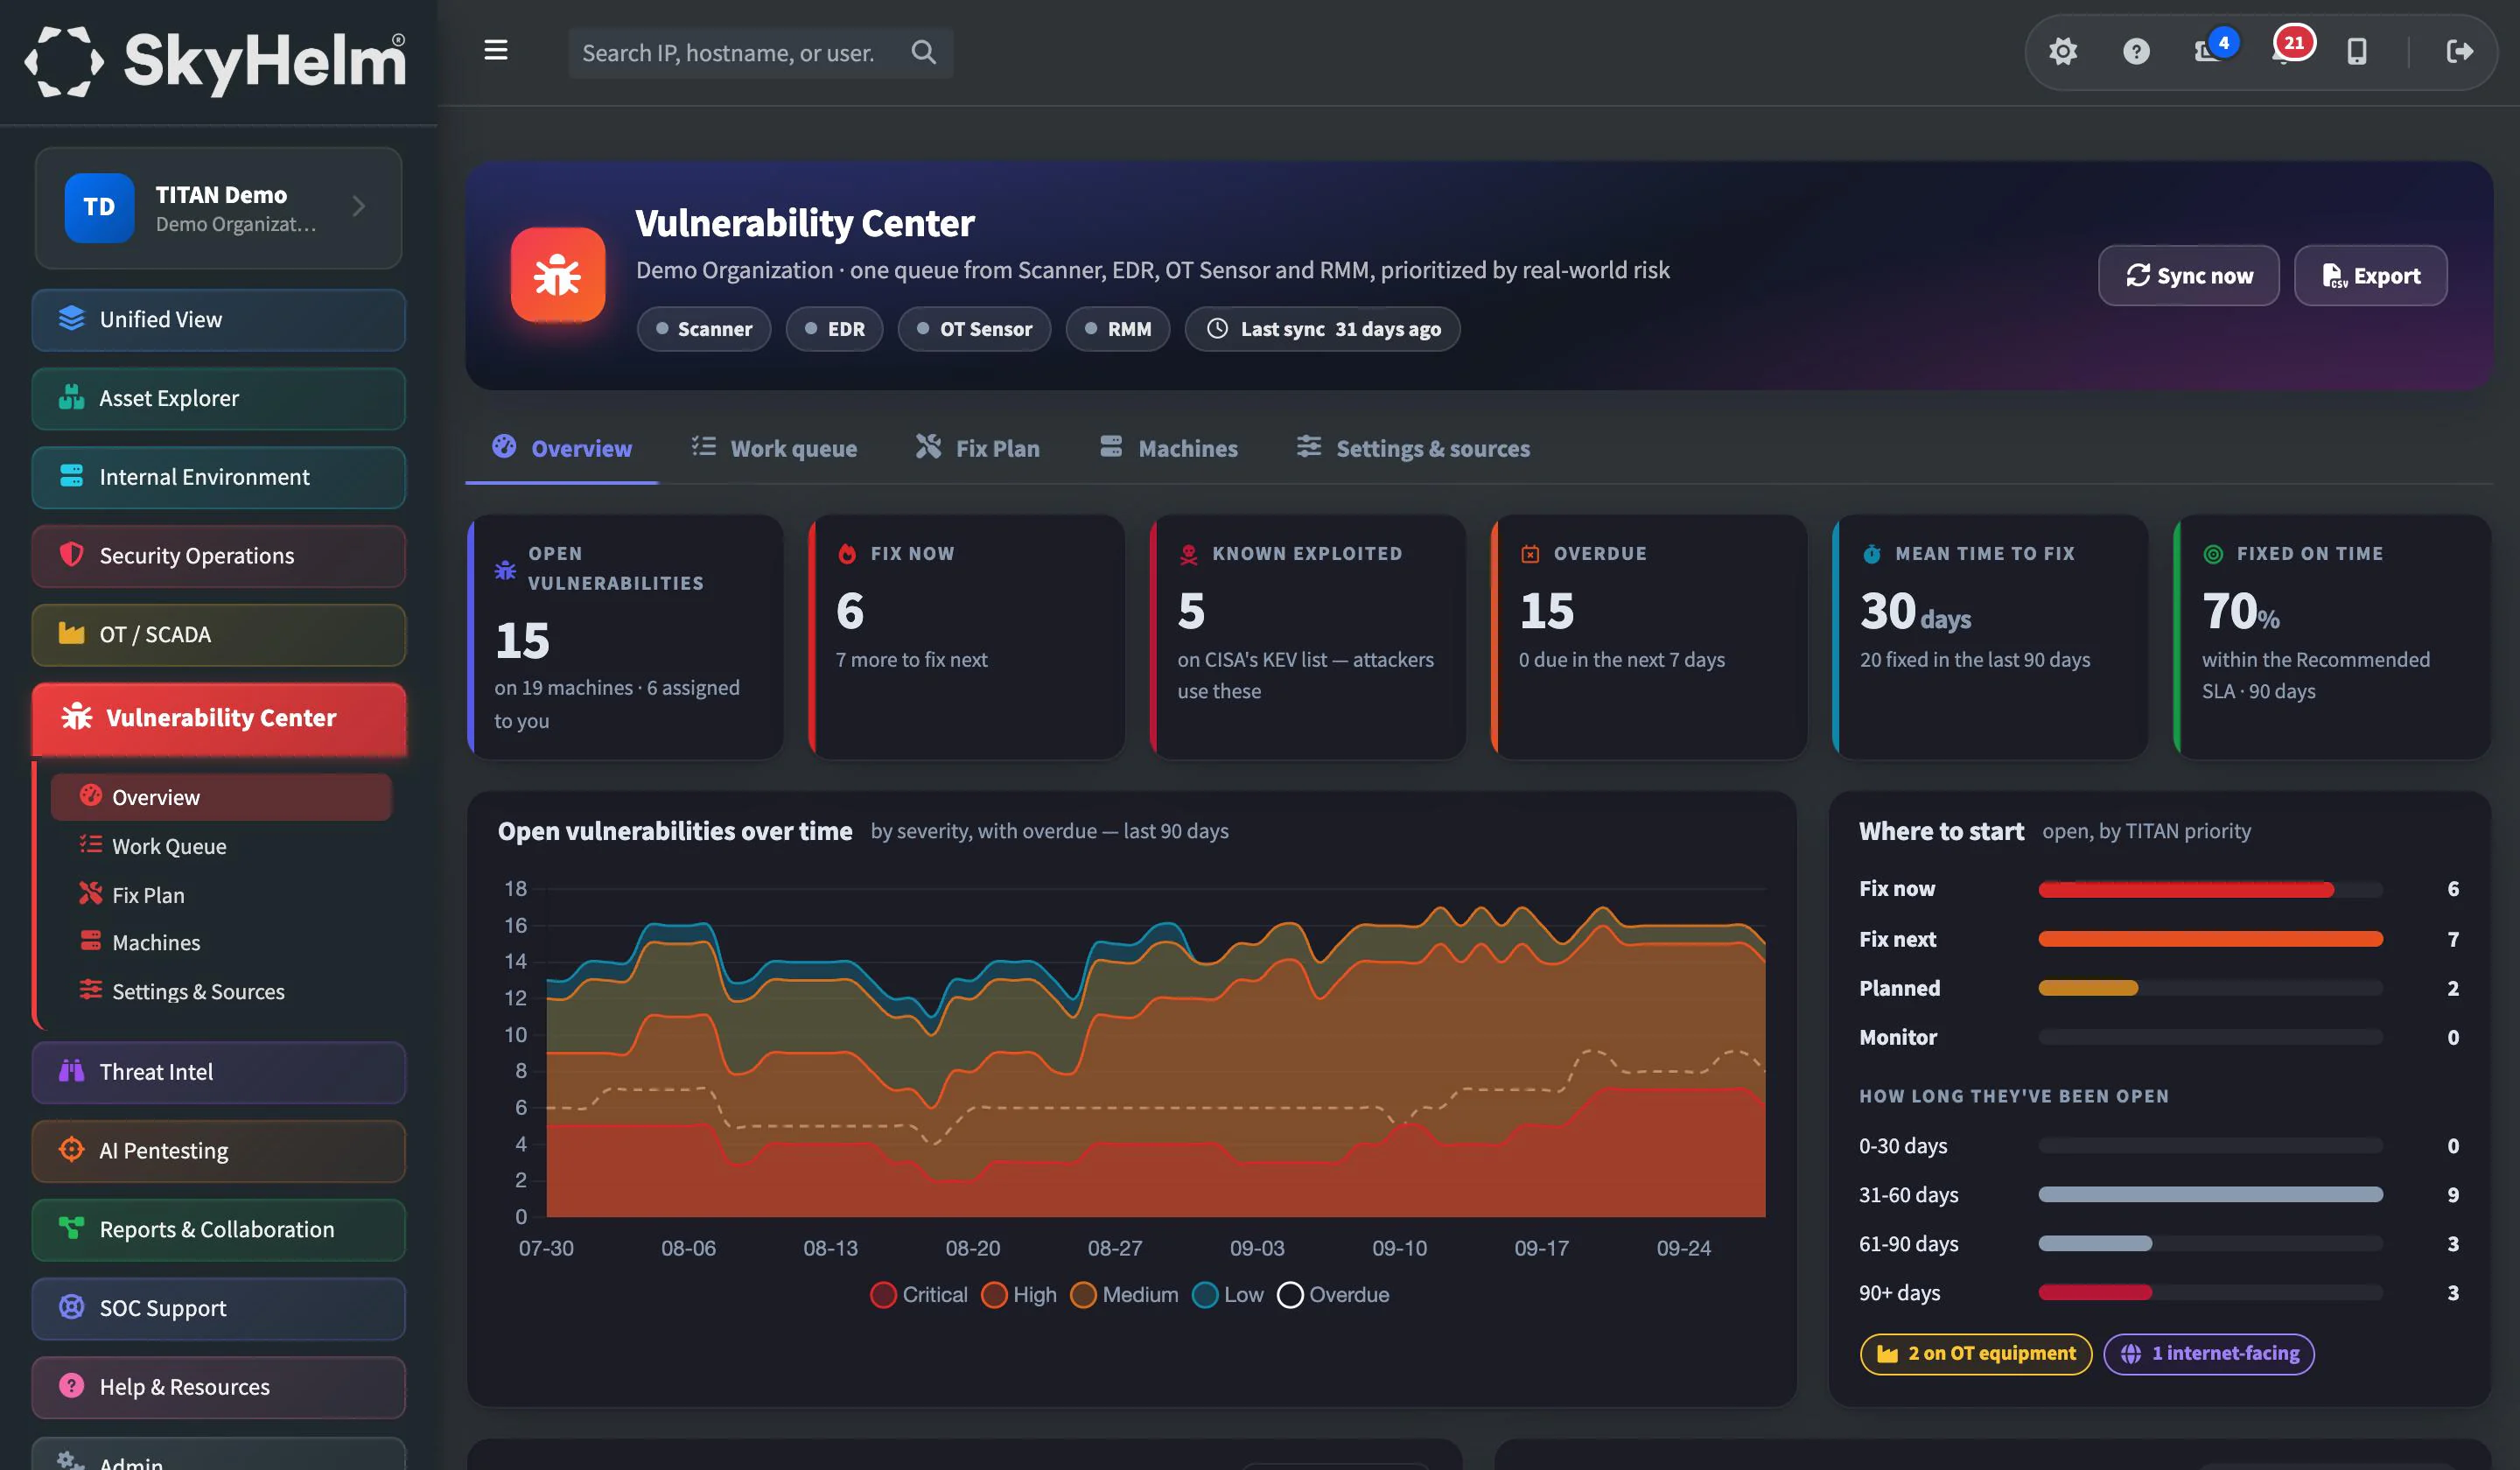
Your scanner, EDR, OT platform and patch tool all find vulnerabilities, and each keeps its own list. The Vulnerability Center merges them into one work queue, ranks every case by how likely it is to be exploited, tells your team exactly which update fixes it, and only closes it once every tool agrees it's gone.
Vulnerability scanning · EDR · OT monitoring · RMM patch data · CISA KEV · EPSS
CVSS alone isn't enough
A CVSS 9.8 on a test server matters less than a CVSS 6.5 on your SCADA historian. TITAN knows the difference.
One Work Queue
Findings from every source, scanners, EDR, OT and patch tools, become one work queue. The same vulnerability reported by several tools becomes one case.
Exploit-Aware Priority
Priority weighs CISA KEV, EPSS exploit likelihood, public exploits, internet exposure and OT assets, and shows every factor, so you always know why a case is at the top.
Fix Plan
Cases grouped by the update that clears them, with the machines to install it on, and plain-language fix guidance on every case. One patch can close dozens of cases.
Continuous Scanning
Authenticated internal and unauthenticated external scanning, scheduled and on demand, with credentialed configuration and compliance audits.
Verified Remediation
A fix counts only once every tool stops detecting it. If a vulnerability comes back, the case reopens automatically, so you never assume something is closed.
SLA Policies
Due dates from a policy you choose: Recommended, NERC CIP-007, Small team or your own, with overdue tracking for every case.
Risk Exceptions
Accepted risk, mitigated and false positive exceptions need a reason and a review date, and live in an exceptions register. Newly known-exploited vulnerabilities are flagged even on accepted risks.
Assign & Collaborate
Assign, comment on and resolve cases, with a full history of who did what. Bulk actions and CSV export keep big backlogs moving.
Remediation Metrics
Backlog trend, on-time rate and time to fix by severity, plus nine report sections and a dedicated Vulnerability Management Report template for your board.
Inside Vulnerability Center
The views your team will use every day.
Backlog trend, on-time rate and time to fix by severity.
Know why every case is at the top.
Severity scores tell you how bad a vulnerability could be. TITAN also asks how likely it is to be used against you: is it on CISA's Known Exploited list, how high is its EPSS exploit likelihood, is a public exploit out there, is the machine internet-facing, is it an OT asset?
Every factor is shown on the case, so priority is never a black box, and the Fix Plan tells your team the one update that clears it.
- On the CISA Known Exploited list
- EPSS exploit likelihood: 94%
- Public exploit available
- Internet-facing machine
- –OT asset
Collect. Prioritize. Fix. Verify.
Collect
Scanners, EDR, OT and patch tools all feed in; the same finding from several tools becomes one case.
Prioritize
Exploit-aware scoring weighs KEV, EPSS, public exploits, exposure and OT assets.
Fix
The Fix Plan groups cases by the update that clears them; patch on your schedule.
Verify
A case closes only when every tool stops detecting it, and reopens if it comes back.
Everything in Vulnerability Center
23 capabilities, every one included in TITAN.
Scanning & compliance
7- Authenticated internal vulnerability scanning
- Unauthenticated (external) vulnerability scanning
- CVE-based risk scoring and prioritization
- Scheduled + on-demand scans
- Remediation tracking and workflow
- Compliance-mapped reporting (NERC, PCI, etc.)
- Credentialed config/compliance audits
Vulnerability Center
16- Vulnerability Center: one work queue built from all available source findings, multiple applications
- Cross-tool correlation: the same vulnerability reported by several tools becomes one case
- Exploit-aware priority weighing CISA KEV, EPSS exploit likelihood, public exploits, internet exposure and OT assets, with every factor shown
- Plain-language fix guidance on every case, with each affected machine listed
- Fix Plan: cases grouped by the update that clears them, with the machines to install it on
- Per-machine vulnerability view, linked both ways with the Asset Explorer
- Assign, comment on and resolve cases, with a full history of who did what
- Risk exceptions (accepted risk, mitigated, false positive) with a required reason and review date, plus an exceptions register
- Verified remediation: a fix counts only once every tool stops detecting it, and a vulnerability that comes back reopens automatically
- SLA due dates from a policy you choose: Recommended, NERC CIP-007, Small team or your own, with overdue tracking
- Missing OS and third-party patches from RMM tracked alongside CVEs
- Newly known-exploited (KEV) vulnerabilities flagged even on accepted risks, prompting a second look
- Remediation metrics: backlog trend, on-time rate and time to fix by severity
- Bulk actions and CSV export of the work queue
- Source health: each tool's last sync and status at a glance, plus on-demand sync
- Nine Vulnerability Management report sections and a dedicated Vulnerability Management Report template
Works hand in hand with
Stop guessing. Start managing.
See how TITAN turns vulnerability chaos into a closed-loop remediation process your team can actually execute.