Change Detection and Management. Catch every change.
Capture every configuration, flag every change and keep the audit trail NERC CIP asks for.
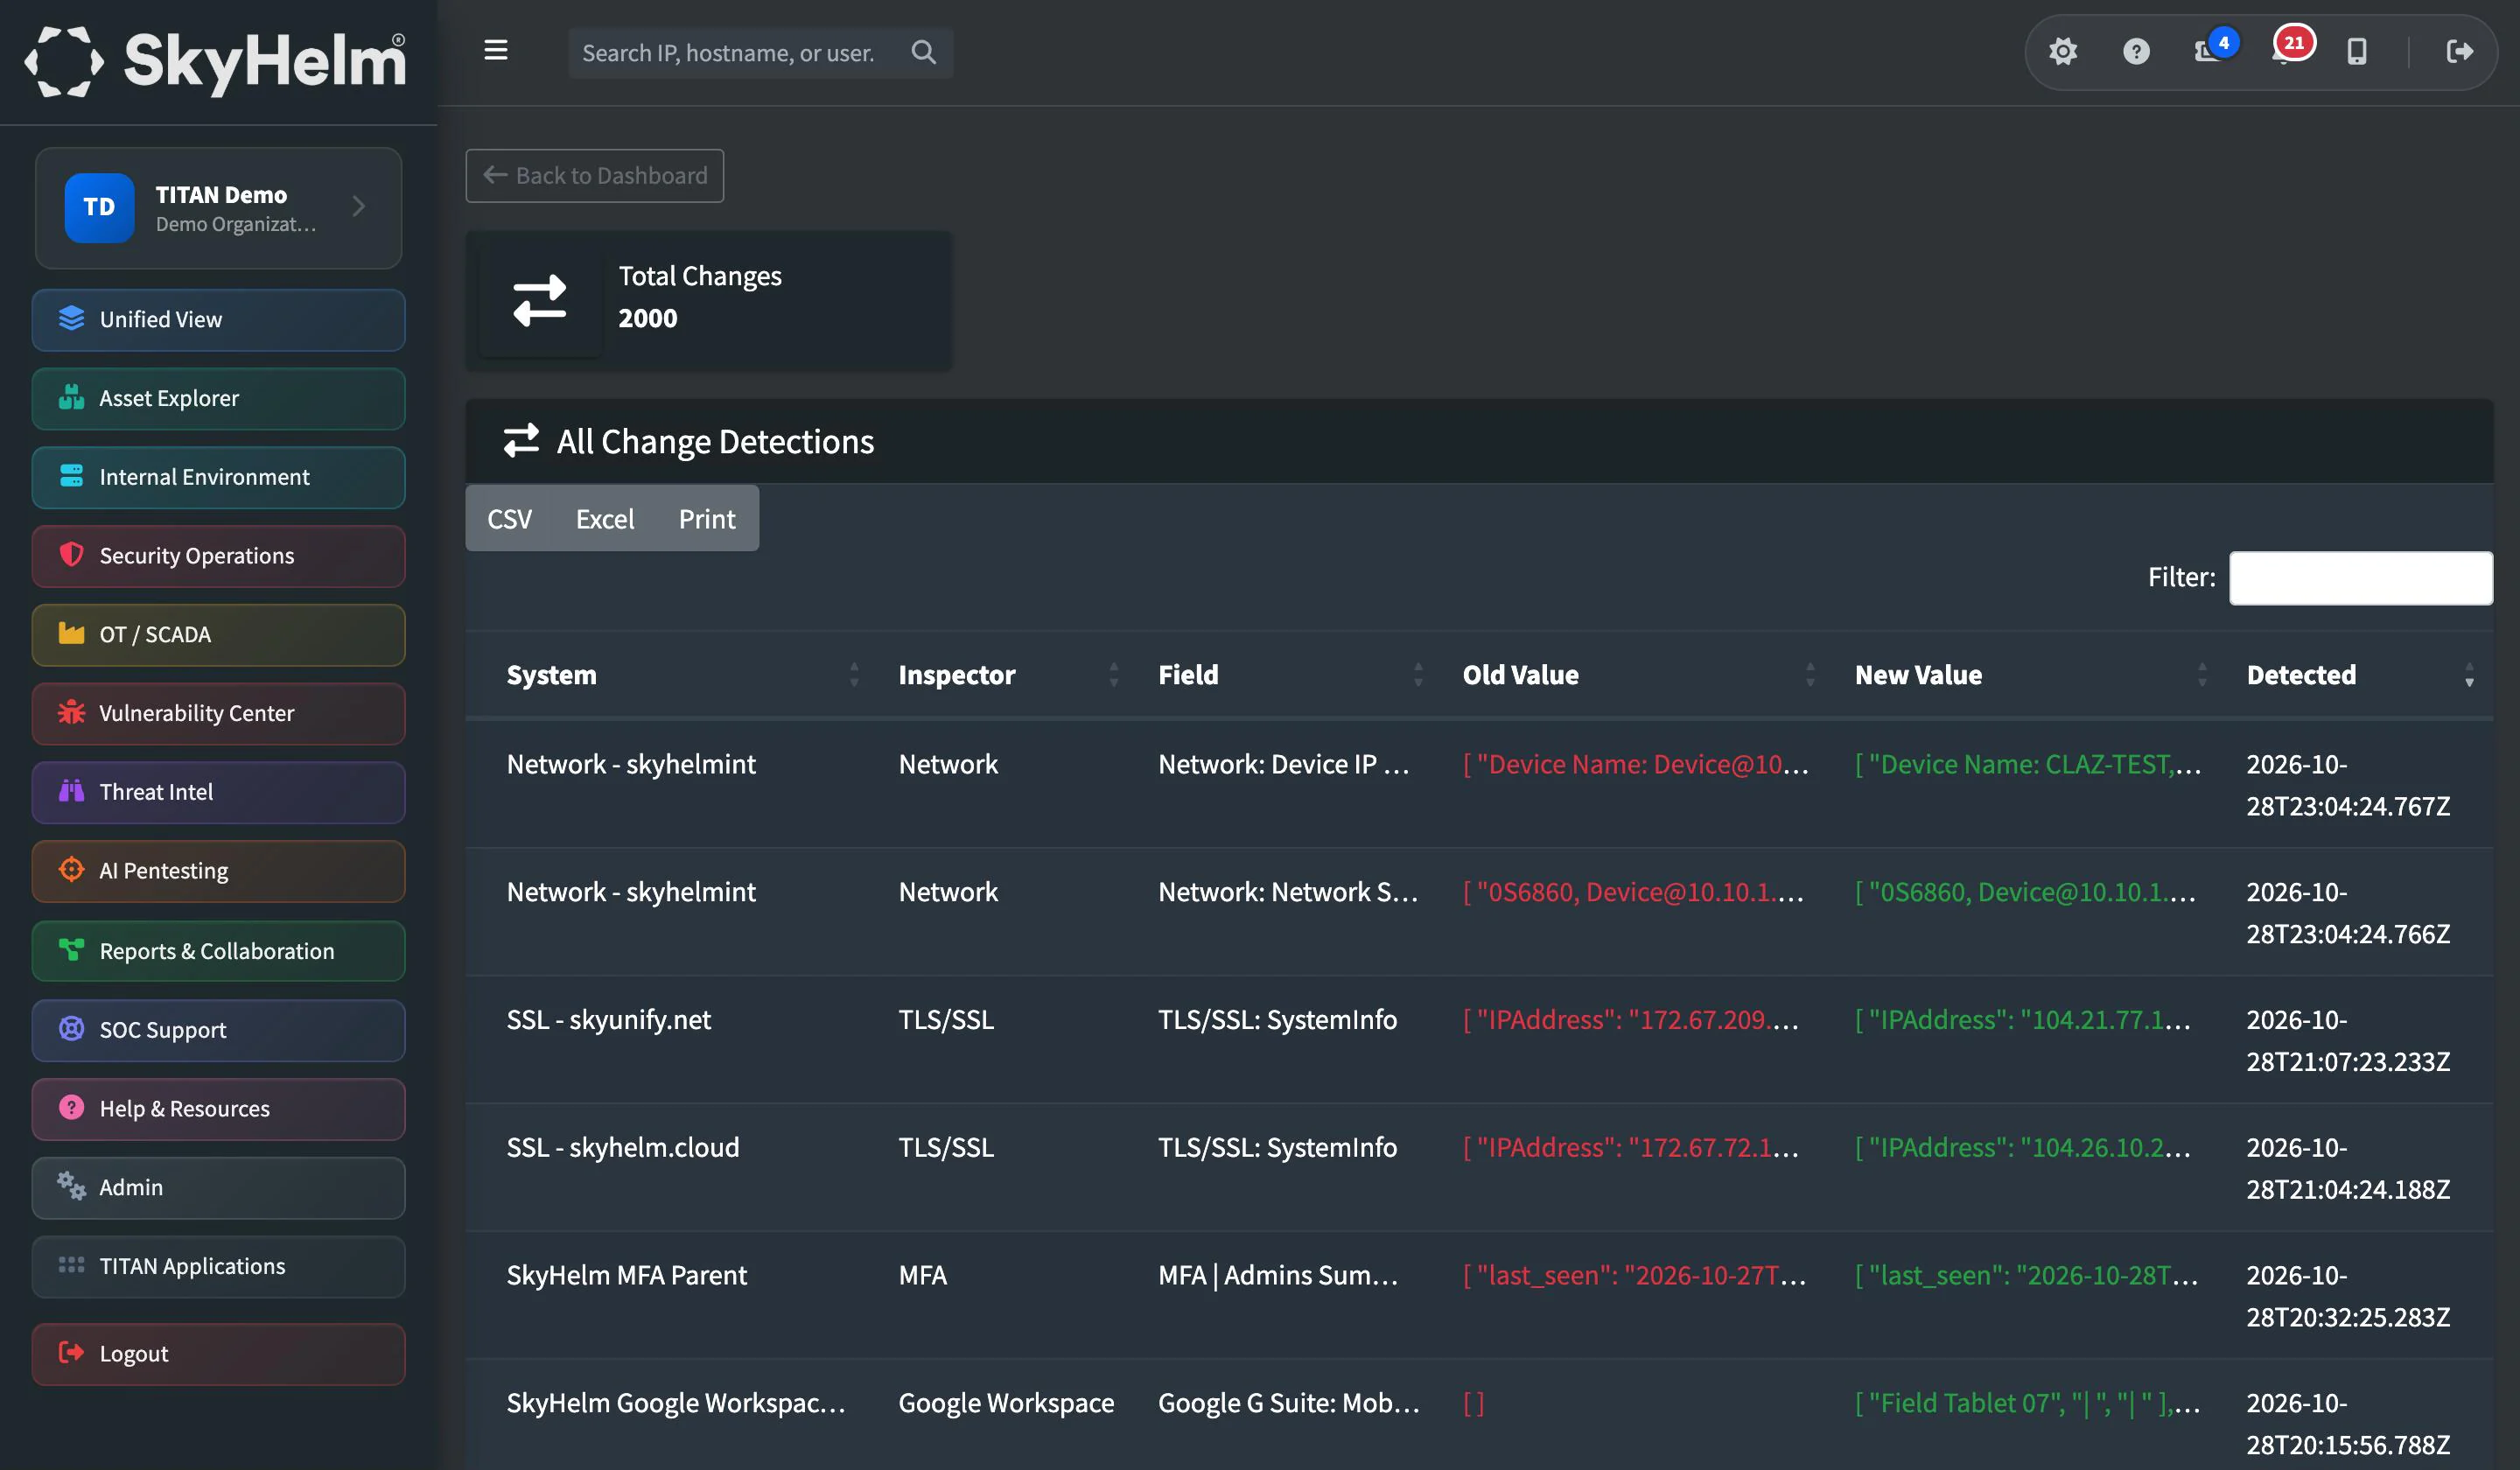
Automated configuration capture and change detection across every system in your organization. Firewalls, switches, Active Directory, DNS, cloud services, backups: every setting documented, every change tracked, every deviation flagged.
IT documentation · Network config backups · Asset Explorer
Every configuration. Every change. Every system.
Stop logging into twelve admin consoles to check configurations. TITAN captures, compares, and alerts on every setting across your entire infrastructure.
Automated Configuration Capture
Every firewall rule, switch port config, AD policy, DNS record, and DHCP scope, captured automatically on a schedule. No manual exports. No stale documentation. Always current.
Change Detection with Diff Views
See exactly what changed, when it changed, and who changed it. Side-by-side diffs for every configuration shift, from a modified firewall rule to a new Group Policy object.
Compliance Baselines
Define your golden configuration and measure every device against it. Drift detection alerts you when a switch, firewall, or server deviates from your approved baseline.
Historical Audit Trail
Full configuration history going back months. When an auditor asks 'what did your firewall rules look like on March 15th?', you answer in seconds, not days.
Critical Change Alerts
Get notified when someone modifies a firewall rule, changes a DNS record, or alters an AD group membership. Know about unauthorized changes before they become incidents.
New Device Detection
A detection engine watches for devices that appear for the first time, with 24-hour, 7-day and 30-day windows and first-seen and last-seen tracking for every asset.
Cross-System Visibility
Firewalls, switches, Active Directory, DNS, DHCP, backup systems, cloud services, all inspected from a single platform. No jumping between twelve admin consoles.
Multi-System Correlation
See how a change in one system affects others. A DNS modification that breaks VPN connectivity. A Group Policy change that weakens endpoint security. Connected visibility.
NERC CIP Compliance Reporting
Generate evidence packages for CIP-005, CIP-007, and CIP-010 requirements. Configuration management documentation that auditors actually accept, produced automatically.
Inside Change Detection and Management
The views your team will use every day.
Every configuration change, timestamped and attributed, in one timeline.
Every change. In context.
Configuration changes don't happen in isolation. A firewall rule change at 8 AM might explain the VPN outage at 8:05 AM. TITAN's timeline view connects the dots so you stop chasing symptoms and start finding root causes.
Every change is timestamped, attributed, and diff'd against the previous configuration. When your auditor asks "who opened port 3389 and when?", you have the answer before they finish the question.
Rule #47 modified, port 3389 opened to 0.0.0.0/0
New admin added to Domain Admins group
MX record changed for primary domain
VLAN 42 added to trunk ports on core switch
Retention policy reduced from 30 to 7 days
Audit-ready. Always.
NERC CIP requires documented configuration management. TITAN generates the evidence automatically, no last-minute scrambles, no manual documentation, no audit anxiety.
Automated Evidence
Configuration snapshots and change logs generated continuously, no manual effort required.
Tamper-Proof History
Immutable audit trail. Every capture timestamped and preserved. No one can rewrite history.
One-Click Reports
Export compliance packages for NERC CIP, NIST CSF, or custom frameworks in seconds.
Everything in Change Detection and Management
6 capabilities, every one included in TITAN.
Configuration history
1- Change history and audit trail
Network changes
2- Configuration backup for network devices
- Alerting on device state changes
New devices
1- New device detection engine with 24-hour, 7-day and 30-day windows and a First Seen/Last Seen tracking
External changes
2- Historical exposure data and change tracking
- Alerting on newly exposed services
Works hand in hand with
Know every configuration. Catch every change.
Schedule a walkthrough and we'll show you how TITAN captures, tracks, and alerts on every configuration change across your infrastructure.