Endpoint Detection & Response. AI that fights back.
Behavioral AI that detects, contains and rolls back attacks on every workstation and server.
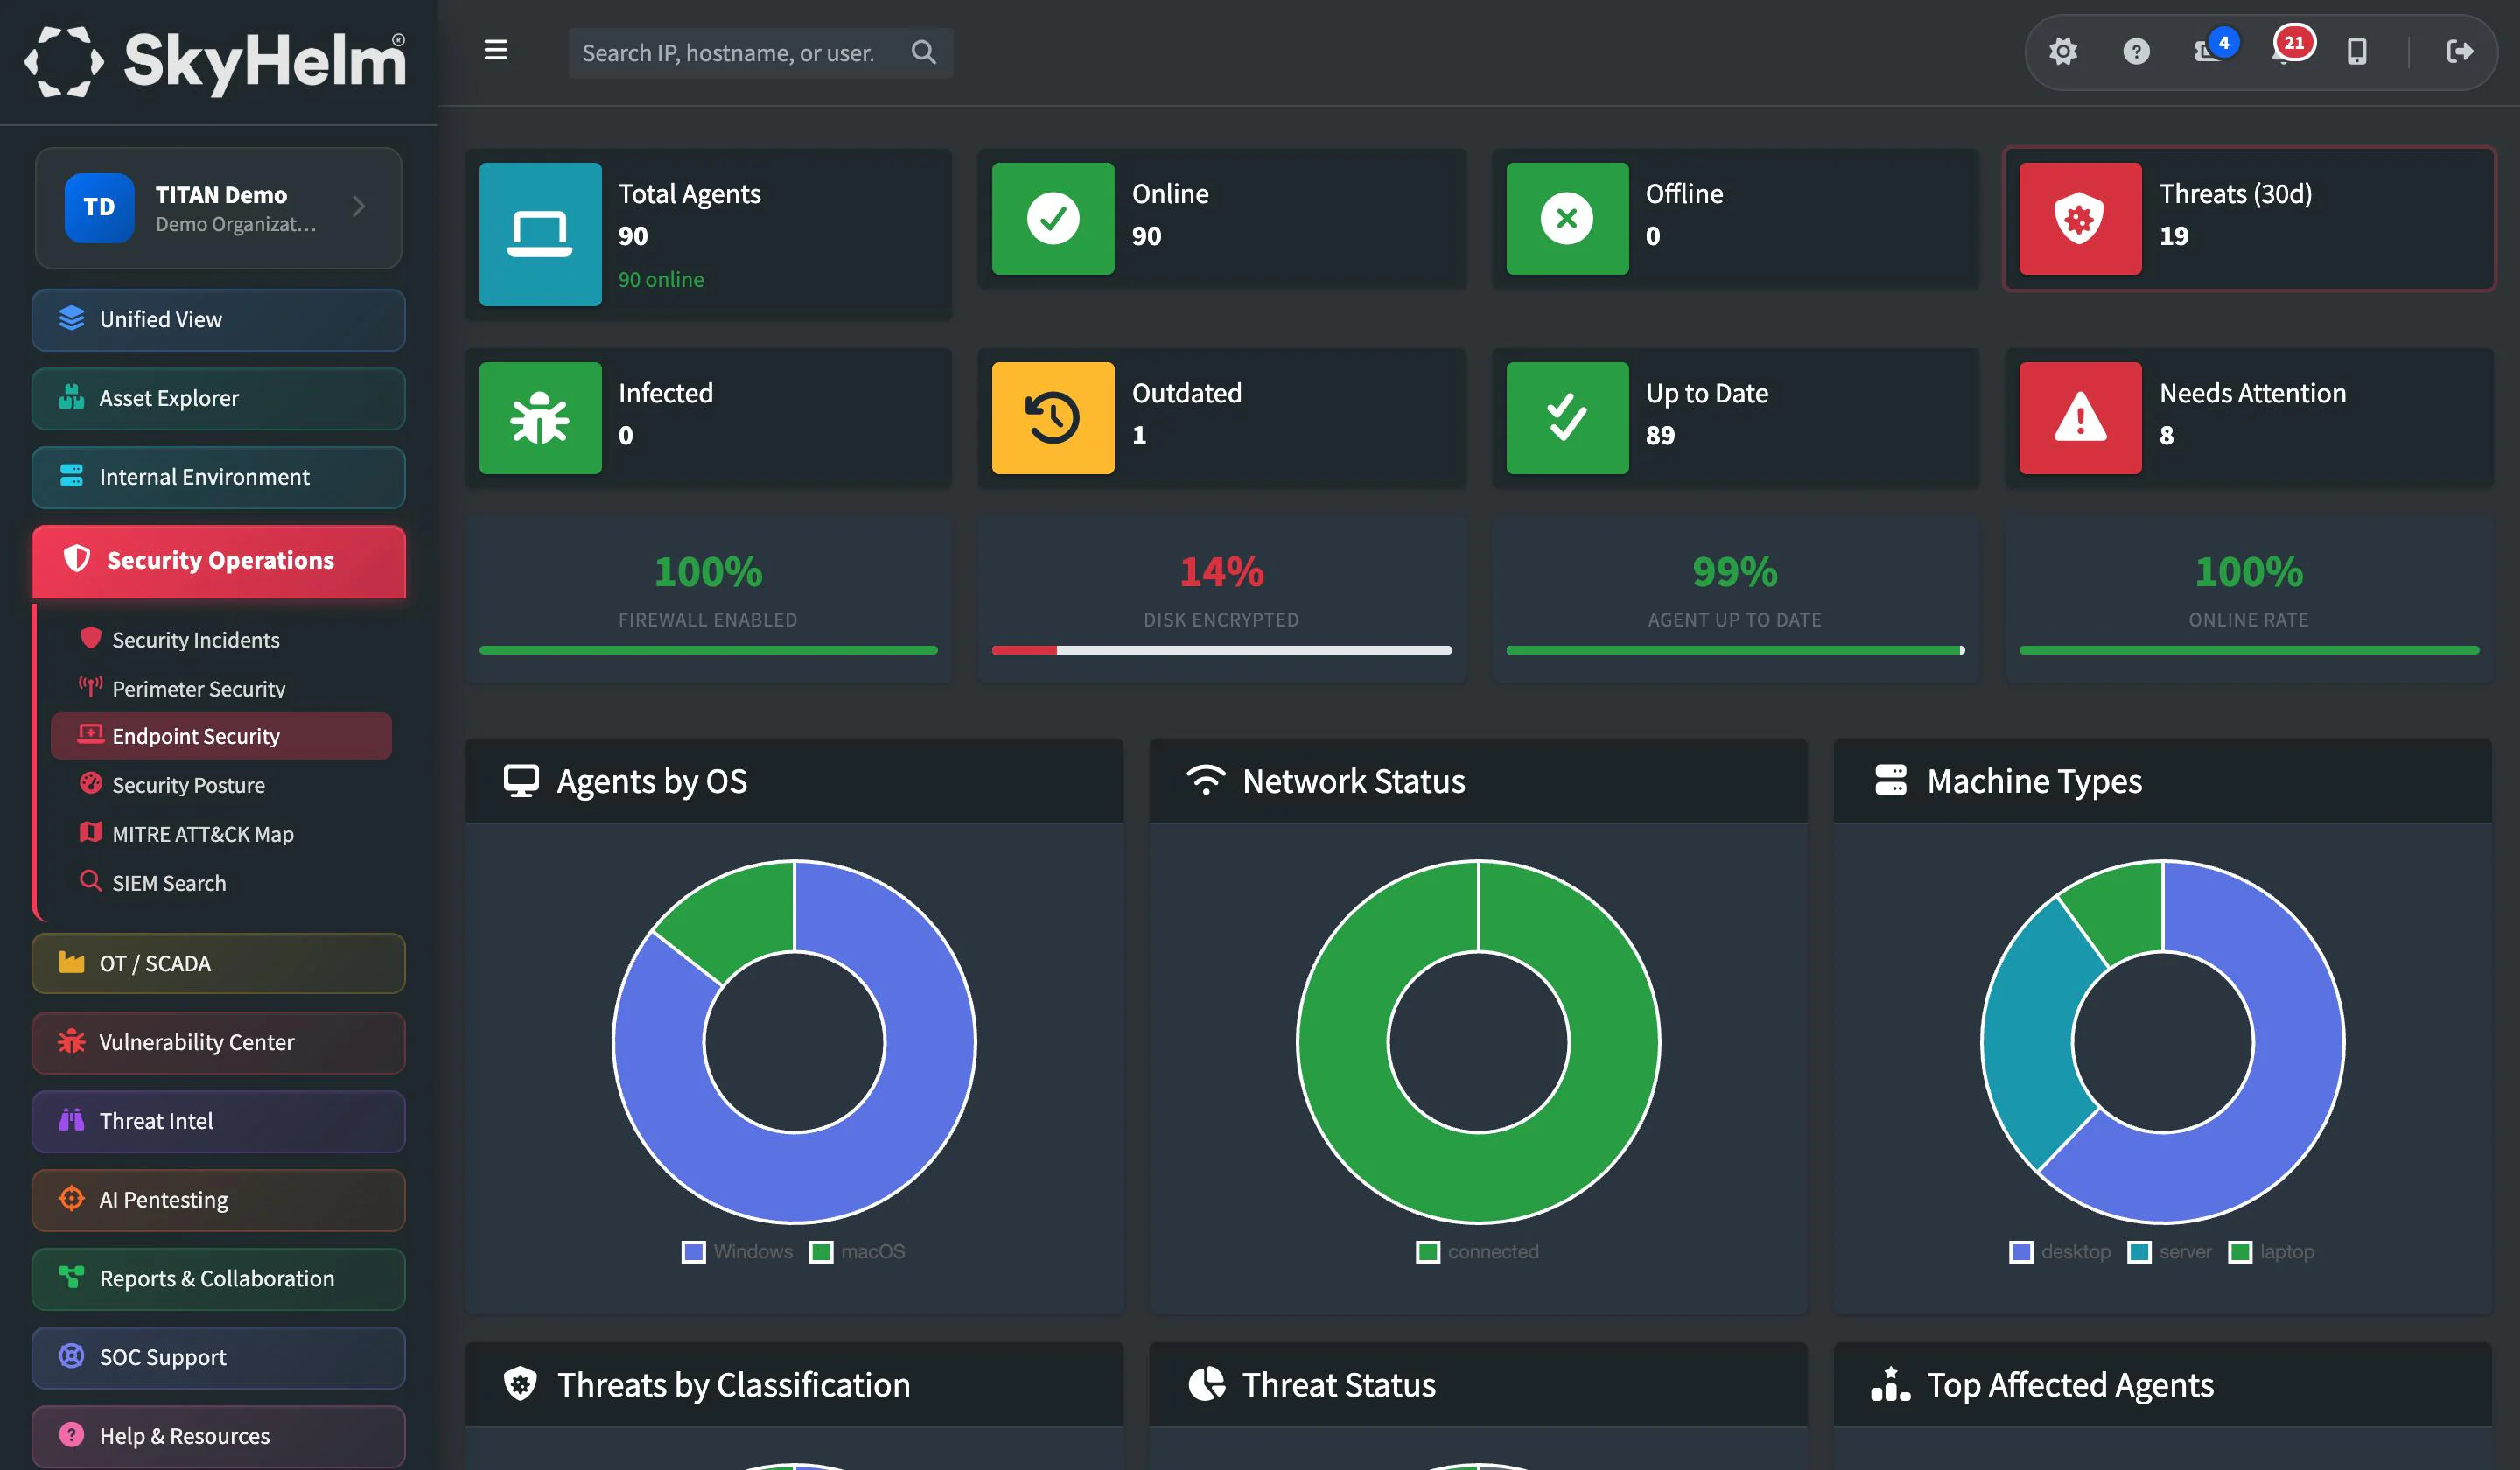
Next-generation endpoint protection powered by behavioral AI, not signatures. Every workstation, server, and laptop in your organization is defended by autonomous detection and response that operates at machine speed. This isn't antivirus. This is a different category.
Autonomous protection. Zero babysitting.
Your endpoints don't wait for a human to respond. Neither does TITAN.
AI-Powered Threat Detection
Behavioral AI identifies malware, ransomware, and fileless attacks in real time, without signature updates. No waiting for the next definition file. The AI watches every process and knows when something isn't right.
Autonomous Response
Threats are automatically contained at machine speed: killed, quarantined, and remediated without human intervention. By the time your SOC analyst opens the alert, the threat is already neutralized.
Ransomware Rollback
One-click rollback restores encrypted files to their pre-attack state. Even if ransomware executes, your data isn't gone, it's recoverable. The safety net your organization needs.
Attack Storyline Visualization
See the full attack chain, initial access, privilege escalation, lateral movement, persistence, in a visual timeline. Understand exactly how a threat got in and how far it spread.
Deep Visibility
Every process, file operation, registry change, and network connection logged and searchable across all endpoints. Threat hunt across your entire fleet from a single query interface.
Remote Shell
Secure remote investigation and remediation directly on any endpoint. Investigate a suspicious process on a substation workstation without driving 45 minutes to get there.
Device Control
USB, Bluetooth, and peripheral policy enforcement across the fleet. Block unauthorized storage devices, prevent data exfiltration, and enforce your acceptable use policies at the endpoint level.
Rogue Device Detection
Identify unmanaged devices connecting to your network, personal laptops, contractor machines, IoT devices that shouldn't be there. If it's not managed, it's a risk.
Cross-Platform Protection
Windows, macOS, and Linux, all protected by a single lightweight agent. Same detection, same response, same visibility regardless of operating system.
Inside Endpoint Detection & Response
The views your team will use every day.
Active threats and protection status across every endpoint.
Watch an attack unfold, and get stopped
TITAN reconstructs the entire attack chain in a visual timeline. See exactly how a threat got in, what it tried to do, and how it was neutralized, all in under 10 seconds.
Phishing email opened on accounting workstation
Malicious macro launches PowerShell downloader
Payload attempts to disable security services
Behavioral AI flags anomalous process chain
Process killed, payload quarantined, host isolated
Modified files restored to pre-attack state
Ransomware? Roll it back.
Even in the worst-case scenario, ransomware executes and encrypts files, TITAN's endpoint agent maintains protected snapshots that let you restore every affected file to its pre-attack state with a single click. No ransom paid. No data lost. No downtime.
For an organization that can't afford to lose SCADA historians, billing records, or customer data, this isn't a nice-to-have. It's the difference between a bad day and a catastrophe.
Everything in Endpoint Detection & Response
8 capabilities, every one included in TITAN.
Endpoint detection & response
8- Real-time endpoint threat prevention (next-gen AV)
- Behavioral detection of fileless/zero-day threats
- Automated endpoint isolation/containment
- Rollback / ransomware remediation
- AI-assisted threat investigation and triage
- Threat hunting across endpoint telemetry
- Cross-platform coverage (Windows, macOS, Linux)
- Agent health, protection coverage and threat detail drill-downs with context lookups
Works hand in hand with
See autonomous endpoint protection in action
Schedule a demo and watch TITAN detect, contain, and roll back a simulated attack, in real time.