Your worst day. Our specialty.
SIRT is SkyHelm's incident response team. When an alert becomes an incident or a breach, SIRT takes command: containing the attacker remotely within minutes, working the investigation around the clock, and putting responders on site the next day.
Containment in minutes. Answers in hours. Responders on site the next day.
From the first call to the final report.
One process, run the same way every time, so nothing important gets skipped while the pressure is on.
You call us, or we call you
Call the SIRT hotline, or our SOC escalates to SIRT the moment monitoring confirms a serious incident. An incident lead takes ownership on that first call.
Triage and first containment
We confirm what's happening, how severe it is and what's at risk, then take the first containment steps remotely: isolating endpoints, blocking attacker infrastructure and disabling compromised accounts.
Scope the attack and preserve evidence
We trace how far the attacker got across endpoints, firewalls, logs and OT sensors, and preserve logs, memory and disk images before anything is wiped or rebuilt.
Responders on site
SIRT responders arrive at your facility to work alongside your team: hands on keyboards, in the server room and, when it's needed, in the control center.
Remove the attacker and restore
We remove every foothold we find, rebuild from clean images and verified backups, reset credentials and bring systems back in a safe order, operations first.
Report, then harden
You get the full timeline, root cause, every action taken and the fixes that close the gap, written so your board, your insurer and your auditors can all use it.
Every responder sees the same picture.
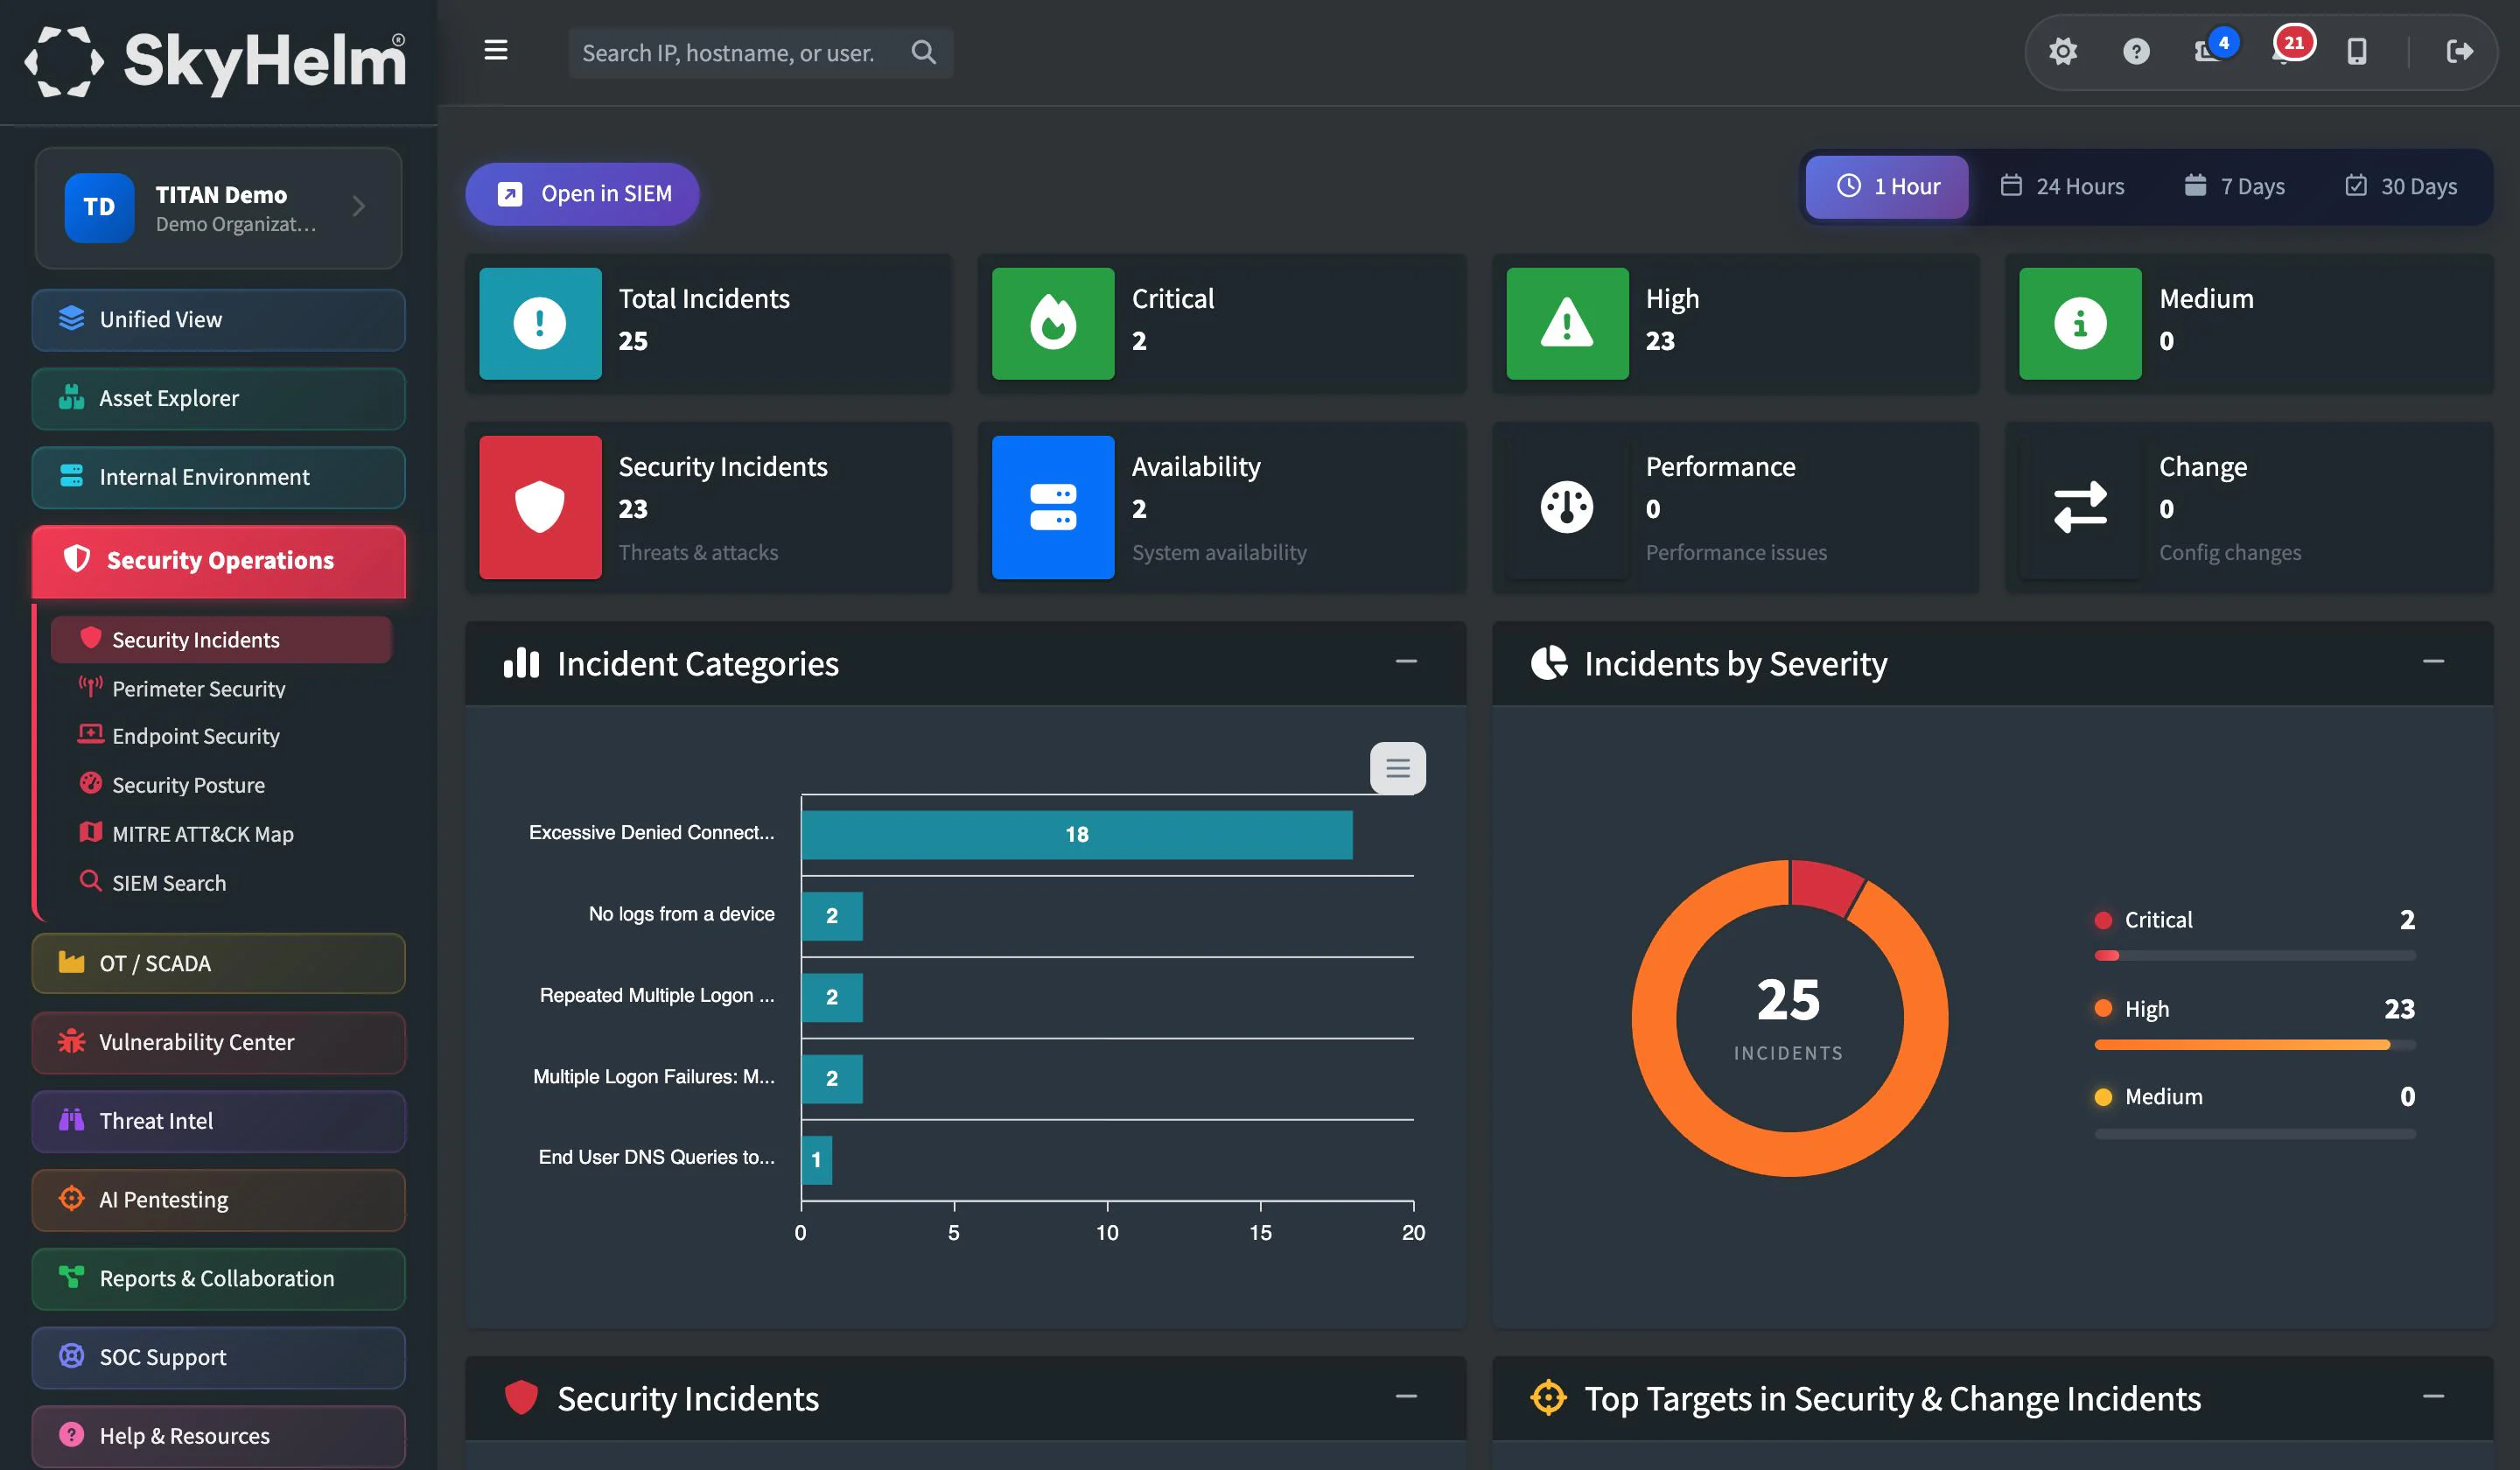
SIRT investigates in TITAN, alongside the SOC, with every alert, log, endpoint and OT sensor already connected. No time lost deploying tools in the middle of a crisis.
Everything an incident needs. In one team.
Incident command
One incident lead runs the response, coordinates the technical work and keeps your leadership informed, so your team isn't left juggling it all.
Digital forensics
Endpoint, memory, log and email forensics, with evidence collected and handled so it holds up for insurers and law enforcement.
OT-safe response
A substation isn't a laptop. Containment steps in operational networks are checked against safety and uptime before anything is changed.
Ransomware response
Stop the spread, work out what was encrypted and what may have left the network, and recover from backups that are known to be clean.
Communications support
Clear, plain-English updates and talking points for your board, your staff and the people you serve.
Partner coordination
We work with your insurer, legal counsel, law enforcement and regulators, so every party gets what it needs from one source.
Already with SkyHelm? You're a step ahead.
SIRT works from the same TITAN data our SOC watches every day. Your agents, sensors and logs are already in place, and we already know your network, your systems and who to call.
TITAN members and SIRT retainer clients get the 15-minute response for critical incidents.*
- Agents and sensors already deployed
- Your network, assets and contacts already known
- Escalation paths agreed ahead of time
- Evidence already flowing into TITAN
- A 15-minute critical response*
How SIRT handles the hard parts.
Think something's wrong? Call now.
The first hours of an incident shape how it ends. Call SIRT at any hour, even if you're not sure yet. We'd much rather hear from you early.
* Quoted response times apply to TITAN members and active SIRT retainer clients. Times for new engagements may be longer depending on current demand.
Have SIRT on your side before you need it.
Talk to us about SIRT coverage for your organization, with a team that already knows your network on the day it matters most.