External Attack Management. See what adversaries see.
Continuous discovery of internet-facing assets, plus graded domain, email and TLS security checks.
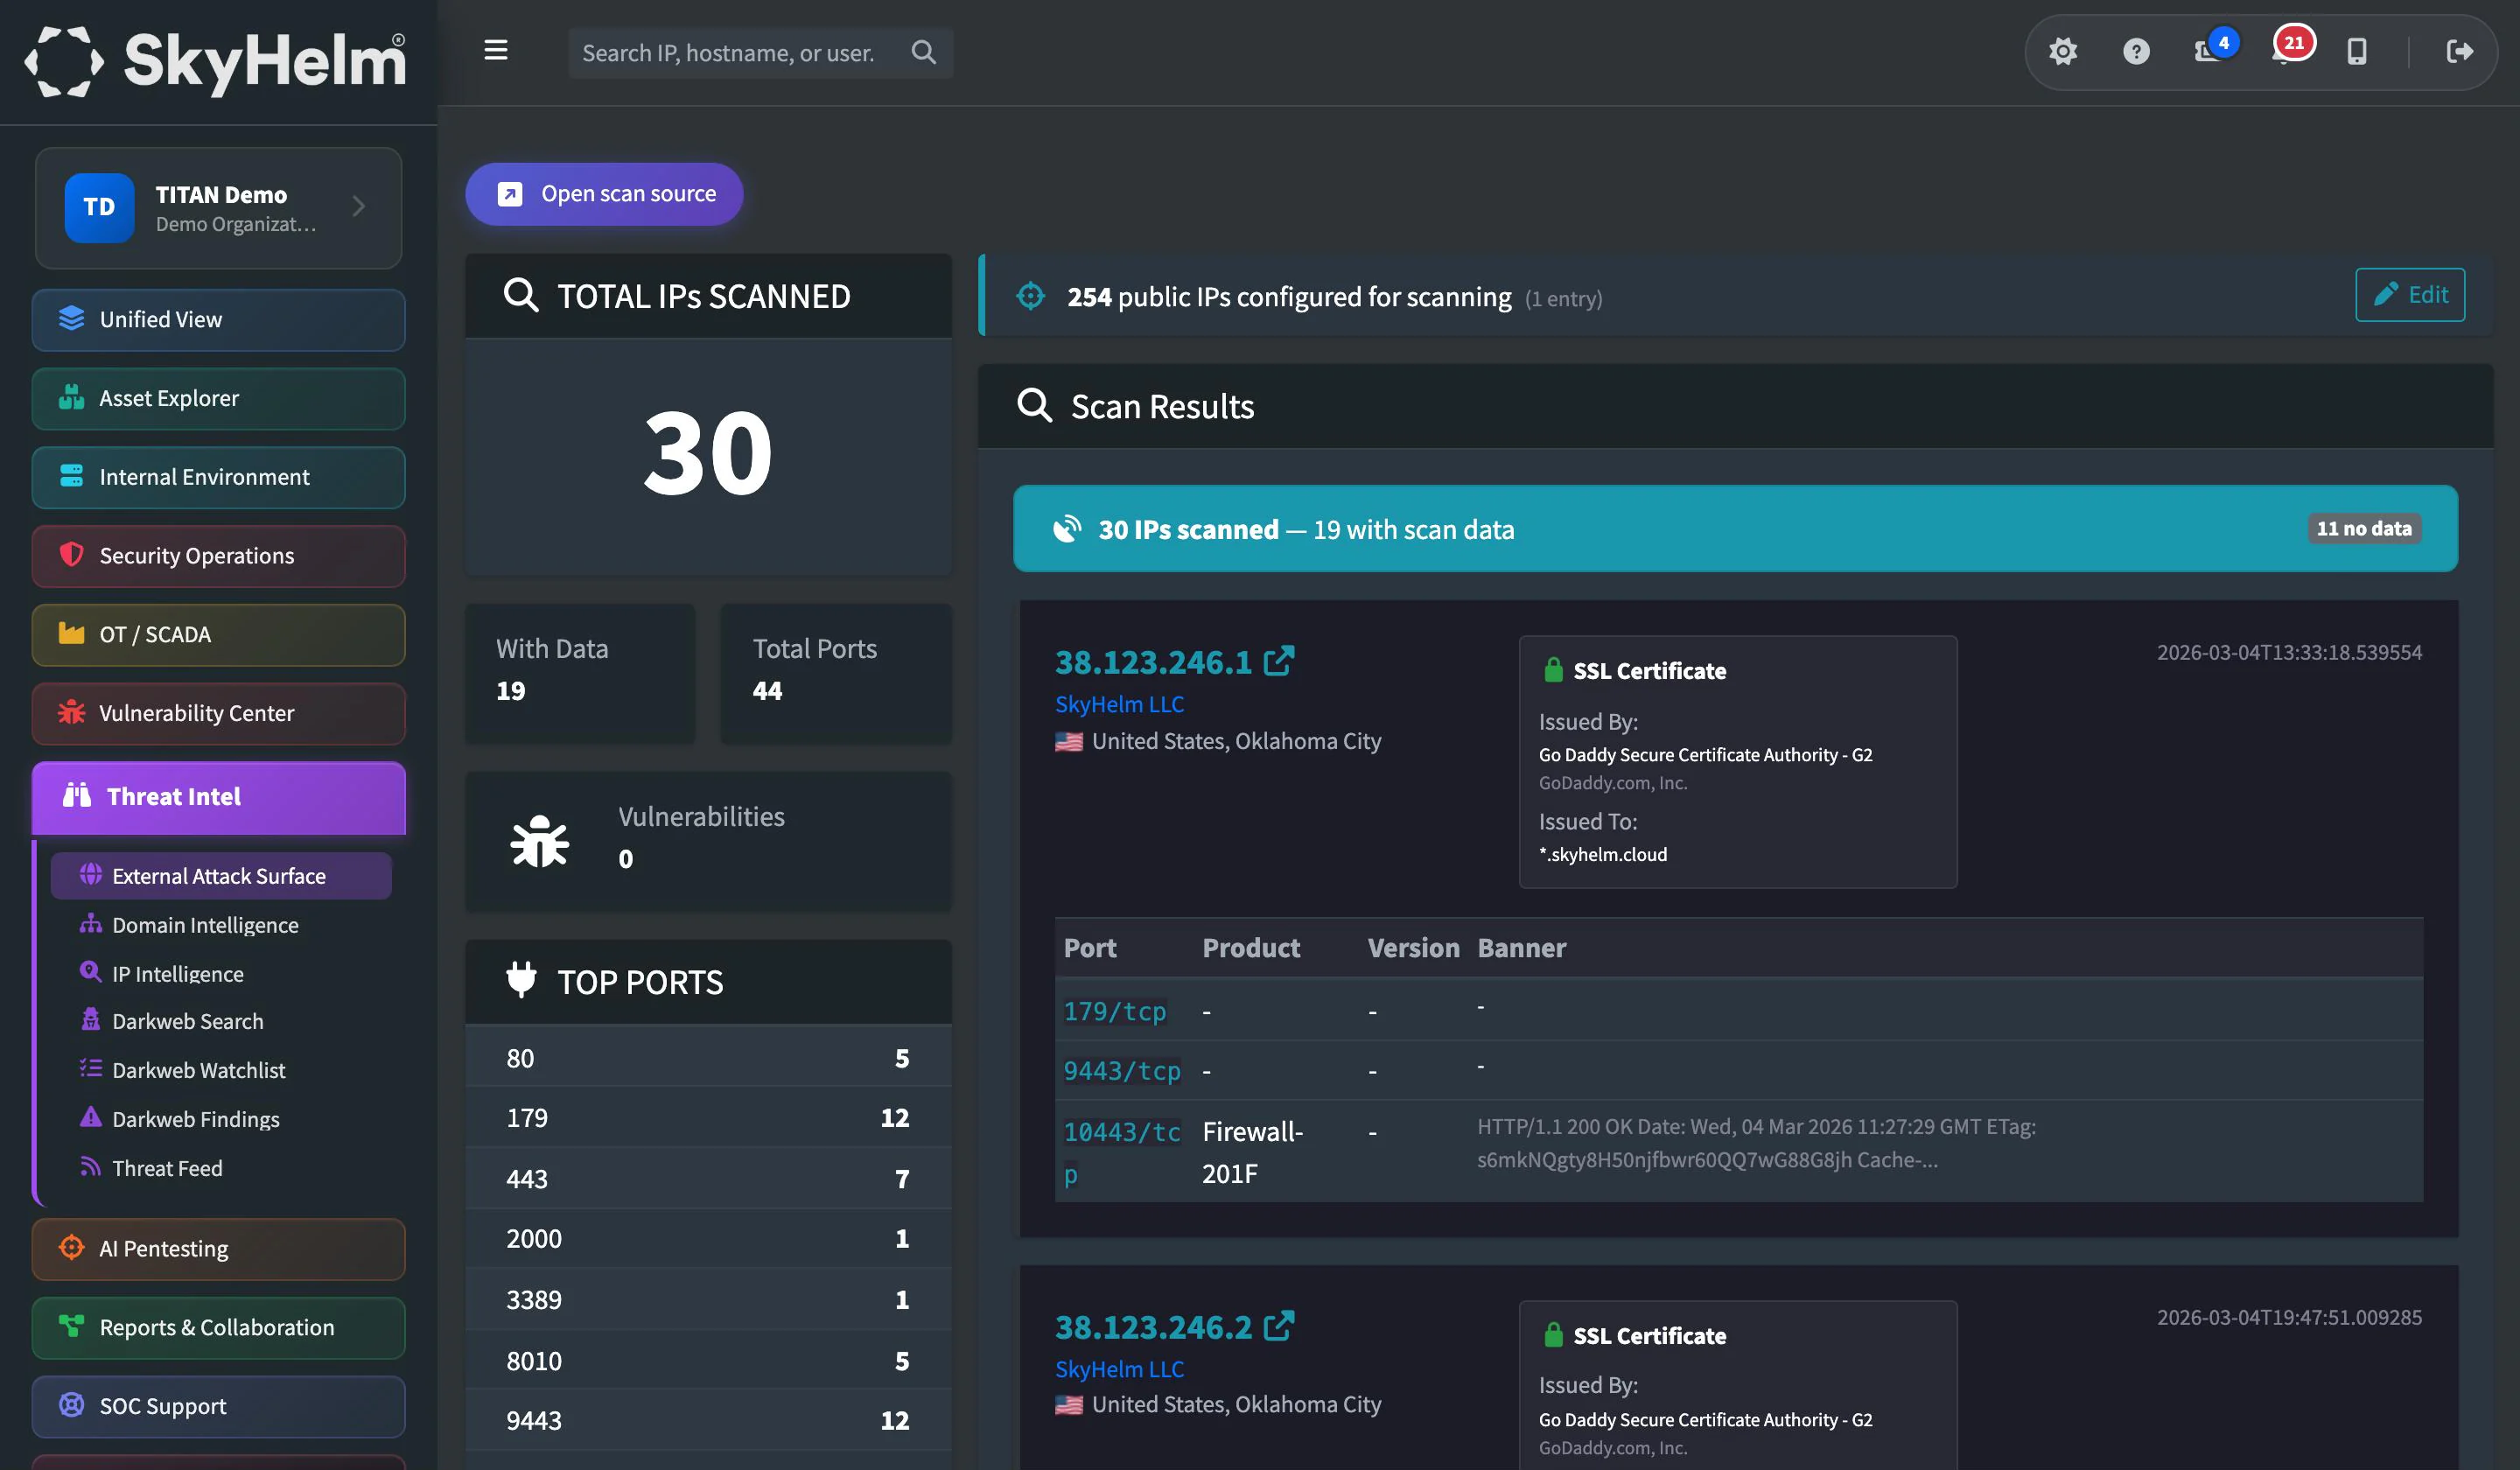
Every organization has more internet-facing exposure than it thinks. Forgotten subdomains, shadow IT services, expired certificates, misconfigured email. TITAN scans your perimeter from the outside in, continuously, and shows you exactly what an attacker would find.
Internet scan data · WHOIS & DNS · Certificate transparency logs · Mail blocklists
The attacker's view, before they get it
Internet-Facing Asset Discovery
Find every IP, port, and service exposed to the internet, including ones you didn't know about. Shadow IT, forgotten test servers, misconfigured cloud instances. If it's reachable, we find it.
Subdomain Enumeration
Discover all subdomains, webmail, VPN portals, SCADA gateways, dev servers. Including the ones your predecessor set up three years ago and forgot to decommission.
Graded Domain Verdict
Every domain gets a graded security verdict, so you can see at a glance which of your domains needs attention first.
Email Authentication Checks
SPF, DKIM and DMARC validation plus mail blocklist (RBL) checks. Misconfigured email authentication is the #1 phishing enabler, we check all of it.
TLS & Certificate Monitoring
Certificate transparency monitoring, TLS configuration and security header checks. Know about weak ciphers and expiring certs before they cause outages or security warnings.
Lookalike Domain Detection
Typosquatting and lookalike domain detection spots the domains attackers register to impersonate your organization in phishing campaigns.
Open Port & Service Detection
Every listening service identified with banner and version fingerprinting. That ancient FTP server on port 2121? The unpatched Apache on a forgotten VM? Found and flagged.
Exposed ICS/SCADA Detection
Exposed ICS and SCADA devices are detected from the outside, and internet-facing devices are flagged in your asset inventory and weighted higher in vulnerability priority.
Continuous Monitoring
Not a one-time scan. Historical exposure data and alerts when your exposure changes: new ports opened, new subdomains discovered, certificates approaching expiration.
Inside External Attack Management
The views your team will use every day.
Every internet-facing IP, open port and service, with history and change tracking.
The exposure you didn't know you had
Shadow IT
Unauthorized cloud services, test servers, personal domains
Found in 73% of our assessmentsForgotten Services
Decommissioned servers still accessible, old VPN portals
Average 12 per organizationExpired Certificates
SSL certs past expiration or using deprecated ciphers
Causes outages and security warningsWeak Email Security
Missing or misconfigured SPF, DKIM and DMARC that lets attackers spoof your domain
The #1 phishing enablerEverything in External Attack Management
20 capabilities, every one included in TITAN.
Internet exposure
8- Continuous public-facing asset discovery (IPs, services, ports)
- Banner/service fingerprinting
- Historical exposure data and change tracking
- Exposed ICS/SCADA device detection
- Alerting on newly exposed services
- Geographic and ISP attribution
- Internet-facing devices flagged in the Asset Explorer and weighted higher in vulnerability priority
- External Attack Surface report section
Domain intelligence
12- WHOIS and DNS record monitoring
- Typosquatting / lookalike domain detection
- Certificate transparency monitoring
- Passive DNS history
- Subdomain enumeration
- Domain reputation and abuse lookup
- URL scanning and sandboxing
- Graded domain security verdict
- Email authentication checks (SPF, DKIM, DMARC)
- TLS configuration and security header checks
- Mail blocklist (RBL) checks
- Host discovery and a domain map
Works hand in hand with
Discover your real attack surface
Schedule a scan and see exactly what an adversary would find when they target your organization. Most IT directors are surprised.