Security Information & Event Management. From noise to signal.
Every log from every tool, correlated in real time into the incidents that matter.
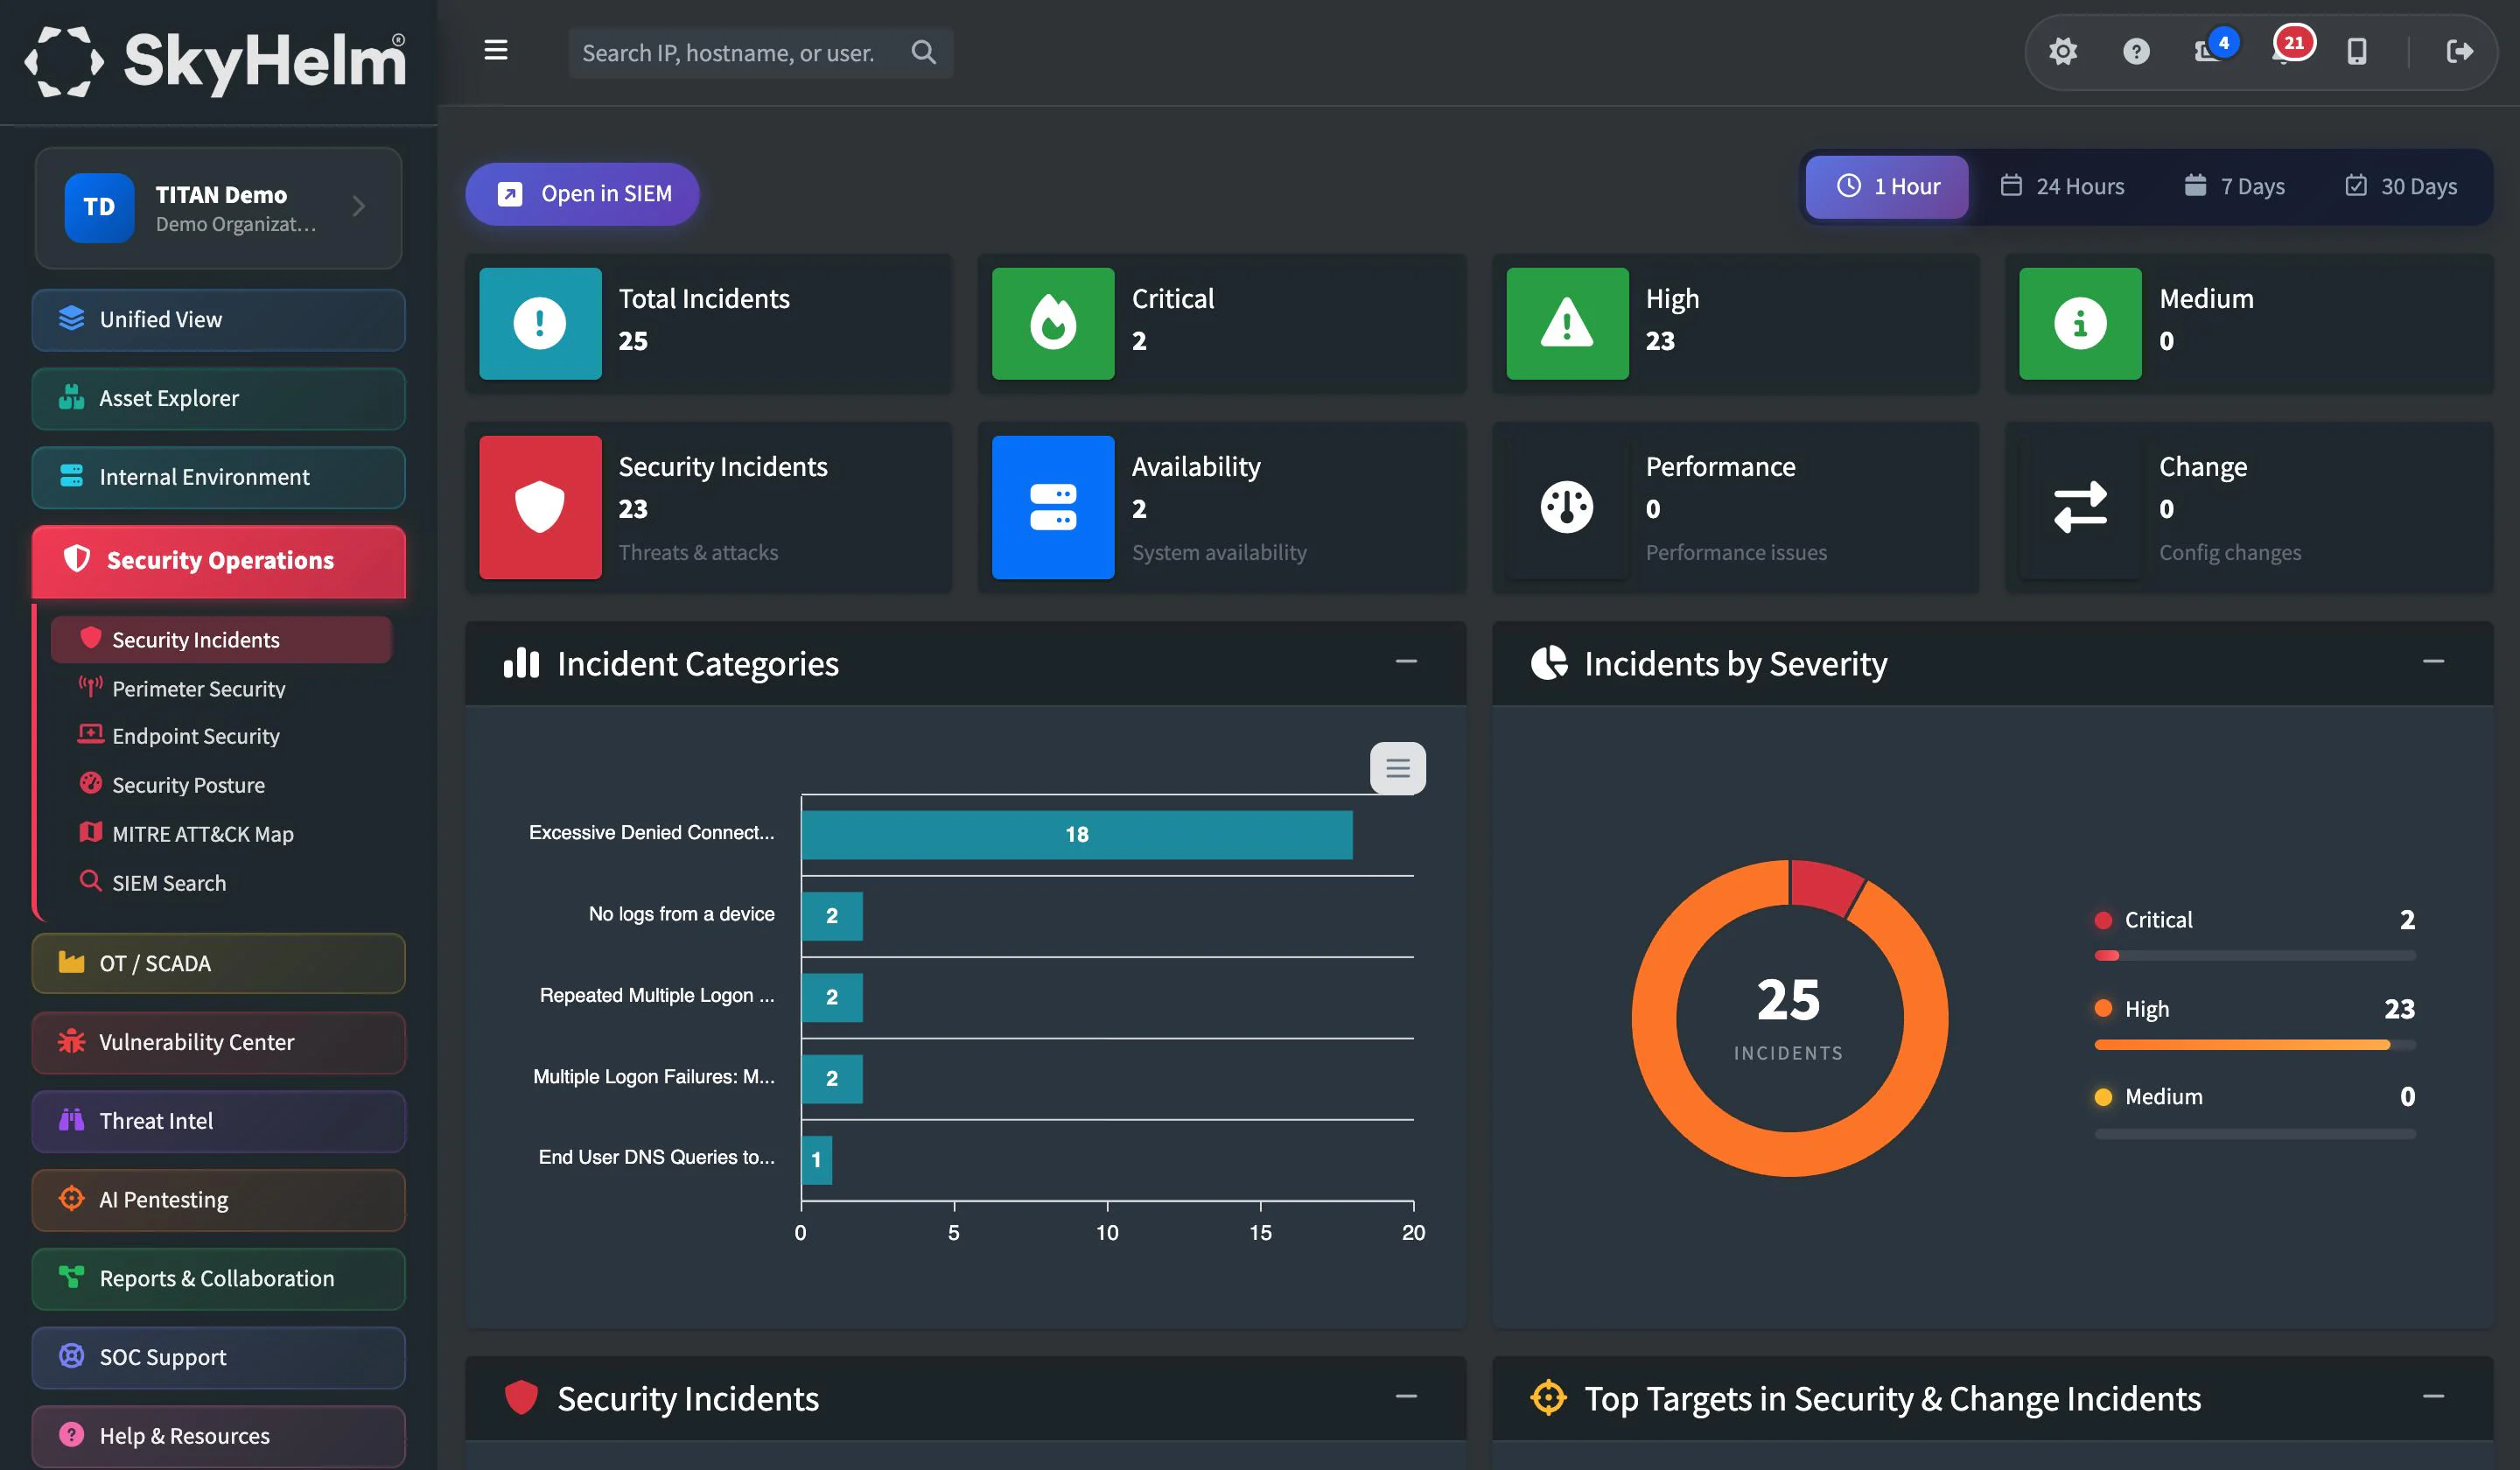
The brain of your security stack. TITAN aggregates logs from every device in your environment, correlates events in real time, and surfaces the incidents that matter, so your team isn't drowning in 10,000 alerts to find the three that are real.
Firewalls · Switches · Servers · Endpoint log agents · Applications · OT systems · Cloud services
Every event. Every device. One timeline.
Universal Log Aggregation
Collect and normalize logs from every device type, firewalls, switches, servers, endpoints, applications, OT systems, cloud services. Hundreds of log sources, one unified format.
Real-Time Correlation
Correlation rules detect multi-stage attacks by linking events across sources automatically. A failed VPN login followed by a successful one from a different geo, followed by unusual file access? TITAN connects the dots.
User & Entity Behavior Analytics
UEBA learns how each user and device normally behaves and flags the departures, like an account suddenly signing in at 3 AM or reaching for files it has never touched.
Incident Timeline
Full chronological view of every event in an incident, from the first indicator to resolution. Every log entry, every alert, every analyst action laid out on a single timeline.
MITRE ATT&CK Mapping
Incidents automatically mapped to ATT&CK techniques for standardized classification and gap analysis. See which techniques your detections cover and where your blind spots are.
Custom Correlation Rules
Build rules specific to your environment, SCADA command anomalies, after-hours substation access, VPN abuse patterns, impossible travel detection, tailored to how your organization actually operates.
Compliance Reporting
Report templates for NERC CIP, HIPAA, PCI and audit evidence packages, backed by long-term log retention. Generate the documentation your auditors need without pulling your IT team off real work.
Automated Response
Trigger automated actions when specific patterns are detected, block an IP, isolate a host, create a ticket, notify the SOC. Playbooks that execute at machine speed.
SIEM Search & Threat Hunting
Months of searchable log data, with IP, host, user and incident search modes. When you need to know 'did this IOC appear in our environment last quarter?', the answer is instant.
Inside Security Information & Event Management
The views your team will use every day.
Every incident, with full drill-downs and context search.
Watch five events become one incident
Know your coverage. Know your gaps.
The MITRE ATT&CK Map lays your alerts over the ATT&CK matrix by tactic and technique. See which adversary techniques your rules detect, where gaps exist, and how your coverage improves over time. Essential for NERC CIP and other compliance evidence, board reporting, and knowing exactly where your organization stands.
Everything in Security Information & Event Management
11 capabilities, every one included in TITAN.
Log management & detection
10- Centralized log collection from all connected tools
- Real-time event correlation across data sources
- User and Entity Behavior Analytics (UEBA)
- Endpoint log agents for deep host telemetry
- Customer-accessible log search and query
- Long-term log retention for compliance
- Custom detection rule authoring
- Compliance reporting (NERC CIP, HIPAA, PCI, etc.)
- Security Incidents dashboard with full incident drill-downs and context search
- SIEM Search: one search box with IP, host, user and incident modes, integrated with all other TITAN tools
Investigation
1- MITRE ATT&CK Map: your alerts laid over the ATT&CK matrix by tactic and technique
Works hand in hand with
See how TITAN cuts through the noise
Schedule a demo and we'll show you real-time correlation, attack timeline reconstruction, and ATT&CK mapping in action.