IDS/IPS & Perimeter Security. Stop attacks at the edge.
Intrusion prevention, deep packet inspection and AI-assisted threat hunting, plus VPN and Entra ID sign-ins, across every firewall.
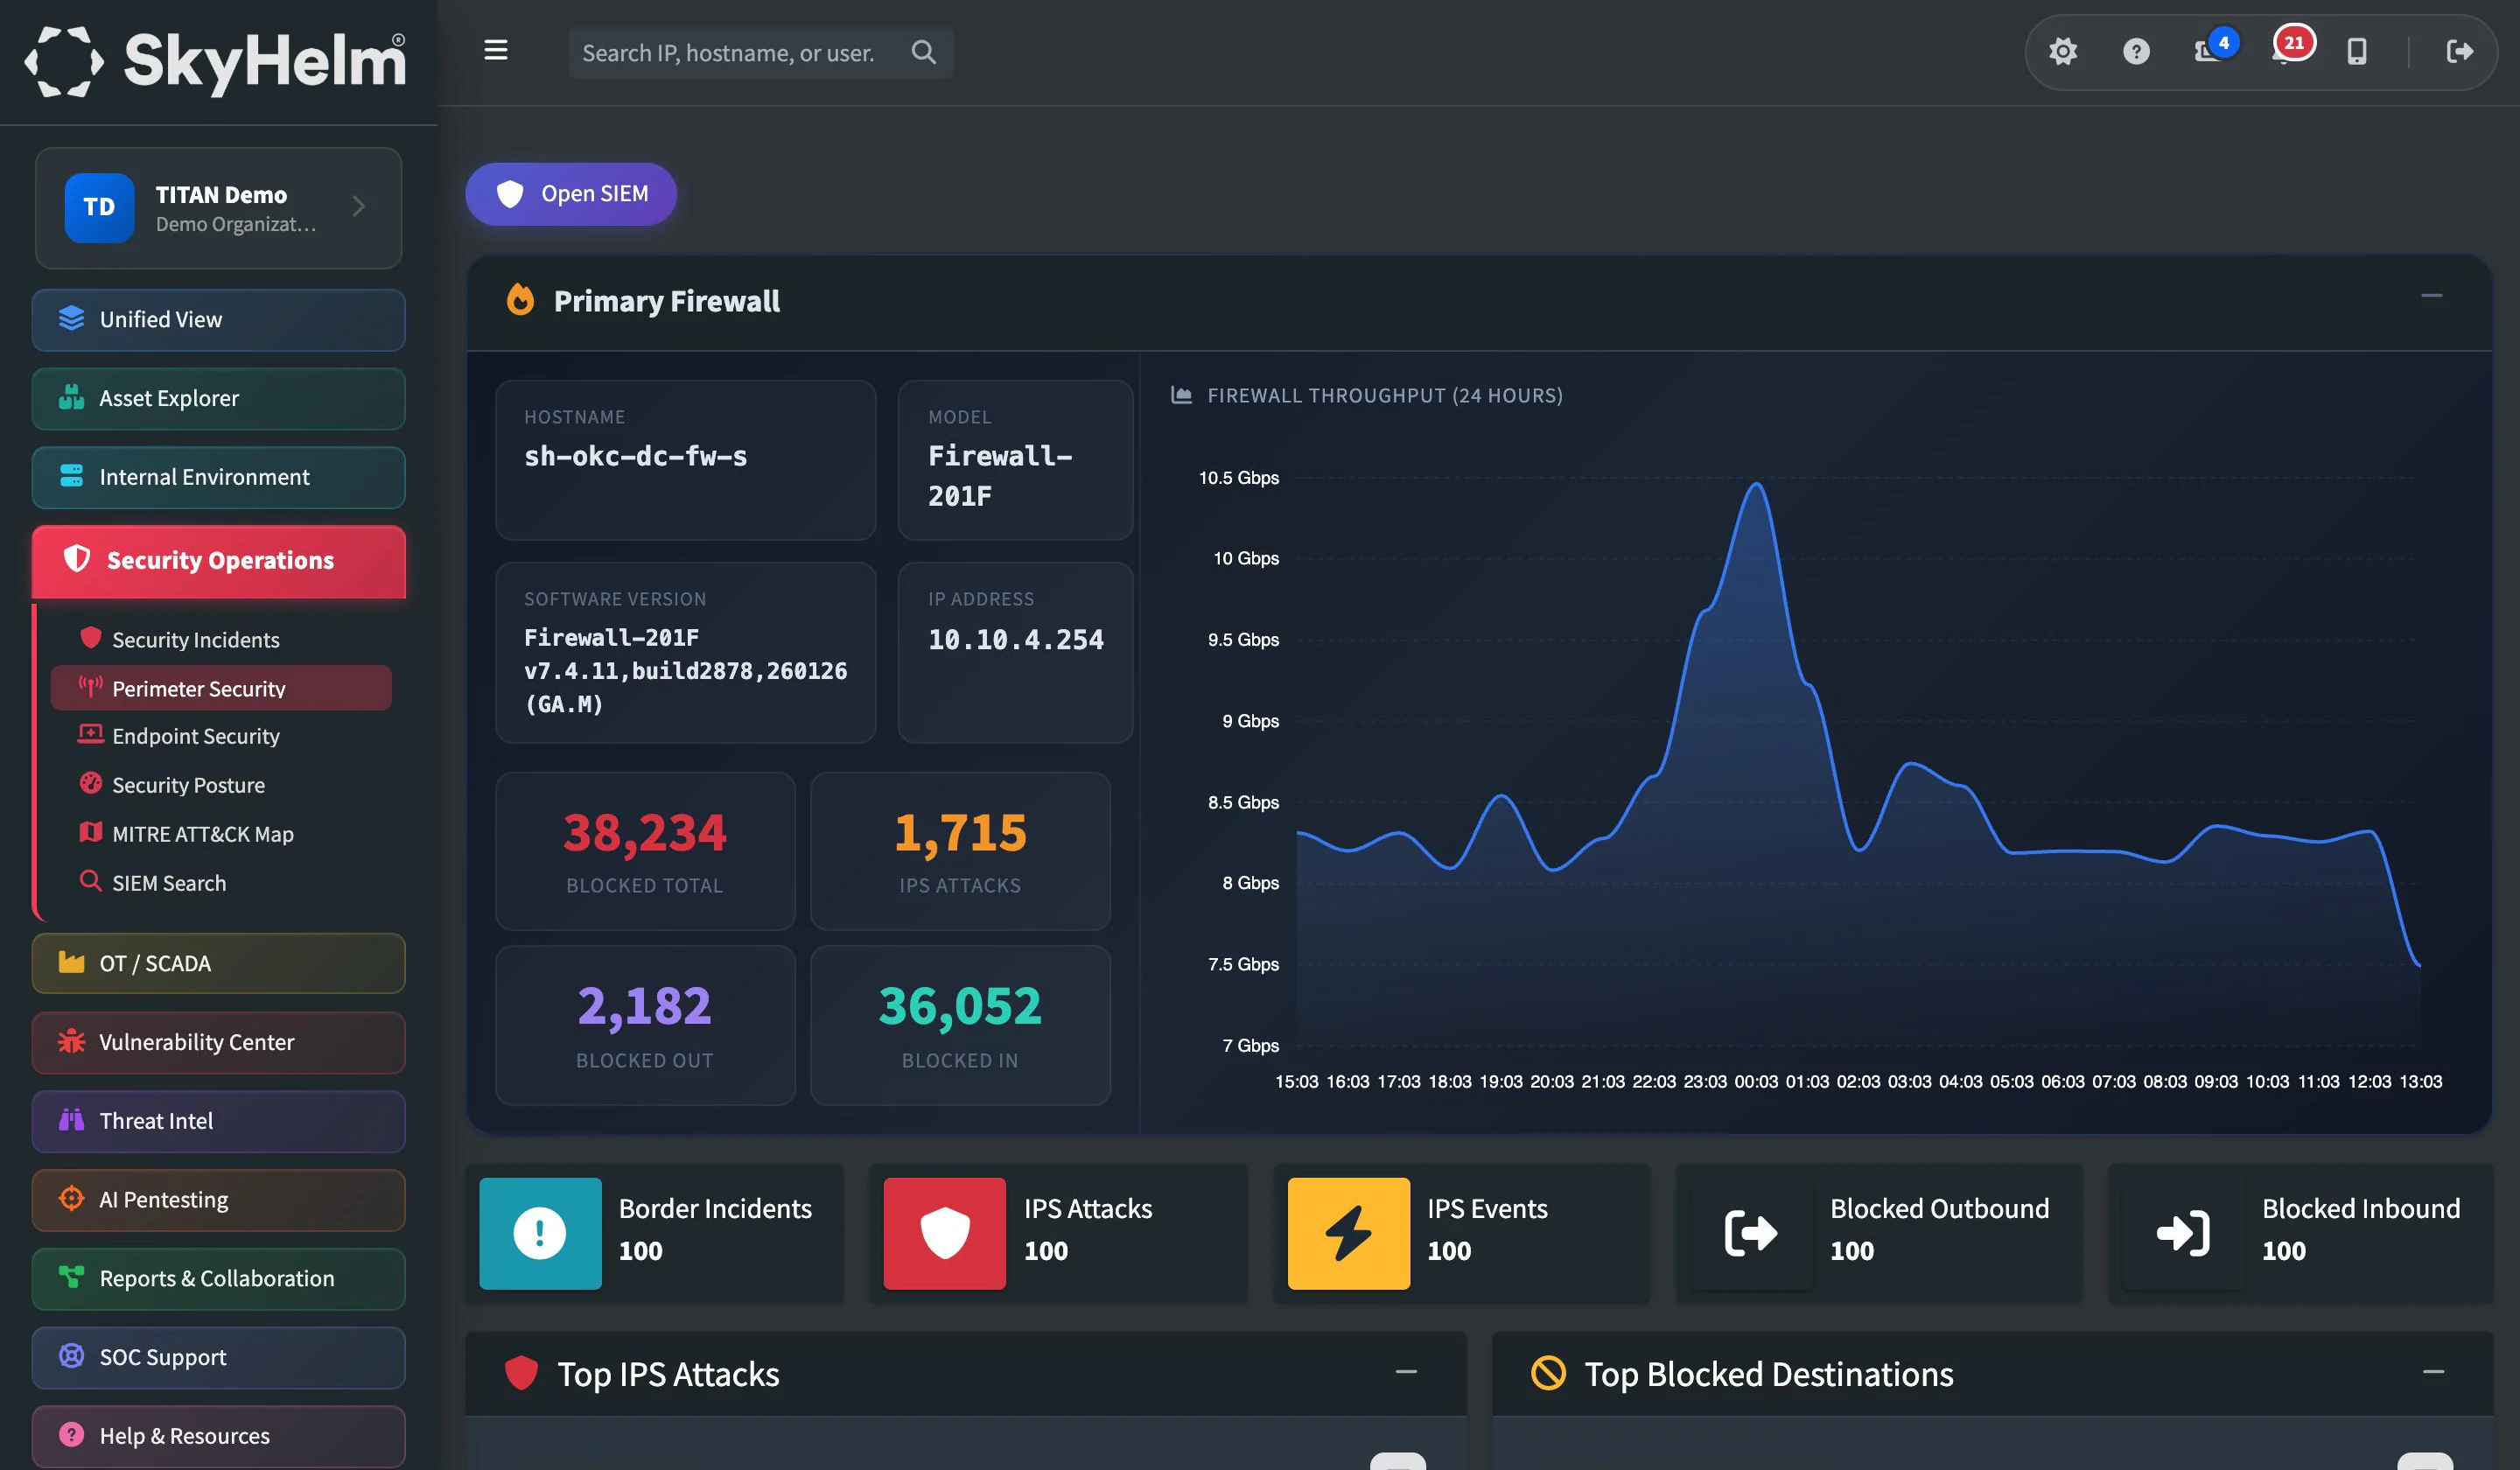
Firewall, intrusion prevention, VPN and sign-in monitoring across every site in your organization. TITAN inspects the traffic crossing your perimeter in both directions: signatures catch known attacks, anomaly detection catches the unknown ones, and AI helps your team hunt through it all.
Next-gen firewalls · SIEM · Network monitoring · Cloud identity sign-ins
Inspect everything. Block what matters.
Most attacks cross the network before they ever reach an endpoint. TITAN watches the wire at every site.
Next-Gen Firewall Monitoring
Real-time visibility into blocked inbound and outbound traffic, border incidents, and IPS events. See exactly what's crossing your perimeter, and what's being blocked, across every site.
Intrusion Detection & Prevention
IPS/IDS across all traffic flows detecting exploit attempts, protocol anomalies, and known attack signatures. Threats are blocked before they reach internal systems.
Deep Packet Inspection
Every packet inspected beyond the header, so exploits hiding inside allowed traffic are caught before they reach internal systems.
Signature + Anomaly Detection
Signatures stop known attacks while automated anomaly detection flags traffic that breaks from your normal patterns, catching attacks no signature exists for yet.
SSL/TLS Inspection
Decrypt and inspect encrypted traffic for hidden threats. Over 80% of malware uses encryption, if you can't see inside TLS, you're flying blind on the majority of your traffic.
Application Control
Visibility and policy enforcement by application, not just port and protocol. Block unauthorized apps, throttle bandwidth hogs, and ensure critical SCADA traffic gets priority.
AI-Assisted Threat Hunting
AI helps analysts hunt across firewall and IPS data, surfacing the patterns worth a closer look instead of leaving them buried in logs.
VPN & Sign-In Monitoring
Remote access VPN sessions and Microsoft Entra ID sign-ins in one place. Know who's connected and from where, and spot a burst of failed logins, impossible travel or a sign-in from the wrong country.
Geo-IP Blocking
Block traffic from high-risk countries and regions with one policy, backed by threat feed integration. When your organization has zero business with certain geographies, there's no reason to accept their traffic.
Outbound Destination Tracking
See every blocked destination and which countries your outbound traffic reaches. Data leaving for the wrong place is often the first sign of a compromise.
BGP Hijack Detection
Route monitoring watches the internet routes to your address space and flags hijacks that could quietly redirect your traffic.
Multi-Site Correlation
Firewall logs from headquarters, substations and remote offices analyzed together, so an attacker probing three substations reads as one campaign, not three unrelated alerts.
Inside IDS/IPS & Perimeter Security
The views your team will use every day.
Blocked inbound and outbound traffic, border incidents and IPS events.
From packet to blocked attack
Every flow through every firewall passes through the same layered checks, and anything worth knowing about lands in TITAN Alerts and in front of the SOC.
Traffic
Every flow crossing every firewall, at headquarters and every substation.
Deep Inspection
Packets inspected beyond the header, including inside encrypted TLS.
Detection
Signatures catch known attacks; anomaly detection catches the rest.
AI Hunting
AI-assisted hunting surfaces the patterns worth a closer look.
Block & Alert
Threats blocked at the edge, with alerts in TITAN and to the SOC.
Your whole perimeter on one screen
Inbound and outbound blocks, border incidents, IPS events and sign-ins across every firewall, without logging into each one.
Everything in IDS/IPS & Perimeter Security
17 capabilities, every one included in TITAN.
Intrusion detection & prevention
9- Deep packet inspection
- Intrusion detection and prevention (IDS/IPS)
- Application control and filtering
- Web filtering and content inspection
- TLS/SSL inspection
- AI-assisted threat hunting on firewall/IPS data
- Automated traffic anomaly detection
- Anomaly and Signature Based Detection
- Cross-firewall correlation across multiple sites
Perimeter monitoring
8- VPN & Remote Access Threat Detection
- BGP Hijack Detection & Route Monitoring
- Centralized multi-site firewall log analytics
- Geo-IP blocking and threat feed integration
- Perimeter Security dashboard: blocked inbound and outbound traffic, border incidents and IPS events
- VPN and Microsoft Entra ID sign-in monitoring (successful and failed logins)
- Blocked-destination and outbound destination-country tracking
- Perimeter Activity report section covering the whole reporting period
Works hand in hand with
See what's crossing your perimeter
Schedule a demo and we'll show you how TITAN inspects, detects and blocks attacks across every firewall in your organization, with VPN and sign-in monitoring in the same view.