Find the way in before an attacker does.
An AI pentester that attacks your network the way a real adversary would, safely and as often as you like. It proves which weaknesses lead to real damage, shows you how to fix them, and checks that the fix worked.
Attackers rarely need a zero-day. They chain a weak password, a missing patch and a forgotten setting into a path to your most important systems. Our AI pentester finds those paths first.
See what an attacker could reach.
Every pentest lands in TITAN beside the rest of your security picture: what was reached, how fast, which weaknesses were proven and what changed since the last test.
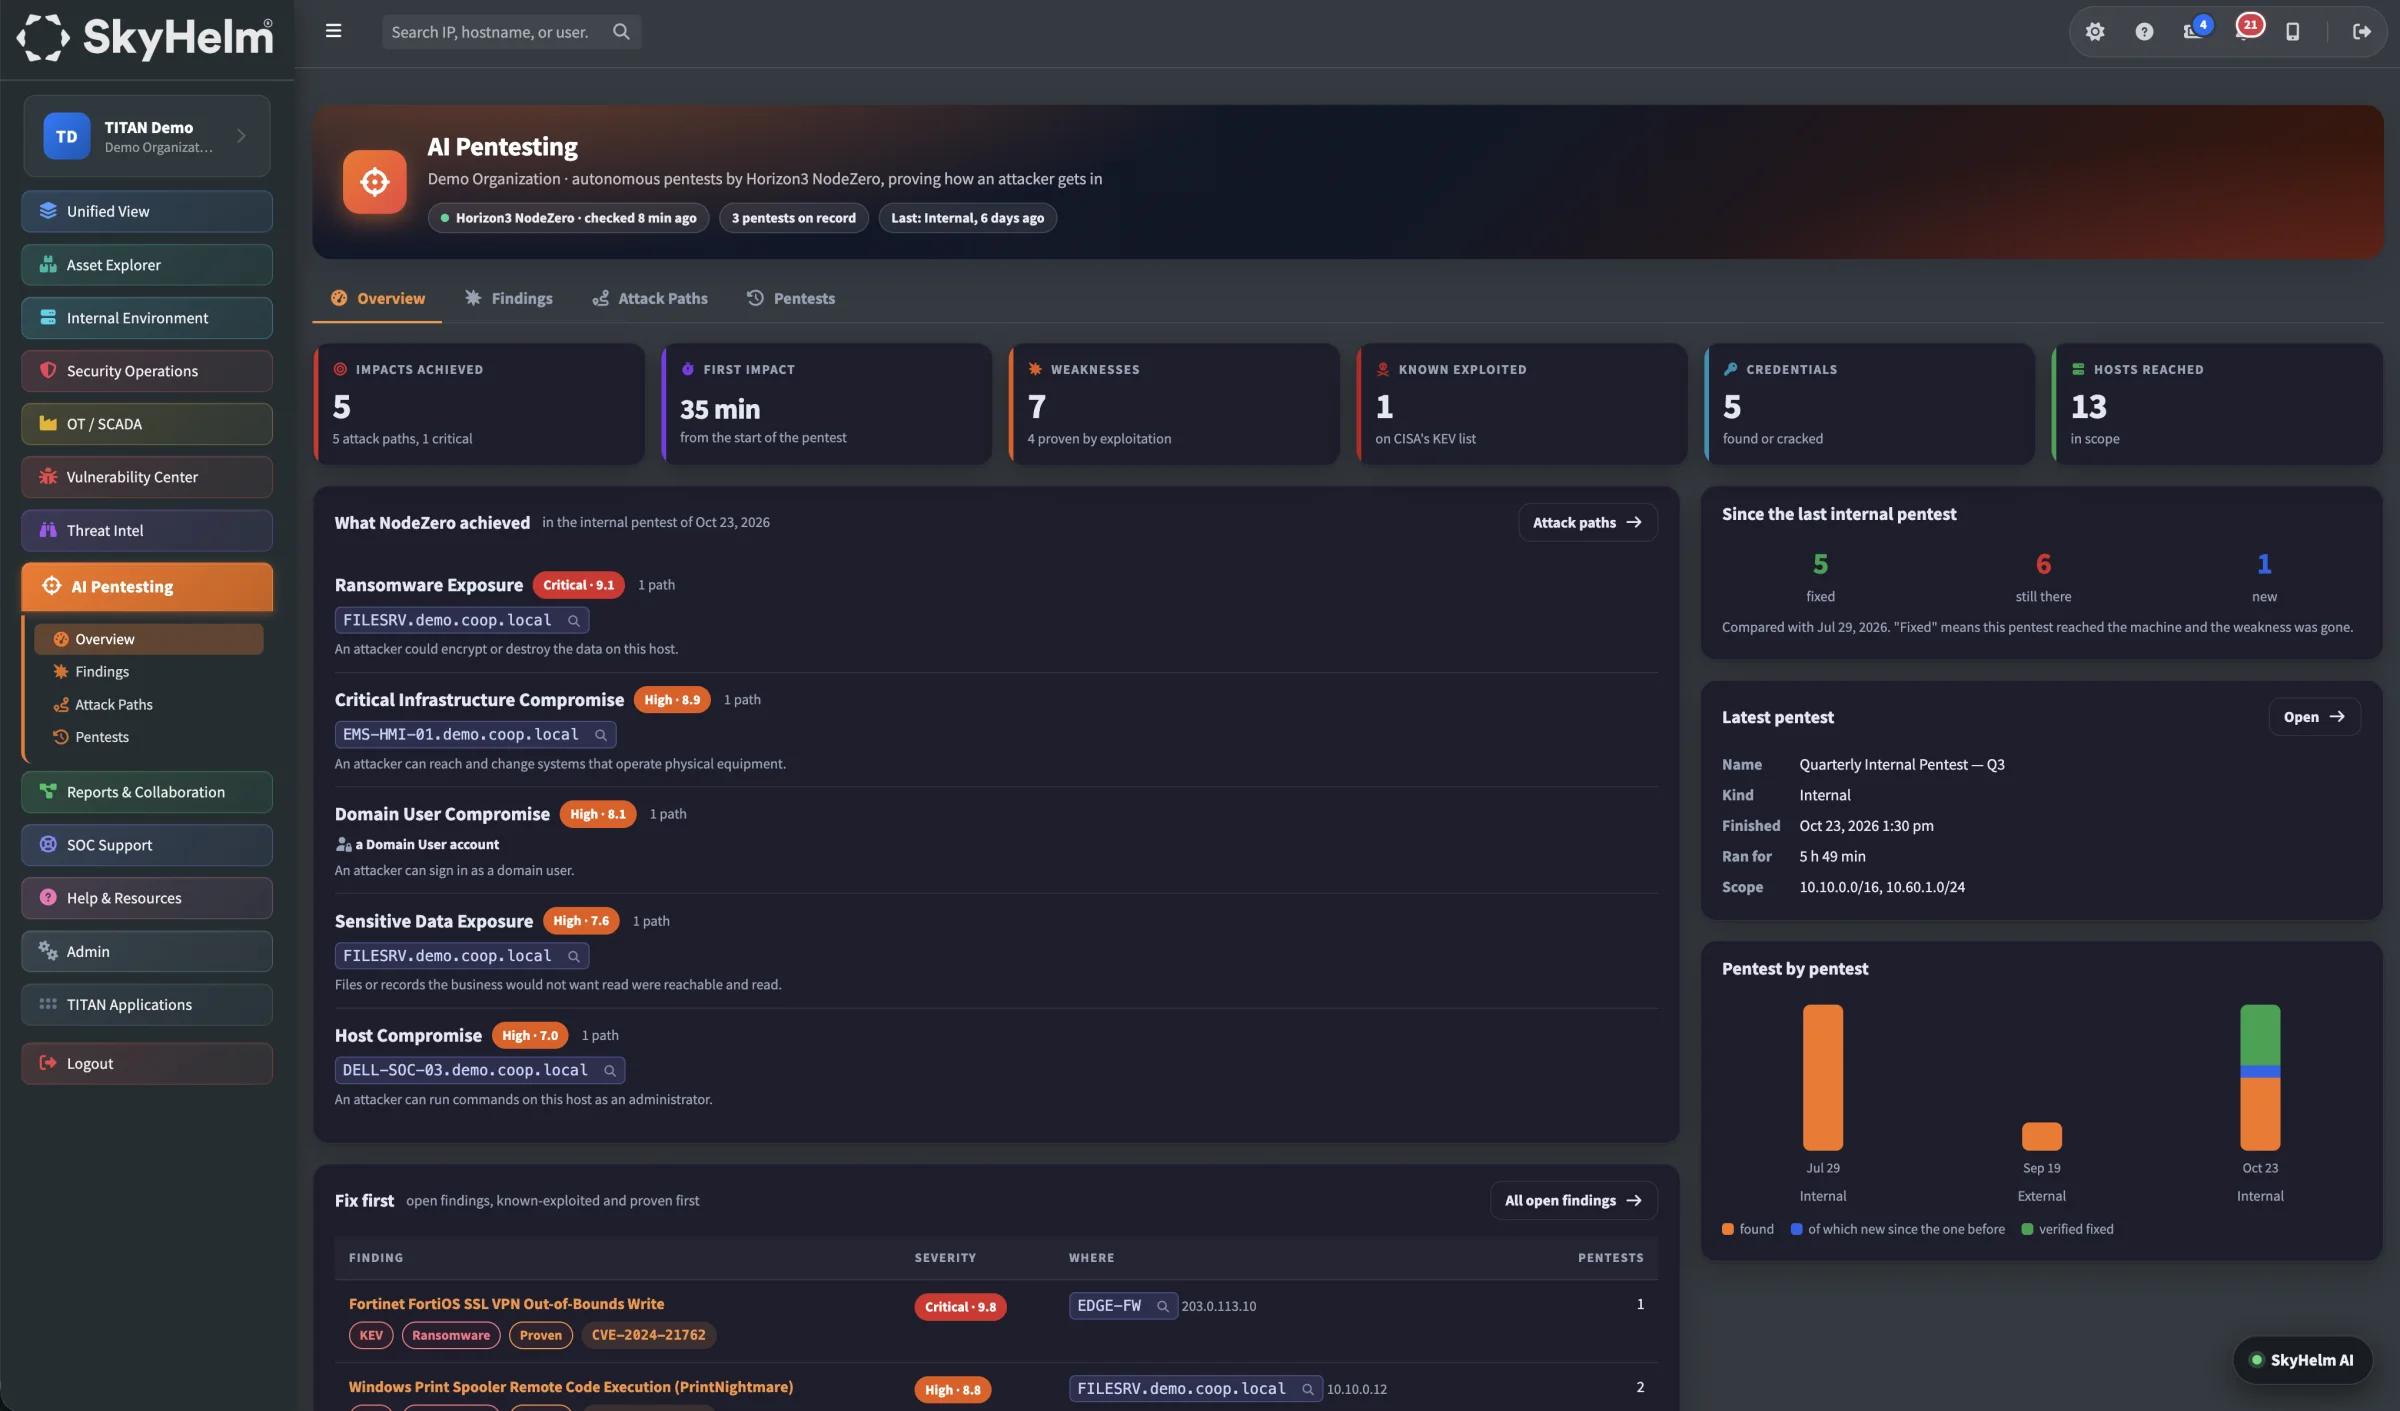
Scope it, run it, fix it, prove it.
A full internal pentest without weeks of scheduling, and a retest whenever you need one.
Plan the test together
We set the scope with your team: which networks are in, which are out, and how to treat sensitive OT segments.
Up and running in minutes
Internal tests run from a small virtual machine or container on your network, with no agents to install. External tests run from the cloud.
It thinks like an attacker
The AI explores your network on its own, chains weaknesses together and safely exploits them to prove they are real. You can watch its progress as it goes.
Every path, with proof
Each attack path is laid out step by step, with evidence of what was exploited and what it would mean for your organization.
Fix what matters most first
Findings are ranked by impact, with detailed fix guidance. Systemic fixes are called out, where one change can close many paths at once.
Confirm the fix worked
Rerun the test to prove each weakness is gone, then schedule pentests to keep running so new gaps are caught early.
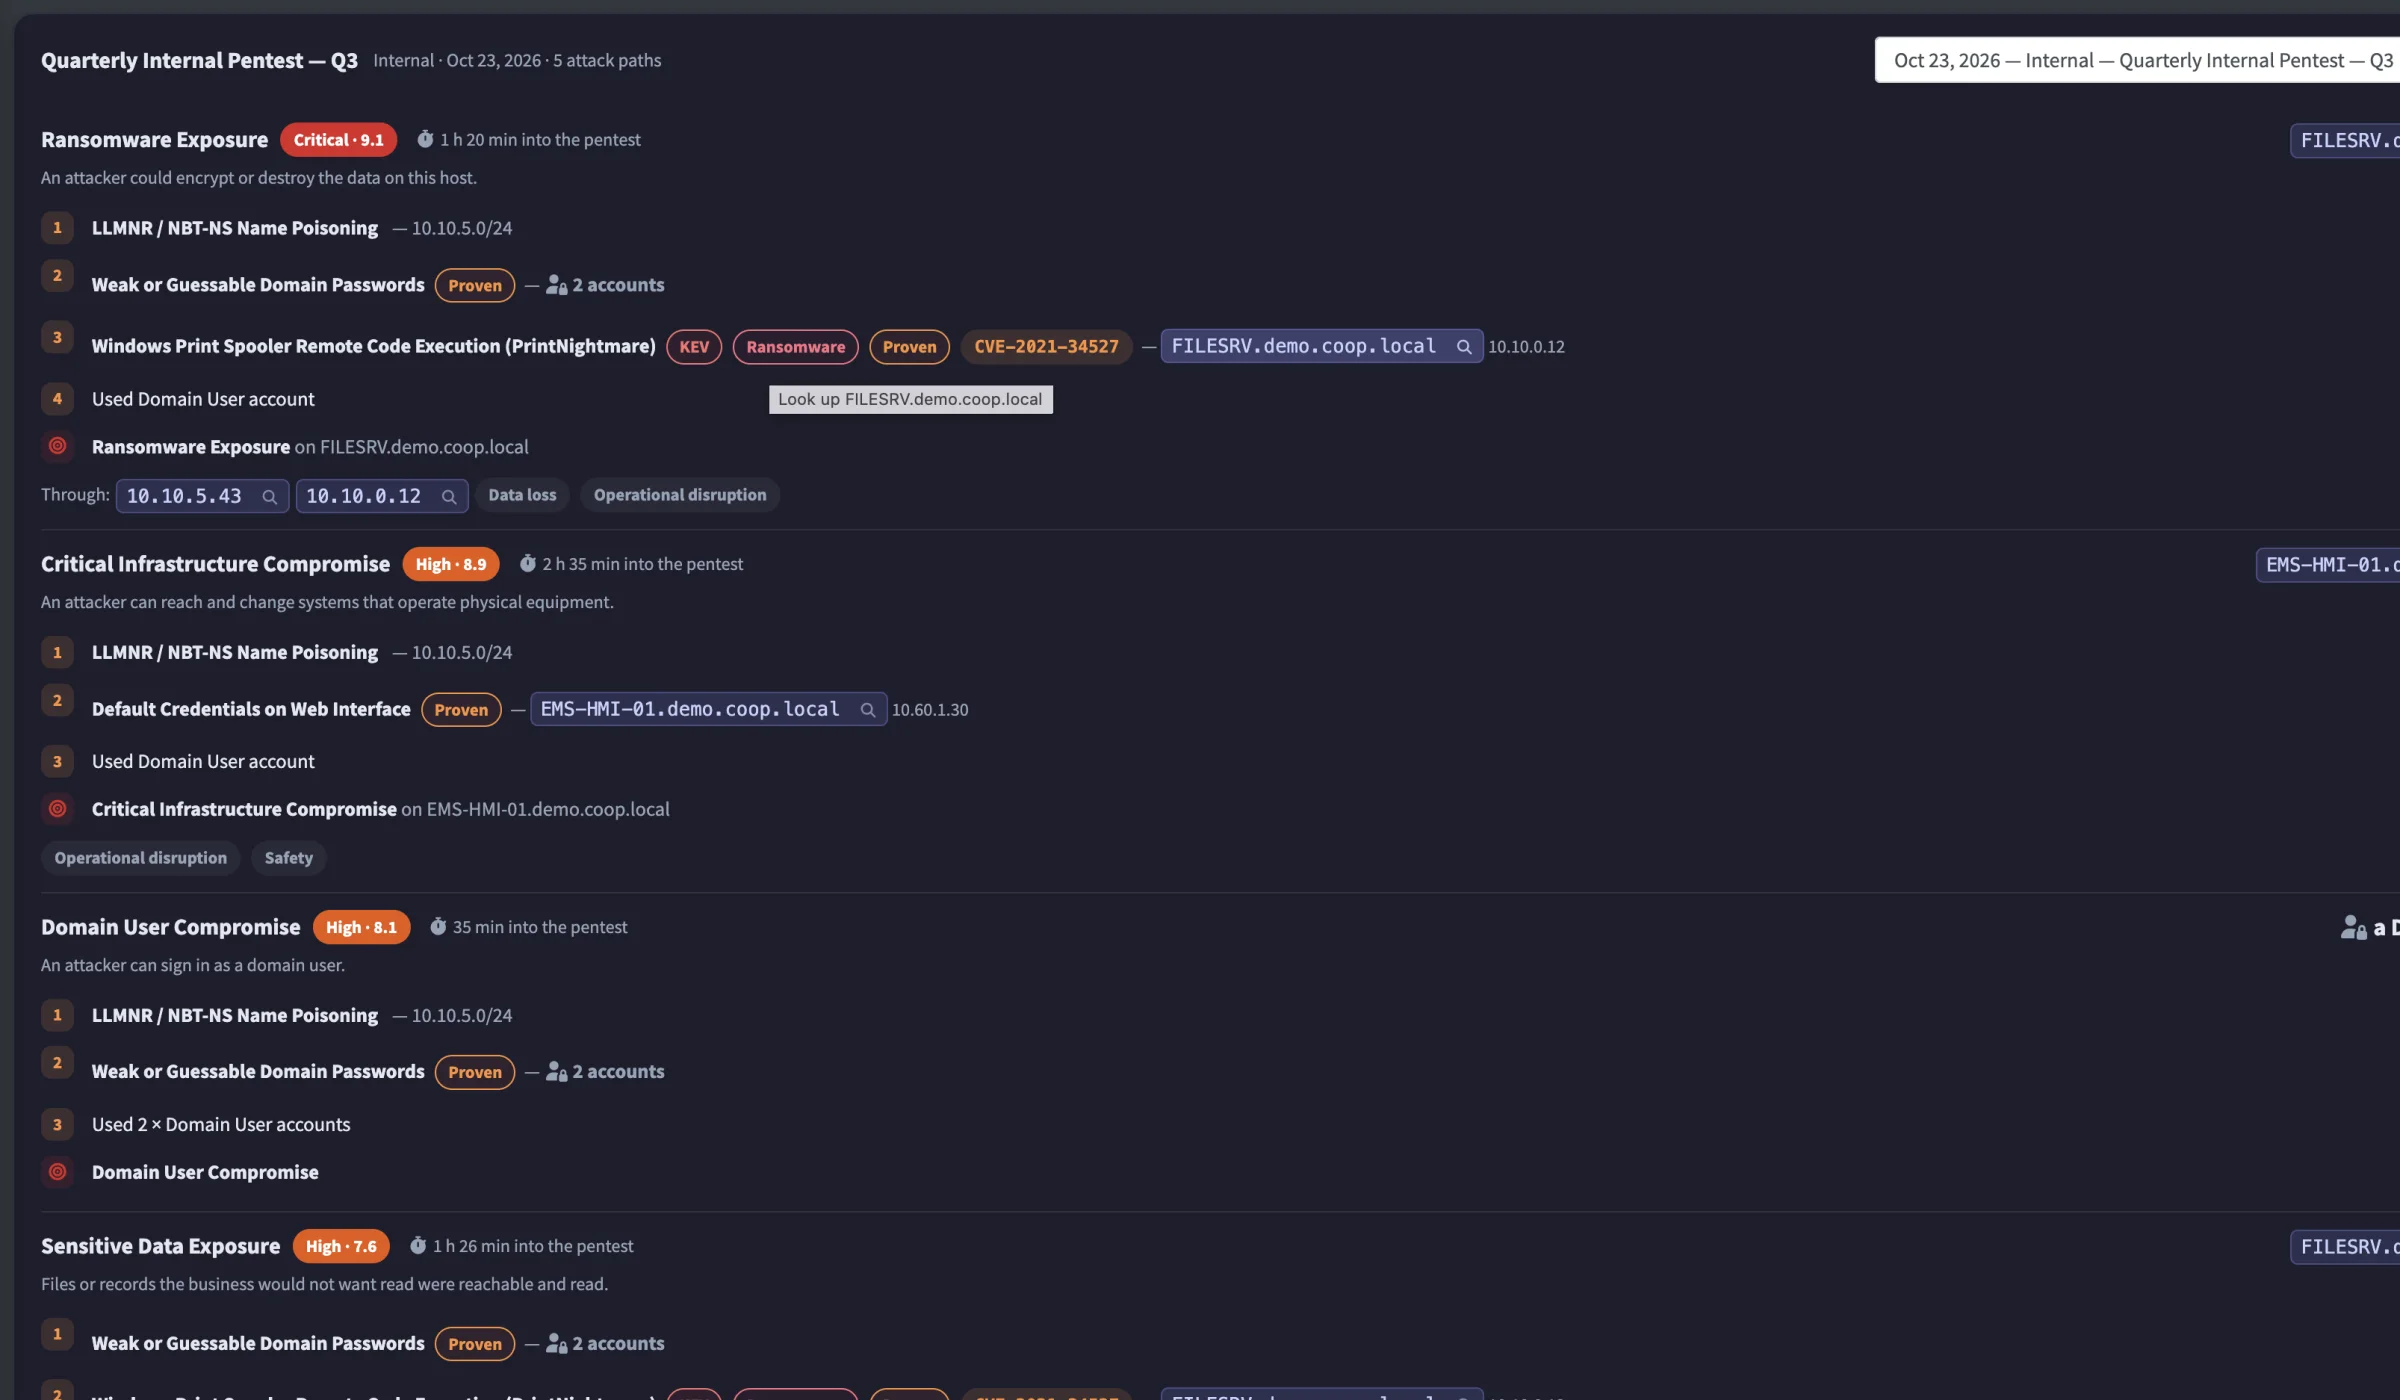
Every step an attacker would take.
See exactly how a foothold turned into ransomware exposure or access to control systems, how long it took, and which machines it went through.
More than a vulnerability scan.
Scanners list what might be wrong. A pentest proves what an attacker can actually do with it, including the weaknesses that are not a missing patch.
Internal pentesting
Starts inside your network, with or without credentials, and finds how far an attacker could get from there.
External pentesting
Tests what is exposed to the internet, the same view an attacker has before they get in.
Cloud pentesting
Finds the misconfigurations and over-privileged identities that open a path into your cloud environment.
Kubernetes pentesting
Tests container clusters for escapes, exposed secrets and paths to the rest of your network.
Credentials and passwords
Finds weak, reused and easily cracked passwords, and audits your Active Directory passwords against your policy.
Phishing impact
Shows what an attacker could reach if someone on your team gave up their credentials to a phishing email.
Rapid response
When a new vulnerability is being exploited in the wild, find out quickly whether you are affected and where.
Tripwires
Leaves decoys behind on high-value machines that raise an alert the moment a real attacker touches them.
Beyond CVEs
Misconfigurations, exposed data, weak controls and risky policies, not only the known vulnerabilities a patch fixes.
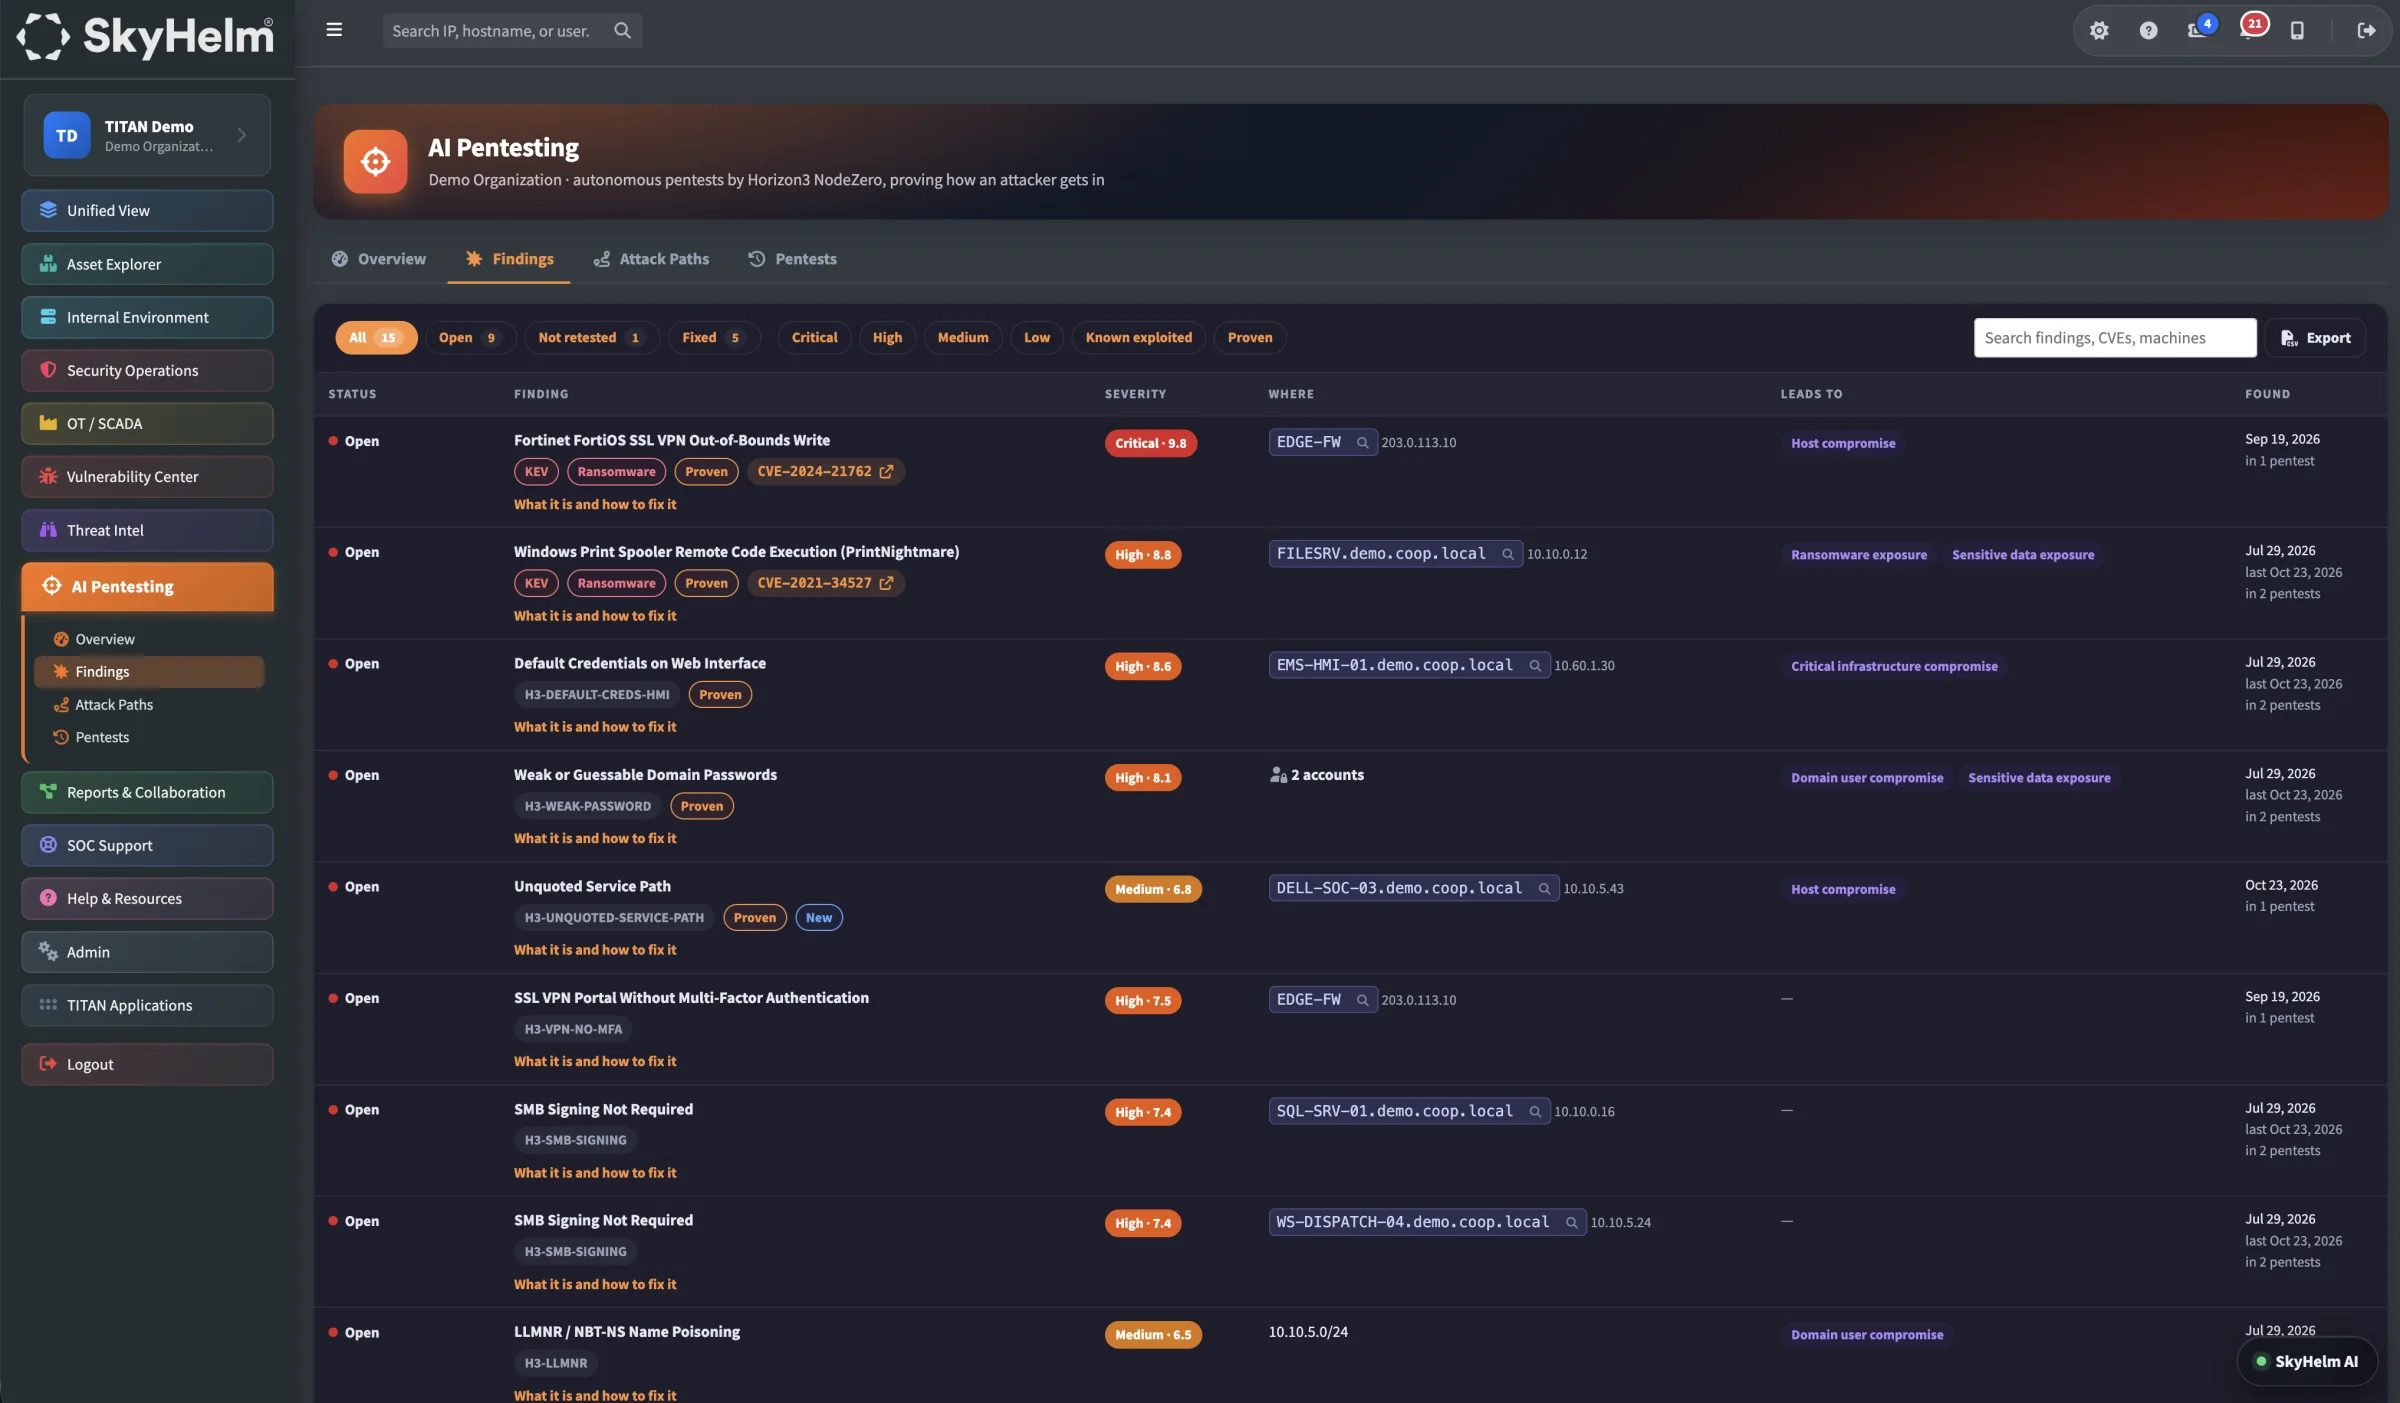
Fix first what attackers use first.
Every finding shows its severity, whether it is known to be exploited, where it was found, what it leads to and how to fix it, and whether a later pentest confirmed the fix.
A pentest is only as good as the fixes that follow.
Most pentests end with a long report and no one to help act on it. With SkyHelm, results flow straight into TITAN, our SOC analysts review what was found, and our engineers can help close the gaps.
Because the pentest can run again whenever you like, you can show your board, auditors and insurers real progress over time, not a snapshot from last year.
- Pentest results in TITAN, beside every other tool you run
- Review of every pentest by SkyHelm security analysts
- Hands-on help fixing what is found
- Scheduled retests to prove fixes and catch new gaps
- Pentest-over-pentest trends for leadership and auditors
- Scoping that respects fragile OT and SCADA systems
Services that fix what a pentest finds.
See what an attacker would find.
Talk with our team about scoping your first AI pentest.