We study the attackers so you don't have to.
SkyHelm's researchers track the groups, campaigns and vulnerabilities aimed at critical infrastructure. Then they turn what they learn into detections, TITAN intelligence and plain-English advisories for your team.
Every finding ends up somewhere useful: a detection in our SOC, an indicator in TITAN, or a briefing your team can act on today.
The threats aimed at organizations like yours.
Our research focuses on the actors and techniques that target critical infrastructure.
Threat actors
Nation-state and criminal groups that target critical infrastructure: who they are, what tools they use and who they're going after.
Ransomware groups
Profiles of active groups, their recent victims, how they get in and the vulnerabilities they exploit.
Exploited vulnerabilities
Flaws being exploited right now, especially in internet-facing VPNs, firewalls and remote access tools.
OT and ICS threats
Malware and techniques built for control systems, and abuse of industrial protocols such as Modbus and DNP3.
Phishing campaigns
The lures, look-alike domains and credential-harvesting pages being used to get a first foothold.
Attacker infrastructure
Command-and-control servers and attacker IP addresses, fed straight into TITAN's Threat Feed.
How research reaches your network.
Gather from everywhere
Over 15 intelligence feeds, government and industry advisories, our own incident response work, and anonymized intelligence from attacks seen across the SkyHelm network.
Separate signal from noise
Researchers work out what's new, what's credible and what actually matters to critical infrastructure organizations.
Turn it into detections
New techniques become detection rules and alert logic for our SOC, so analysts recognize them the moment they appear.
Put it in TITAN
Indicators and ransomware group profiles land in TITAN's threat intelligence, where your team can search them and see whether they match your own alerts and assets.
Look back, not just forward
When something important breaks, we hunt for it in the history already collected, not just in what happens next.
Research you can see for yourself.
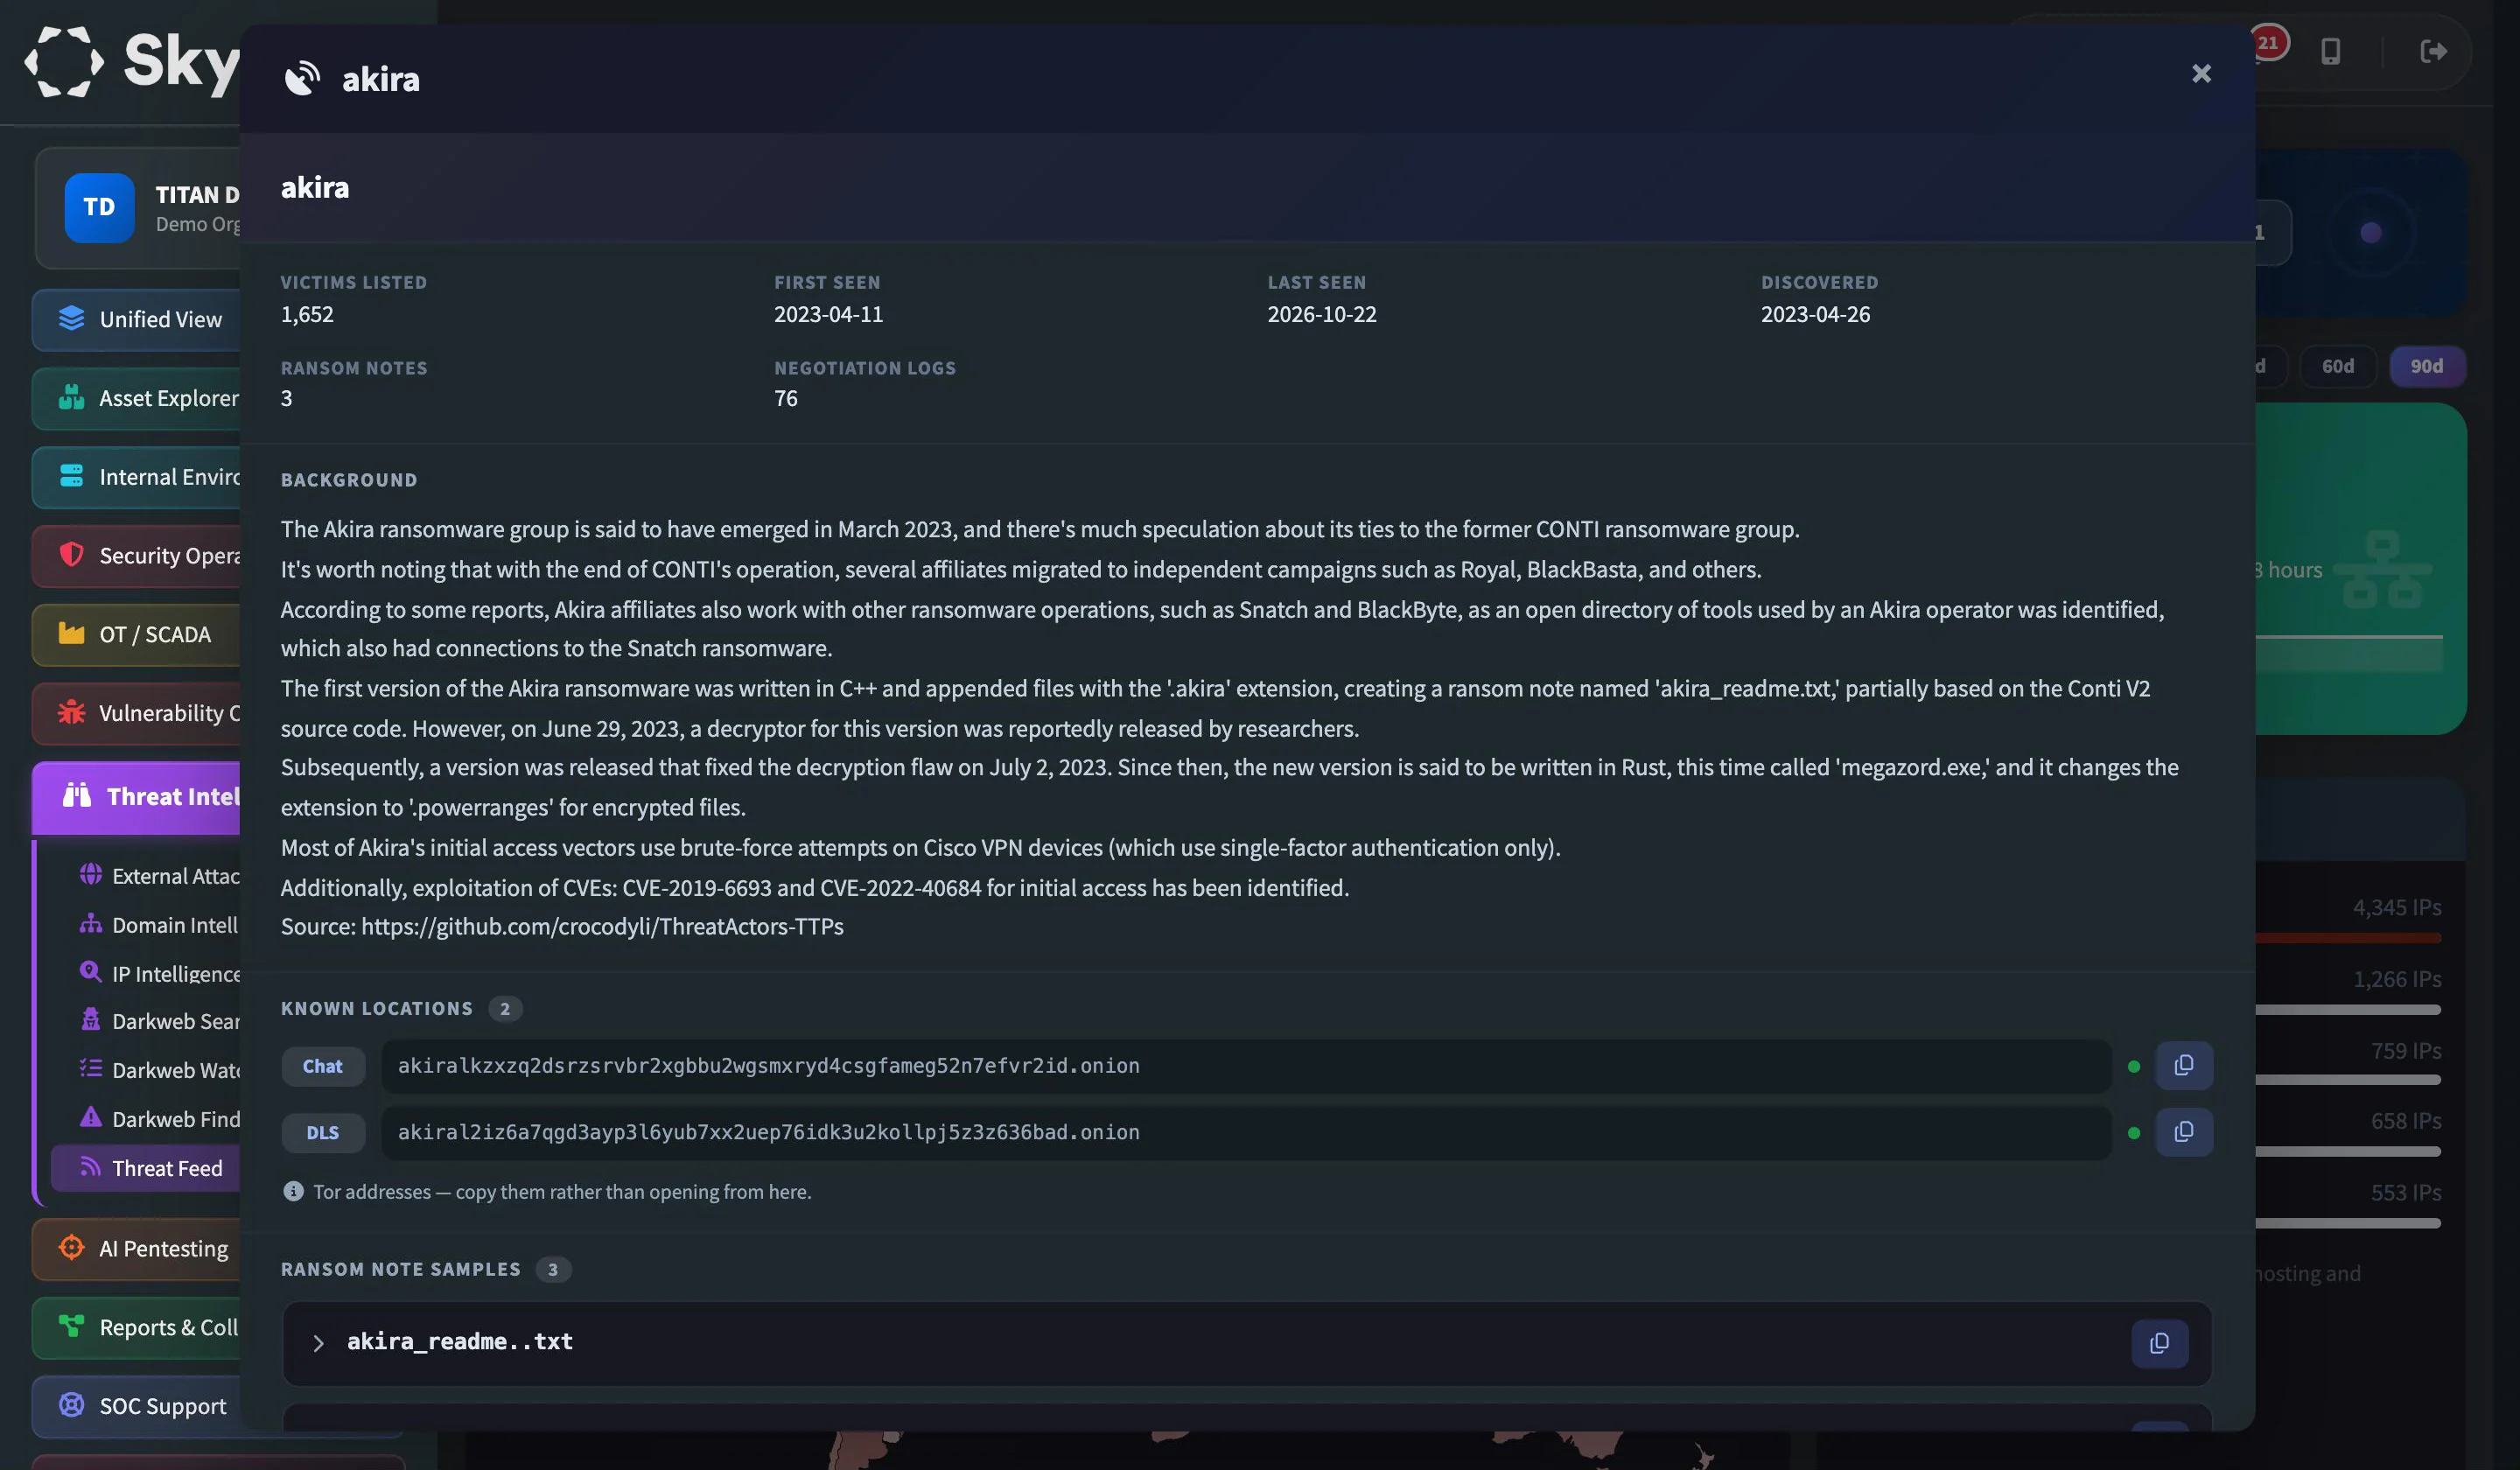
Ransomware group profiles show recent activity, known locations, ransom notes and the vulnerabilities each group exploits.
When something breaks, you hear from us.
When a serious vulnerability or campaign emerges, a long industry report isn't much help. Our advisories tell you what it is, whether you're exposed and what to do, in plain English.
- What's happening, in one paragraph
- Whether your environment is exposed
- What we're already doing about it
- What your team should do, and how urgently
Where threat research shows up.
Put a research team behind your defenses.
See how SkyHelm's threat research feeds TITAN and our 24/7 SOC, and what it would catch on your network.