Threat Intelligence. Know your adversary.
An indicator catalog from 15+ feeds, IP intelligence from 14 sources, and ransomware tracking for utilities.
TITAN turns the world's threat intelligence into something your team can act on: a live indicator catalog built from more than 15 feeds, IP investigations across 14 sources at once, and ransomware tracking focused on energy and utilities, all checked against your own alerts and assets.
Intelligence you can actually use
Raw feeds don't stop attacks. Context does. TITAN connects outside intelligence to what's happening inside your organization.
Threat Feed
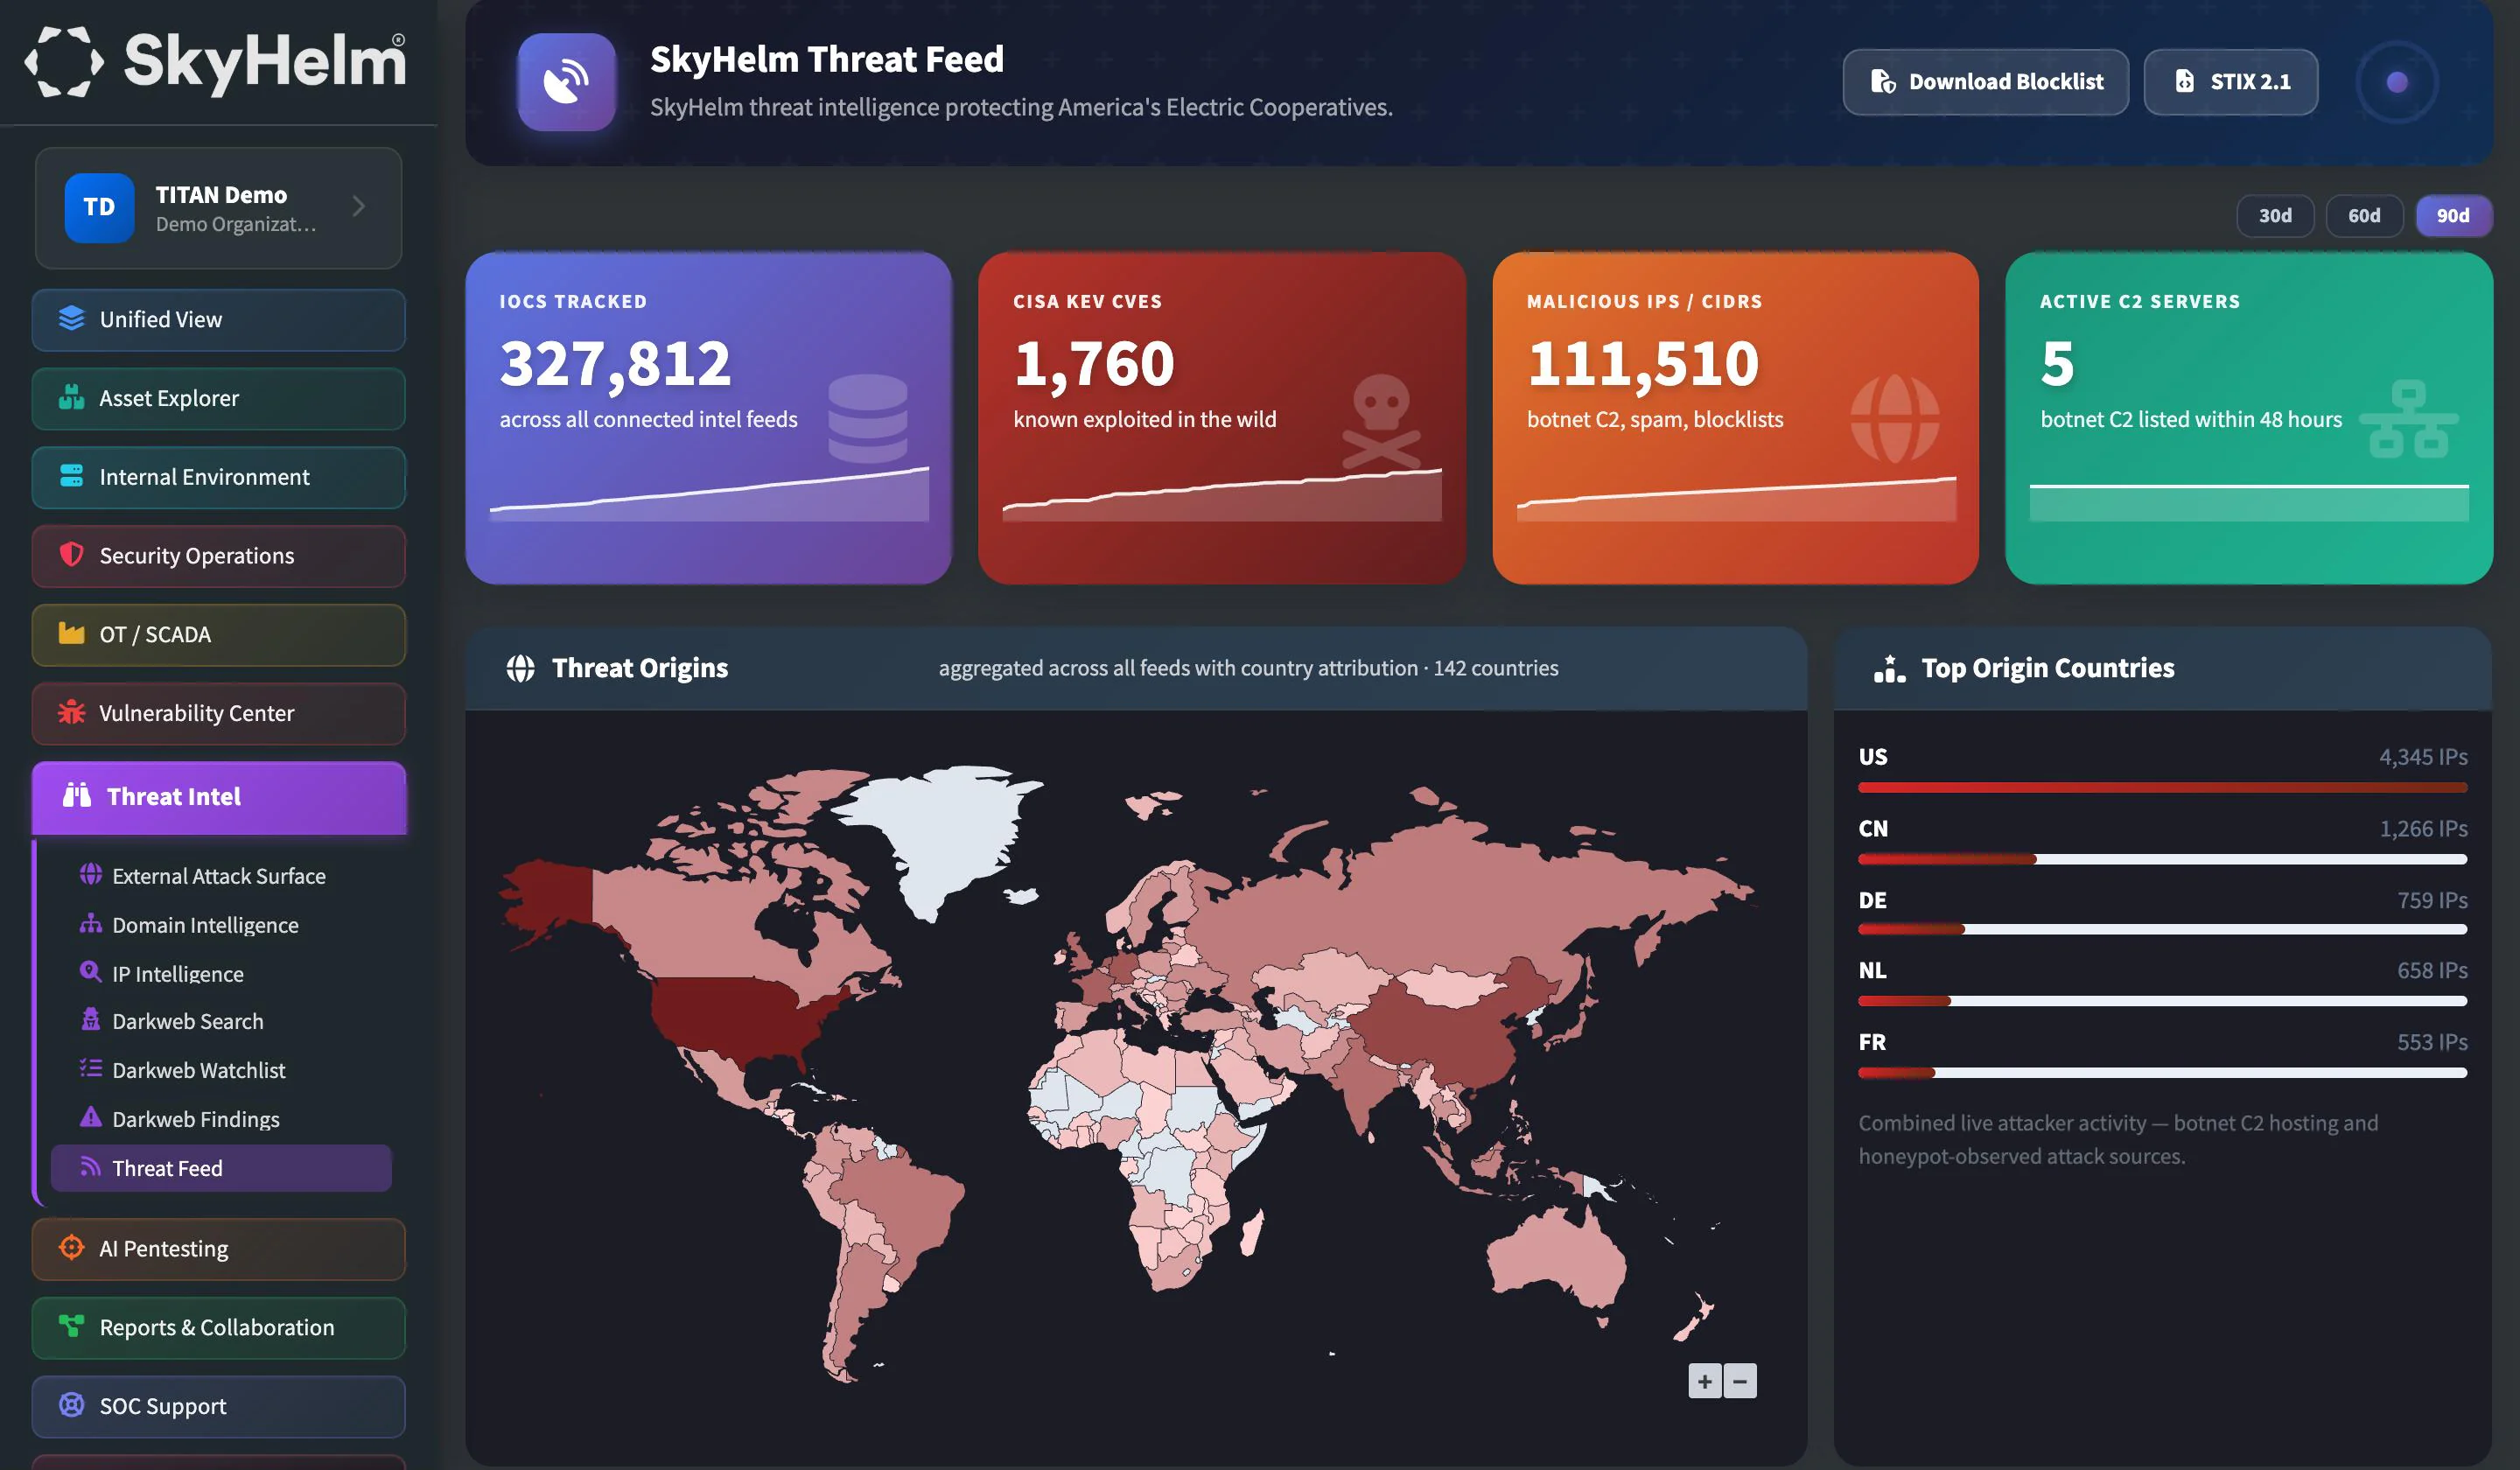
An indicator catalog built from more than 15 threat-intelligence feeds, with daily trend sparklines and a live threat map.
IP Intelligence
Investigate any IP address across 14 sources at once, and see whether it already appears in your own alerts, assets or the indicator catalog. Every lookup is kept in your organization's history.
Community Intelligence
Anonymized intelligence from attacks seen across the SkyHelm network. When a threat hits one organization, the others are ready.
Indicator Watchlist
Pin IPs, domains, hashes and CVEs and be alerted on the page, by email and by mobile push when they show up.
Ransomware Group Profiles
A Ransomware Groups board with a profile for each group: activity, known locations, ransom notes and the vulnerabilities they exploit.
Energy & Utilities Breach Tracking
Recent ransomware breaches in Energy & Utilities across the US, with infostealer credential counts, so you know what's hitting your peers.
Known-Exploited Vulnerabilities
Known-exploited vulnerability tracking with OT/ICS vendor flagging, so the CVEs being used in the wild against utility equipment stand out.
Firewall-Ready Exports
Export indicators as a STIX 2.1 bundle, a plain blocklist or per-panel downloads, ready to load into your firewalls.
Malware Lab & News
Malware Lab and phishing panels with one-click copy of hashes and indicators, plus news feeds from CISA ICS-CERT, CISA advisories, NIST NVD and more.
Inside Threat Intelligence
The views your team will use every day.
An indicator catalog built from 15+ feeds, with daily trends and a live threat map.
The world's threat intelligence, checked against your network
TITAN pulls from public and commercial intelligence sources of every kind, then tells you which of it touches your organization.
Threat Feed
Plus anonymized community intelligence from attacks seen across the SkyHelm network.
IP Intelligence
Every lookup is also checked against your own alerts, your assets and the indicator catalog, and kept in your organization's lookup history.
Everything in Threat Intelligence
13 capabilities, every one included in TITAN.
Threat feed & IP intelligence
13- Co-op-specific threat intelligence and advisories
- Threat Feed: an indicator catalog built from 15+ threat-intelligence feeds
- Anonymized community intelligence from attacks seen across the SkyHelm network
- Indicator Watchlist: pin IPs, domains, hashes and CVEs and be alerted on the page, by email and by mobile push
- Ransomware Groups board with group profiles: activity, known locations, ransom notes and the vulnerabilities they exploit
- Recent ransomware breaches in Energy & Utilities across the US, with infostealer credential counts
- Malware Lab and phishing panels with one-click copy of hashes and indicators
- Known-exploited vulnerability tracking with OT/ICS vendor flagging
- Firewall-ready exports: STIX 2.1 bundle, plain blocklist and per-panel downloads
- Daily trend sparklines and a live threat map
- IP Intelligence: investigate any IP address across 14 sources at once
- IP checks against your own alerts, assets and the indicator catalog, with a lookup history for your organization
- Cybersecurity news feeds from CISA ICS-CERT, CISA advisories, NIST NVD and more
Works hand in hand with
Turn intelligence into action
Schedule a demo and we'll show you how TITAN checks the world's threat intelligence against your own environment, automatically.